Threat hunting · Ransomware detection · Malware analysis
Run the attack, catch it, one bit at a time.
An attacker command run in my own lab, the telemetry it left, and the query that catches it. AI-assisted, human-validated.
Latest issue
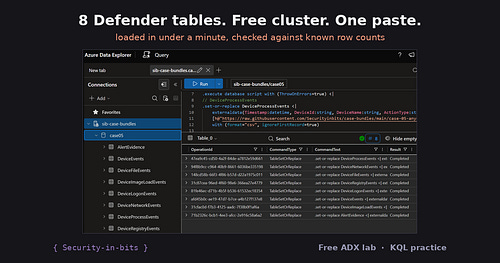 New issueNewsletterLoad Real Defender Telemetry into a Free ADX Cluster in One PasteNo tenant, no Azure subscription, no credit card. Eight MDE tables from a real lab intrusion, loaded with one script, checked against known row counts.newsletter.securityinbits.comRead the issue on Substack