Ayush Anand
Detection engineer and malware analyst. 15+ years defending against malware: reverse engineering at Symantec, then leading malware defense and incident response at a global bank. Now I build detections in my own lab and teach them in public, one bit at a time.
- 15+ years
- GREM
- GCFA
- GDAT
- GCWN
- 3 US patents
- Ex-Symantec
Get the newsletterBrowse the detection index
Now
Writing and teaching
I write the Security in Bits newsletter and run a YouTube channel covering detection engineering, RMM abuse, and ransomware techniques. I turn lab investigations into practical walkthroughs: how the technique works, what evidence it leaves, and how defenders can hunt for it. The newsletter carries the detailed analysis and queries; YouTube shows the investigations and detections in action.
Building and testing in the lab
I run an instrumented home lab with Microsoft Defender for Endpoint, Elastic Security, Velociraptor, Suricata, and Sysmon. I reproduce attacker techniques, collect endpoint and network evidence, and use that telemetry to develop and test detections. My current focus is RMM abuse and the activity leading up to ransomware encryption, including what the tools detect, what they miss, and why.
Read the newsletterWatch on YouTubeExplore detections
Track record
Experience
2018–present
Founder
Security-in-bits
Detection engineering and malware analysis, written up from my own lab.
2017–present
Senior Vice President, Cyber Defense Senior Manager
A global bank
Lead a multi-region team defending against malware and phishing; incident bridge lead for malware events, from containment to eradication.
2011–2017
Senior Malware Analyst
Symantec, Security Technology and Response (STAR), Singapore and Pune
Targeted-attack malware analysis, YARA and IPS signatures, published threat research.
Education
Bachelor of Engineering, Computer
University of Pune · 2005–2009
Certifications (6)
Certified Malwareless Adversarial Operator (CMAO)
ZephrSec
Show credential: Certified Malwareless Adversarial Operator (CMAO) (opens in a new tab)
GIAC Defending Advanced Threats (GDAT), 94%
GIAC
Show credential: GIAC Defending Advanced Threats (GDAT), 94% (opens in a new tab)
Microsoft Certified: Azure Fundamentals
Microsoft
Show credential: Microsoft Certified: Azure Fundamentals (opens in a new tab)GIAC Reverse Engineering Malware (GREM), 96%
GIAC
Show credential: GIAC Reverse Engineering Malware (GREM), 96% (opens in a new tab)GIAC Certified Windows Security Administrator (GCWN), 89%
GIAC
Show credential: GIAC Certified Windows Security Administrator (GCWN), 89% (opens in a new tab)GIAC Certified Forensic Analyst (GCFA), 91%
GIAC
Show credential: GIAC Certified Forensic Analyst (GCFA), 91% (opens in a new tab)

Patents
3 granted · 2 published applications
Granted
System and method for identifying and analyzing computing device intrusions using artificial intelligence powered virtualized environment
US 12,689,633 B2
View patent: System and method for identifying and analyzing computing device intrusions using artificial intelligence powered virtualized environment (opens in a new tab)Published application
System and method for detection and prevention of computing device intrusion vectors using AI
US 2026/0052170 A1
View patent: System and method for detection and prevention of computing device intrusion vectors using AI (opens in a new tab)Published application
System and method for computing device intrusion detection via machine learning for interaction data analysis
US 2026/0030360 A1
View patent: System and method for computing device intrusion detection via machine learning for interaction data analysis (opens in a new tab)Granted
Dynamic event securitization and neural network analysis system
US 11,722,524 B2
View patent: Dynamic event securitization and neural network analysis system (opens in a new tab)Granted
Dynamic event securitization and neural network analysis system
US 11,635,964 B2
View patent: Dynamic event securitization and neural network analysis system (opens in a new tab)
Publications (4)
Russian bank employees received fake job offers in targeted email attack
Symantec Security Response (archived)
Read publication: Russian bank employees received fake job offers in targeted email attack (opens in a new tab)Organizations must respond to increasing threat of ransomware
Symantec Security Response (archived)
Read publication: Organizations must respond to increasing threat of ransomware (opens in a new tab)MySQL servers hijacked with malware to perform DDoS attacks
Symantec Security Response (archived)
Read publication: MySQL servers hijacked with malware to perform DDoS attacks (opens in a new tab)Ramnit cybercrime group hit by major law enforcement operation
Symantec Security Response (archived)
Read publication: Ramnit cybercrime group hit by major law enforcement operation (opens in a new tab)
Since 2018: every post on this site and the newsletter.
Courses and training (9)
Sliver C2: Pentesting and Evasion
Kairos Sec
View completion: Sliver C2: Pentesting and Evasion (opens in a new tab)
Introduction to Model Context Protocol
Anthropic
View completion: Introduction to Model Context Protocol (opens in a new tab)
Advanced Hands-On KQL for Threat Hunting and Detection Engineering from Scratch
Blu Raven Academy
Credential ID: 699076ee9d90316d2b0bf581
View completion: Advanced Hands-On KQL for Threat Hunting and Detection Engineering from Scratch (opens in a new tab)
Practical Threat Hunting
Mandiant Academy
26–29 January 2026 · 24 hours
View certificate: Practical Threat Hunting (opens in a new tab)
AI Engineer Core Track: LLM Engineering, RAG, QLoRA, Agents
Udemy
View completion: AI Engineer Core Track: LLM Engineering, RAG, QLoRA, Agents (opens in a new tab)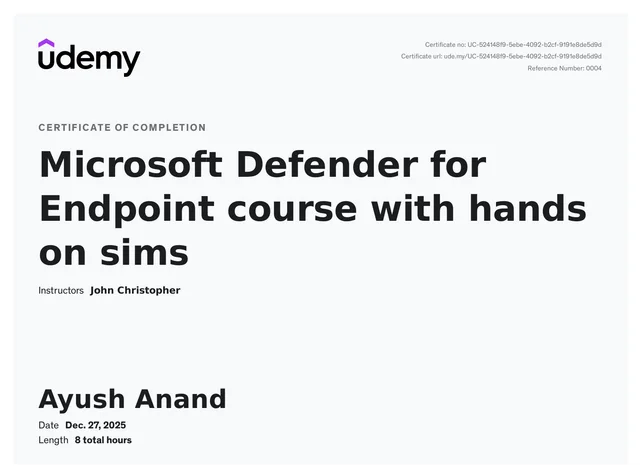
Microsoft Defender for Endpoint with hands on
Udemy
View completion: Microsoft Defender for Endpoint with hands on (opens in a new tab)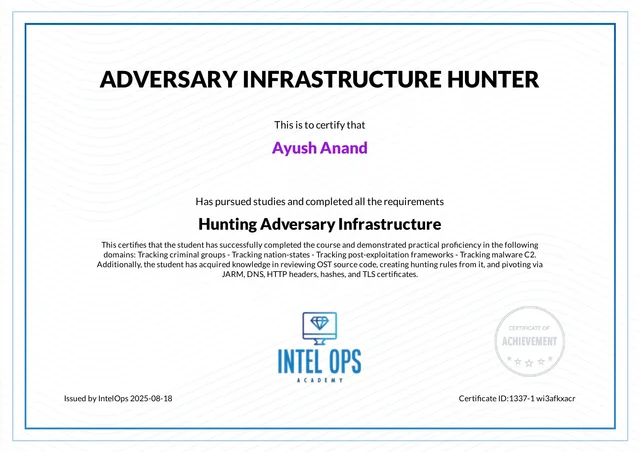
Hunting Adversary Infrastructure
Intel-Ops
View completion: Hunting Adversary Infrastructure (opens in a new tab)
Supervised Machine Learning: Regression and Classification
DeepLearning.AI
View completion: Supervised Machine Learning: Regression and Classification (opens in a new tab)
Contact
Email contact@securityinbits.com. DMs on X and LinkedIn are fine too, and often faster. Corrections are welcome and acted on.
Last reviewed .