Threat Hunting
10 items, newest first, including 6 newsletter issues.
Newsletter
Load Real Defender Telemetry into a Free ADX Cluster in One Paste
No tenant, no Azure subscription, no credit card. Eight MDE tables from a real lab intrusion, loaded with one script, checked against known row counts.
Newsletter
Watch it run: the network scan 45+ ransomware groups use
Catch the scan before the encryption. On real lab telemetry, in Defender and Elastic.
Newsletter
ScreenConnect RMM Abuse: The Cloud Client Gets In, The Self-Hosted One Stays
Two real samples in my lab dropped two implants on one host. One vendor-signed and loud, one self-hosted and configured to be invisible. Here is how to hunt both.
Newsletter
32 Ransomware Groups Abuse AnyDesk. Your EDR Sees a Legit Tool
Is That AnyDesk Legit or Planted? A Lab-Validated Hunt
Newsletter
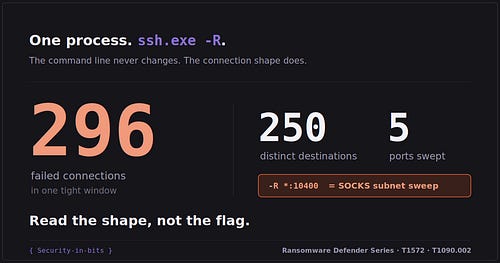
Detecting Reverse SSH SOCKS Tunnels: Separating Benign -R From Akira Pivoting
Two of these three ssh.exe -R sessions are benign. The telemetry that separates them, and the one case it can't.
Newsletter
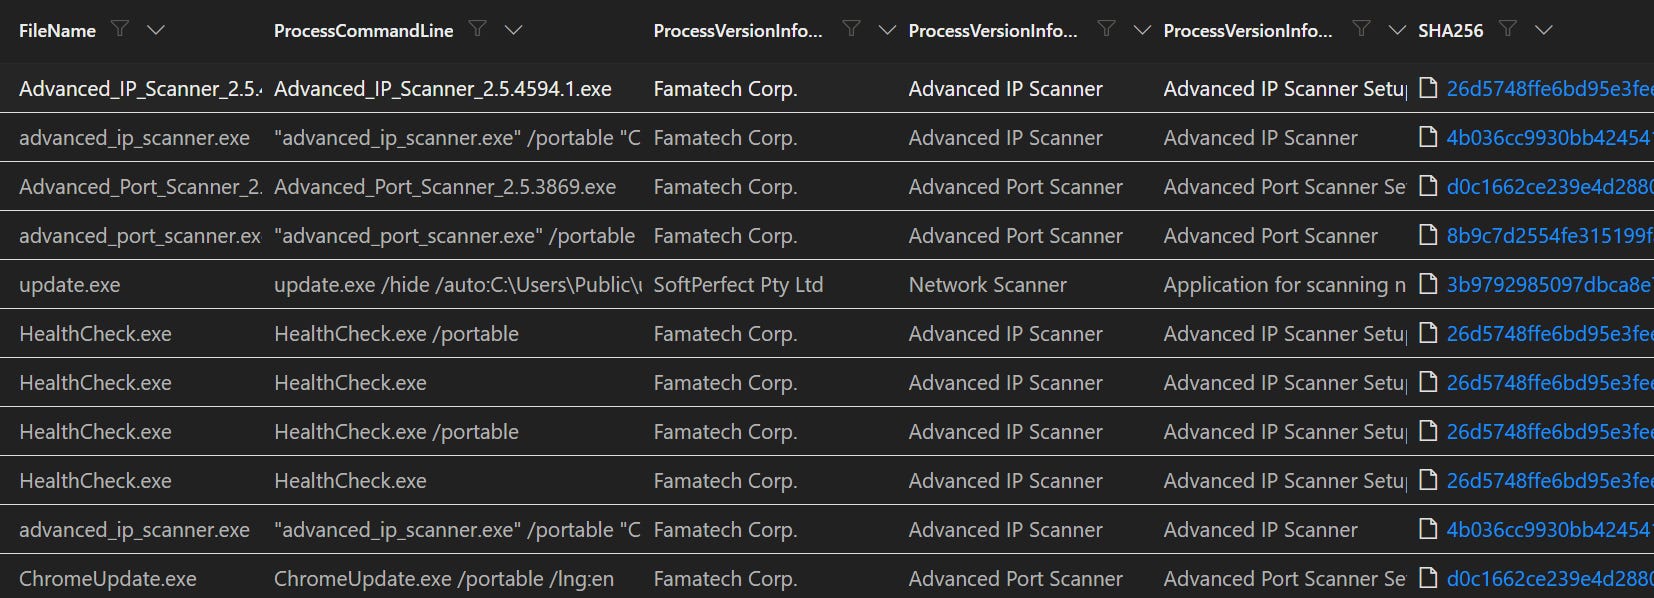
Hunt Ransomware Before It Encrypts: The Three Tools 45+ Gangs Reach For
As of May 2026, 3,734 organizations have been hit by ransomware.

wbadmin NTDS.dit dump detection for Domain Controllers
wbadmin NTDS.dit dump detection for DCs using Sigma, MDE KQL, and Elastic plus fast triage with Backup logs.

How to set up Sigma rules for Elasticsearch SIEM
End-to-end workflow to convert Sigma rules into Elasticsearch SIEM detection rules using sigma-cli, Elasticsearch backend, and Kibana NDJSON imports.

Discovery using nltest, net and whoami
Learn how adversaries run nltest, whoami, and net for AD recon, with ready Sigma detections and process context to detect and triage.

LSASS Dump via comsvcs.dll: Defender Detection Guide
Detect LSASS dump with comsvcs.dll and rundll32. Clear command breakdown and Sigma mappings for Defender and Elastic