T1543.003: Windows Service
ATT&CK technique, covered in 2 newsletter issues · attack.mitre.org
Newsletter
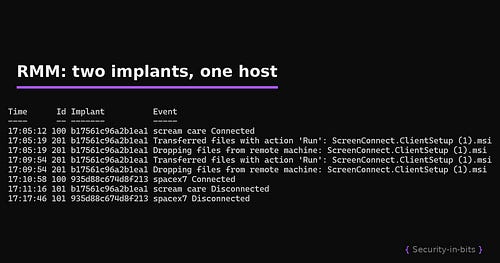
ScreenConnect RMM Abuse: The Cloud Client Gets In, The Self-Hosted One Stays
Two real samples in my lab dropped two implants on one host. One vendor-signed and loud, one self-hosted and configured to be invisible. Here is how to hunt both.
Newsletter
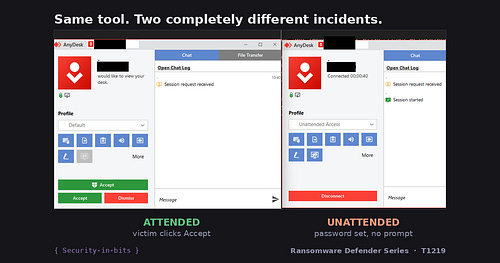
32 Ransomware Groups Abuse AnyDesk. Your EDR Sees a Legit Tool
Is That AnyDesk Legit or Planted? A Lab-Validated Hunt