#Java
4 posts

Interesting tactic by Ratty & Adwind for distribution of JAR appended to signed MSI – CVE-2020-1464
This article discusses an interesting tactic (CVE-2020-1464) actively used by different Java RAT malware authors like Ratty & Adwind to distribute malicious JAR appended to signed MSI files.
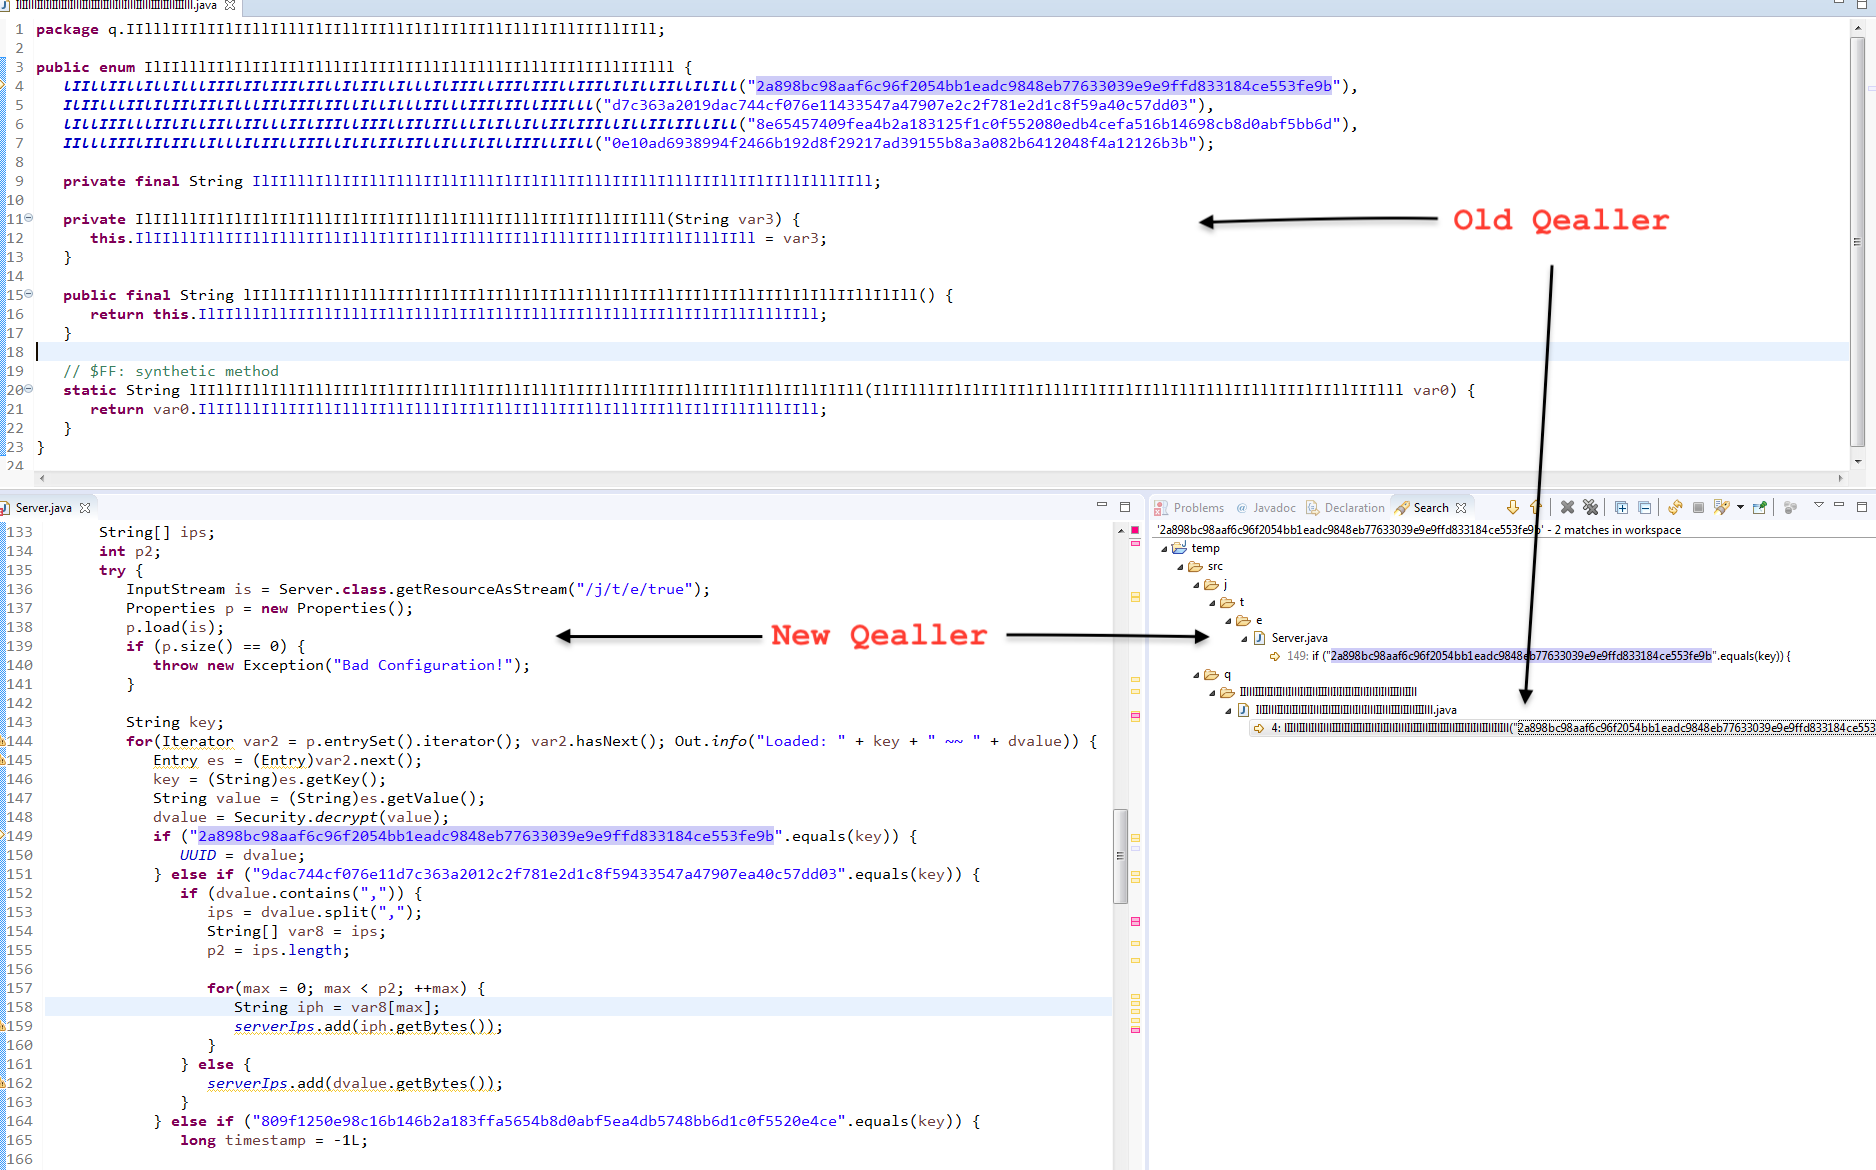
Similarity between Qealler/Pyrogenic variants -Part 0x3
In this last part, we will compare Old Qealler with new Qealler/Pyrogenic variant based on static code analysis.
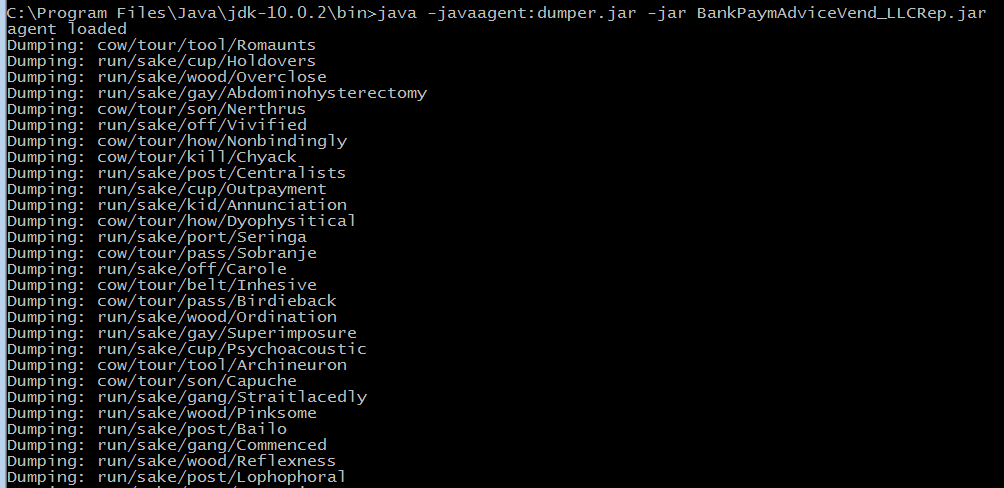
Unpacking Pyrogenic/Qealler using Java agent -Part 0x2
We will learn how and when we can use Java agent to quickly unpack the Pyrogenic/Qealler Infostealer.

Qealler Infostealer static analysis – Part 0x1
Pyrogenic/Qealler is heavily obfuscated Java based Infostealer which is quiet active based on ANY.RUN and this post will focus on Pyrogenic Infostealer static analysis


